

Essential Insights
-
Threat Overview: Google identifies a financially motivated threat group named UNC6040, specializing in voice phishing (vishing) to access organizations’ Salesforce accounts for data theft and extortion.
-
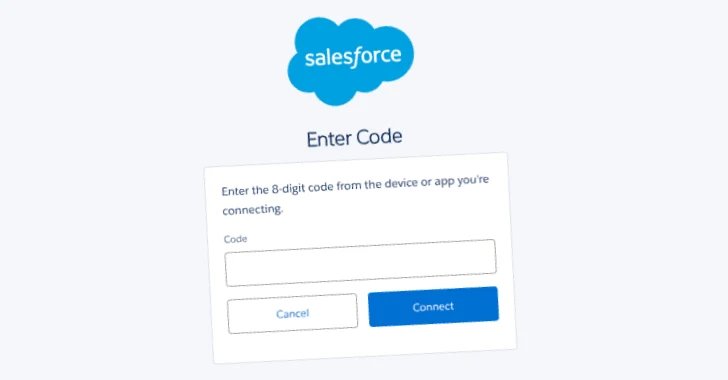
Deceptive Tactics: UNC6040 uses social engineering by impersonating IT support personnel, convincing employees to authorize a modified Salesforce Data Loader app that allows unauthorized access to sensitive information.
-
Data Exfiltration and Lateral Movement: The attackers not only steal data from Salesforce but also move laterally within the victim’s network to target other platforms, with extortion attempts following months after initial breaches.
- Increased Targeting of IT Staff: The campaign highlights a growing trend in targeting IT support personnel as gateways for breaches, emphasizing the need for heightened awareness in organizations to combat sophisticated social engineering attacks.
Underlying Problem
On June 4, 2025, Google revealed a troubling account of a financially motivated threat group, identified as UNC6040. This nefarious cluster specializes in voice phishing, or vishing, specifically targeting organizations’ Salesforce environments for extensive data theft and subsequent extortion. Operating under the guise of IT support personnel, UNC6040’s sophisticated tactics involve convincing employees to authorize a malicious version of Salesforce’s Data Loader, cleverly disguised as a legitimate application (e.g., “My Ticket Portal”). By exploiting social engineering techniques and manipulating trusted channels, this group successfully gains unauthorized access to sensitive credentials, facilitating lateral movement across networks to siphon data from multiple platforms, including Okta and Microsoft 365.
Reporting on this alarming development, Google’s Threat Intelligence Group outlined the operational patterns of UNC6040, linking them to the online criminal collective known as The Com. The report highlights the increasing efficacy of these vishing attacks and underscores the inherent vulnerabilities of organizations that depend on personal interactions for security protocols. Salesforce has also acknowledged the threat, warning its customers of the rising exploitation tactics targeting employees and third-party support workers. As the specter of extortion looms—airing claims of affiliation with notorious groups like ShinyHunters—it becomes clear that the cybersecurity landscape continues to evolve, necessitating heightened vigilance among organizations and employees alike.
Risk Summary
The rise of sophisticated voice phishing (vishing) campaigns, notably exemplified by the UNC6040 threat cluster, poses significant risks not only to directly targeted organizations but also to other businesses, users, and affiliated entities. As hackers impersonate IT personnel to extract sensitive information via social engineering, the potential for widespread data breaches escalates dramatically. This interconnected threat landscape enables attackers to exploit compromised environments, spreading their reach laterally across networks, thereby jeopardizing the integrity of related systems like those managed by Okta, Workplace, and Microsoft 365. The resultant data theft can lead to extensive financial losses, erode customer trust, and catalyze a cascade of extortion demands, placing undue pressure on multiple organizations within the ecosystem. Consequently, the ripple effects of such breaches may destabilize not only the directly affected entities but also challenge the operational viability of partners and clients, emphasizing the critical need for heightened vigilance and proactive cybersecurity measures across all sectors.
Possible Action Plan
Timely remediation is essential in safeguarding sensitive data and maintaining trust, particularly in light of the recent exposure of the vishing group UNC6040 targeting Salesforce through a counterfeit Data Loader application.
Mitigation Strategies
- User Awareness Training: Educate employees on recognizing phishing attempts and suspicious app downloads.
- Multi-Factor Authentication: Implement MFA to enhance security for user accounts within Salesforce.
- App Vetting Protocols: Establish strict criteria for app installation and usage, ensuring all tools are verified.
- Incident Response Plan: Develop a comprehensive response plan for addressing data breaches, including communication strategies.
- Regular Security Audits: Conduct routine assessments to identify vulnerabilities in systems and immediately address them.
- Threat Intelligence Sharing: Collaborate with cybersecurity communities to stay informed about emerging threats and tactics.
NIST CSF Guidance
The NIST Cybersecurity Framework (CSF) emphasizes the importance of identifying, protecting, detecting, responding, and recovering from cyber threats. Specifically, organizations should refer to the NIST SP 800-53: "Security and Privacy Controls for Information Systems and Organizations" for a deeper dive into effective controls and best practices. Implementing these measures aids in establishing a resilient cybersecurity infrastructure that effectively mitigates risks associated with evolving threats.
Stay Ahead in Cybersecurity
Explore career growth and education via Careers & Learning, or dive into Compliance essentials.
Explore engineering-led approaches to digital security at IEEE Cybersecurity.
Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.
Cyberattacks-V1
