

Essential Insights
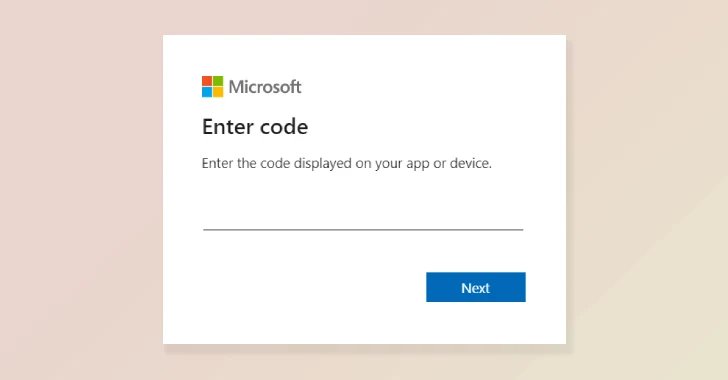
- Amazon identified and disrupted a Russia-linked APT29 campaign using compromised websites to redirect users and trick them into authorizing attacker-controlled devices via Microsoft’s device code authentication.
- APT29, a state-sponsored group tied to Russia’s SVR, has intensified its tactics, employing phishing, RDP exploits, and website injections to steal credentials and gather intelligence, especially targeting Microsoft 365 accounts.
- The threat actors used sophisticated evasion techniques like Base64 encoding, cookies, and infrastructure shifts to evade detection and maintain persistence despite mitigation efforts.
- Amazon’s threat intelligence team highlighted the group’s evolving operations and ongoing efforts to scale their campaigns for broader intelligence collection, despite ongoing disruptions.
What’s the Problem?
In August 2025, Amazon reported that a sophisticated cyber operation linked to the Russian intelligence agency, specifically the APT29 hacking group, had been actively targeting internet users through an elaborate watering hole campaign. This campaign involved hijacked legitimate websites, which were clandestinely infected with malicious JavaScript. When visitors accessed these compromised sites, they were redirected to fake verification pages that mimicked legitimate cloud security interfaces, designed to trick users into granting access to their Microsoft accounts by entering device codes controlled by the attackers. The motivation behind this campaign appears to be for intelligence gathering, aiming to harvest credentials and obtain sensitive information from targeted individuals and organizations, particularly those with valuable government or corporate data. This ongoing operation highlights the evolving sophistication of APT29’s tactics, including the use of evasive techniques such as code obfuscation and infrastructure shifts, even after intervention efforts by threat intelligence teams.
The attack was reported by Amazon’s Chief Information Security Officer, CJ Moses, and is part of a broader pattern of malicious activity attributed to APT29—which has also been linked to other efforts, such as deploying malicious RDP configurations against Ukrainian targets and exploiting Google account features to access email data. These activities reveal the group’s strategic shift toward broader, more opportunistic campaigns that seek to expand their cyber espionage reach by exploiting trusted websites and manipulating users into unwittingly participating in their espionage efforts. Despite concerted efforts to disrupt their infrastructure—such as moving their operations from Amazon Web Services to alternative cloud providers—the threat actors continue to adapt and pursue their objectives, underscoring the persistent danger posed by state-backed cyber espionage entities.
Critical Concerns
Cyber risks posed by state-sponsored advanced persistent threat (APT) groups like Russia-linked APT29 exemplify the escalating sophistication and multifaceted nature of modern cyber threats, significantly impacting both organizational and national security. These threat actors employ a diverse arsenal of tactics—including watering hole campaigns, phishing (notably device code and device join phishing), malicious infrastructure exploitation, and evasion techniques such as code obfuscation—to compromise targets, exfiltrate sensitive data, and gather intelligence. Their operations, which often involve compromising legitimate websites and mimicking trusted platforms like Cloudflare, underscore the deceptive strategies used to exploit vulnerabilities, deceive users, and bypass defenses. The persistent activity of such groups, despite disruptions, indicates a relentless evolution aimed at broadening their intelligence-gathering scope, jeopardizing data integrity, confidentiality, and operational continuity across sectors. This environment mandates heightened vigilance, robust security protocols, and adaptive defenses to mitigate the profound and persistent impact of these advanced cyber risks.
Possible Next Steps
In the rapidly evolving landscape of cybersecurity threats, addressing vulnerabilities swiftly is essential to prevent substantial damage, especially when advanced persistent threats like APT29 exploit sophisticated methods such as watering hole campaigns abusing Microsoft device code authentication. Prompt remediation not only minimizes potential data breaches and system compromises but also bolsters an organization’s defense posture by closing security gaps before attackers can fully execute their plans.
Mitigation Strategies
-
Patch Systems: Deploy the latest security updates and patches to fix known vulnerabilities related to Microsoft device code authentication.
-
Network Monitoring: Implement advanced intrusion detection and prevention systems to identify unusual network traffic indicative of malicious activity.
-
Access Controls: Enforce strict access controls and multi-factor authentication to reduce the risk of credential misuse.
-
Threat Intelligence: Incorporate threat intelligence feeds that specifically monitor APT29 activities and indicators.
- User Education: Conduct training to improve awareness about phishing tactics and suspicious links related to watering hole exploits.
Remediation Actions
-
Incident Response: Initiate an immediate incident response plan to contain and investigate the breach, if detected.
-
System Isolation: Isolate affected systems to prevent lateral movement within the network.
-
Credential Reset: Reset compromised accounts and update credentials associated with Microsoft device authentication.
-
Threat Hunting: Conduct proactive threat hunting to uncover hidden malicious activities or malware.
- Continuous Monitoring: Enhance ongoing monitoring for signs of compromise and anomalous behavior post-remediation.
Advance Your Cyber Knowledge
Discover cutting-edge developments in Emerging Tech and industry Insights.
Explore engineering-led approaches to digital security at IEEE Cybersecurity.
Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.
Cyberattacks-V1
