
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Hackers Steal $2.7M from Polymarket Traders via Hijacked Script

November 1, 2026

North Korean Hackers Behind $6B+ Binance Attack

November 1, 2026

Could Keyless Pseudonymization Help Stop Ransomware?

November 1, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Shifting the Balance: U.S. Cyber Strategy Must Burden Adversaries
Uncategorized

Shifting the Balance: U.S. Cyber Strategy Must Burden Adversaries

Staff WriterBy Staff WriterSeptember 10, 2025No Comments2 Mins Read7 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Essential Insights

  1. Whole-of-Nation Approach: National Cyber Director Sean Cairncross emphasized an aggressive, coordinated strategy to combat cyber threats from authoritarian regimes, especially China.

  2. Addressing Vulnerabilities: Cairncross highlighted the current patchwork of U.S. cyber defenses and the need for a proactive, unified stance to protect against espionage and cyberattacks.

  3. Immediate Priorities: Key focuses include extending the Cybersecurity Information Sharing Act (CISA), upgrading outdated federal technology, and encouraging the tech sector to adopt secure design principles.

  4. Strategic Vision: Cairncross advocates for a comprehensive cyber policy that integrates offensive and defensive measures to enhance national security and resilience against cyber threats.

Adopting a New Posture

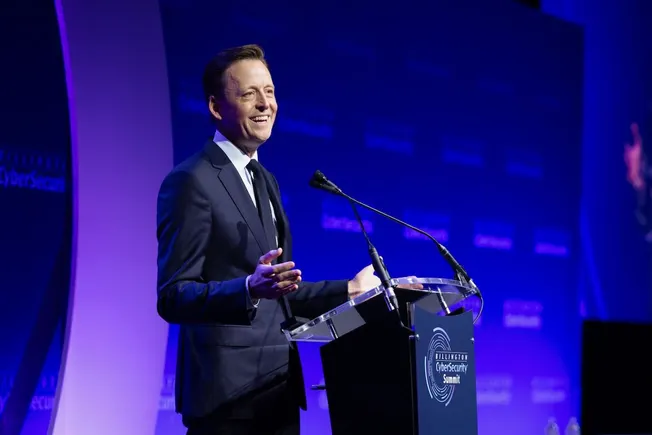
National Cyber Director Sean Cairncross emphasizes a need for an aggressive response to cyber threats from adversaries like China. In his recent address, he highlighted the persistent cyberattacks targeting American networks. These attacks include espionage, ransomware, and intellectual property theft. Given the decentralized nature of U.S. governance, responses often lack coordination. Therefore, Cairncross argues that it is time to shift the burden of risk from Americans back toward adversaries.

This approach requires a whole-of-nation strategy. Stakeholders must align their cyber capabilities to create a unified front. Cairncross insists the U.S. possesses the tools necessary to combat these threats effectively. By sending a clear signal to adversaries, the U.S. can impose consequences for unacceptable behaviors. The urgency is palpable; outdated government technology fuels vulnerabilities. Thus, upgrading these systems must be a priority to safeguard against future attacks.

Policy and Collaboration

Cairncross identified key actions to reinforce cybersecurity. First, he requests an extension of the Cybersecurity Information Sharing Act. This act plays a crucial role in enabling the private sector to share threat information. Collaborative efforts among federal, state, and local governments can strengthen national defenses. Second, modernizing technology in federal agencies is essential. Many agencies still rely on aging systems that cannot withstand sophisticated attacks.

Moreover, he urges the tech sector to adopt secure design standards. Implementing privacy by design is equally important. Lastly, streamlining regulations can encourage compliance without adding unnecessary burdens. By cultivating a strategic cyber environment, the U.S. can advance its national interests. This coordinated effort can serve as a model for balancing innovation and security in our digital future.

Expand Your Tech Knowledge

Explore the future of technology with our detailed insights on Artificial Intelligence.

Discover archived knowledge and digital history on the Internet Archive.

Cybersecurity-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleJaguar Land Rover Faces Data Breach from Cyberattack
Next Article Syniverse Elevates Justin Dellaportas to EVP Role, Strengthening Leadership in CIS & DSO
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Hackers Steal $2.7M from Polymarket Traders via Hijacked Script

November 1, 2026

Chainalysis Breach Exposes Customer Identity Data

October 31, 2026

Binance Breach Hits $6.3B in Assets; Nearly $3B Frozen

October 30, 2026

Comments are closed.

Latest Posts

North Korean Hackers Behind $6B+ Binance Attack

November 1, 2026

Could Keyless Pseudonymization Help Stop Ransomware?

November 1, 2026

Millions of PHP2Shell Exploit Attempts Target Devices to Spread Mirai

October 31, 2026

Syrian Hacker Who Served Assad Gets 42 Months in U.S. Prison

October 31, 2026
Don't Miss

Hackers Steal $2.7M from Polymarket Traders via Hijacked Script

By Staff WriterNovember 1, 2026

Quick Takeaways A compromised DebugBear script injected malicious code into Polymarket after DebugBear’s DNS was…

Chainalysis Breach Exposes Customer Identity Data

October 31, 2026

Binance Breach Hits $6.3B in Assets; Nearly $3B Frozen

October 30, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Hackers Steal $2.7M from Polymarket Traders via Hijacked Script
  • North Korean Hackers Behind $6B+ Binance Attack

  • Could Keyless Pseudonymization Help Stop Ransomware?

  • Millions of PHP2Shell Exploit Attempts Target Devices to Spread Mirai
  • Syrian Hacker Who Served Assad Gets 42 Months in U.S. Prison
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Hackers Steal $2.7M from Polymarket Traders via Hijacked Script

November 1, 2026

North Korean Hackers Behind $6B+ Binance Attack

November 1, 2026

Could Keyless Pseudonymization Help Stop Ransomware?

November 1, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026349 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026228 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026217 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.