

Quick Takeaways
- Jaguar Land Rover’s production halt due to a cyber attack has been extended until October 1, 2025, highlighting vulnerabilities in complex supply chains and ongoing efforts to safely restore operations.
- The UK government officials, including Industry Minister Chris McDonald, are actively supporting JLR and engaging with supply chain workers affected by the disruption, which may last into November.
- The cyber incident has broader implications across the automotive industry, prompting companies like Stellantis to respond to unauthorized access on third-party platforms, emphasizing vulnerabilities in third-party integrations.
- Industry experts warn that trust in SaaS platforms and third-party tokens presents systemic risks, with attackers exploiting these to access enterprise systems, underscoring the need for proactive security measures.
What’s the Problem?
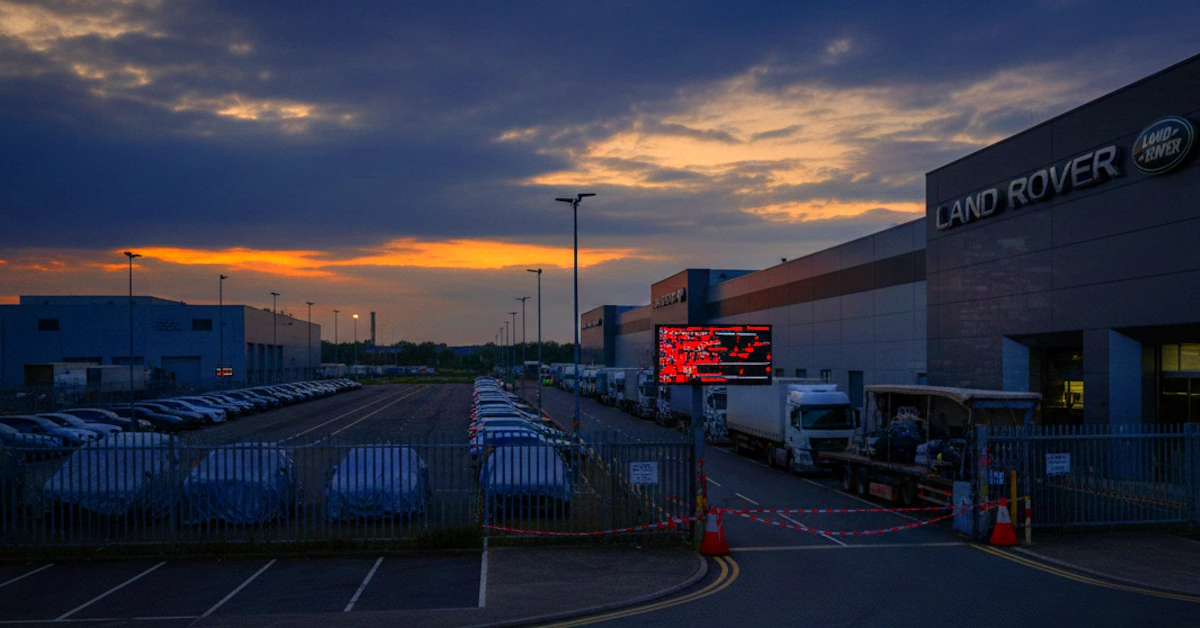
Jaguar Land Rover (JLR) has extended its production shutdown until October 1, 2025, following a cyberattack that began on August 31. This malicious breach has not only halted vehicle manufacturing but has also caused disruptions across the supply chain, impacting workers’ wages and prompting government officials, including industry Minister Chris McDonald, to visit and assess the situation. The company’s teams are working tirelessly with cybersecurity experts, law enforcement, and the National Cyber Security Centre to ensure a safe restart, amidst ongoing investigations. Meanwhile, the UK government is actively engaging with JLR and suppliers to mitigate the economic and operational impacts of this attack, highlighting how deeply interconnected and fragile supply chains are against cyber threats.
In a broader context of rising cyber risks within the automotive industry, other companies like Stellantis and Bridgestone have also experienced security breaches involving unauthorized access to third-party platforms and disrupted operations. Stellantis promptly responded to a data breach affecting customer service, emphasizing the importance of safeguarding third-party integrations, while Bridgestone is recovering from a separate attack that forced it to halt production at multiple plants. Industry experts warn that these incidents reveal systemic vulnerabilities in digital supply chains, where attackers exploit trust between enterprise platforms, and stress the importance of proactive security measures to prevent significant operational and financial damage.
What’s at Stake?
Cyber risks pose significant threats to industrial sectors, exemplified by Jaguar Land Rover’s extended production halt due to a cyberattack, which severely disrupts supply chains, causes economic losses, and affects workers’ livelihoods, underscoring the vulnerability of complex interconnected systems. These incidents prompt government interventions, as seen with UK officials visiting affected companies and engaging with suppliers to support recovery efforts. The risks extend beyond manufacturing; third-party service breaches, such as Stellantis’ incident, highlight how attackers exploit vulnerabilities in external platforms—targeting trust relationships within enterprise ecosystems—leading to data exposure that’s often limited but undermines customer trust and operational integrity. The recurring pattern of such breaches reveals systemic vulnerabilities, emphasizing that defending modern organizations requires proactive measures to identify and mitigate weaknesses within third-party integrations and trust boundaries, as delays in response or reliance on outdated safeguards leave organizations exposed to cascading operational and reputational damage.
Possible Actions
Timely remediation is crucial in this situation because delays could further disrupt production, deepen supply chain issues, and threaten the company’s financial stability while also impacting consumers and partners.
Mitigation Strategies:
Enhanced Cybersecurity:
Implement immediate, robust security protocols such as updated firewalls, intrusion detection systems, and regular vulnerability assessments to prevent further attacks.
Incident Response Activation:
Activate a dedicated cyber incident response team to identify, contain, and eradicate the malicious breach swiftly.
Supply Chain Coordination:
Work closely with suppliers and logistics providers to find alternative routes and sources, minimizing production downtime.
Communication Protocols:
Maintain transparent communication with stakeholders, including the UK government, employees, suppliers, and customers, to manage expectations and provide updates.
Operational Recovery:
Develop and execute a detailed recovery plan that includes restoring affected systems, data, and processes with minimal downtime.
Government Collaboration:
Engage with government agencies for support, intelligence sharing, and potential resources to bolster cybersecurity defenses.
Contingency Planning:
Prepare contingency procedures such as backup manufacturing plans or temporary outsourcing to maintain production levels.
Employee Training:
Provide ongoing cybersecurity awareness and response training to employees to help prevent future incidents.
Legal and Compliance Measures:
Ensure response measures comply with relevant legal, cybersecurity, and data privacy regulations to mitigate legal risks.
Continue Your Cyber Journey
Discover cutting-edge developments in Emerging Tech and industry Insights.
Learn more about global cybersecurity standards through the NIST Cybersecurity Framework.
Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.
Cyberattacks-V1
