
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

WordPress Backdoor Reinstates via Files, Database, Shared Memory

October 1, 2026

Attackers Exploit ScreenConnect for Remote Access Breaching

October 1, 2026

MetaMask breach targets Ethereum validator security vulnerabilities

October 1, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Unlocking the Danger: How Vulnerabilities in Cognex Industrial Cameras Open Doors for Hacking
Cybercrime and Ransomware

Unlocking the Danger: How Vulnerabilities in Cognex Industrial Cameras Open Doors for Hacking

Staff WriterBy Staff WriterSeptember 26, 2025No Comments4 Mins Read7 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Top Highlights

  1. Several Cognex industrial cameras (In-Sight series) are affected by high-severity vulnerabilities such as hardcoded passwords, privilege escalation, and credential interception, but no patches will be issued due to their legacy status.
  2. The vulnerabilities can be exploited by attackers who gain network access, enabling man-in-the-middle attacks, unauthorized admin access, or system disruptions, especially within isolated industrial environments.
  3. Cognex advises migrating to newer camera models (In-Sight 2800, 3800, 8900), as the affected products are legacy systems not intended for new installations; however, immediate replacement is often challenging.
  4. Organizations are recommended to mitigate risks by segmenting networks, limiting exposure, using VPNs, and deploying cybersecurity tools, as the vulnerabilities pose significant threats within critical manufacturing infrastructures.

What’s the Problem?

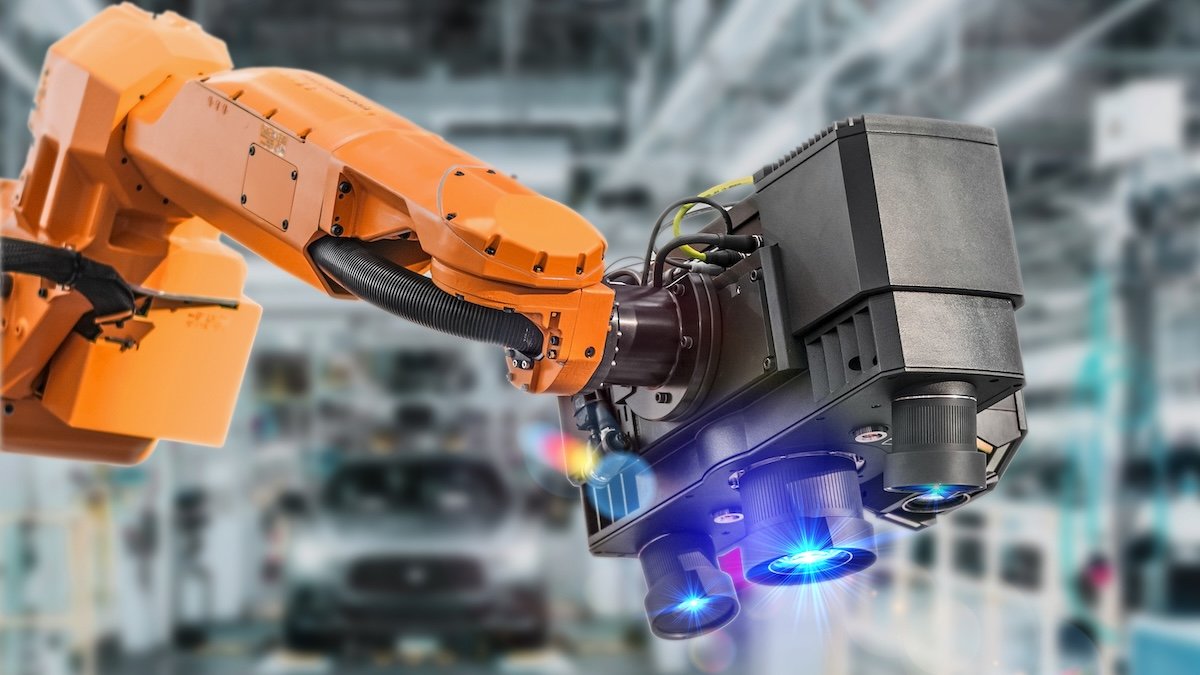
The story concerns serious cybersecurity vulnerabilities found in certain Cognex industrial cameras, which are widely used in manufacturing settings for guiding robots, inspecting products, and tracking items. Discovered by cybersecurity firm Nozomi Networks, nine vulnerabilities—including high-severity issues like hardcoded passwords, unsecured data transmission, and privilege escalation—affect multiple Cognex In-Sight series cameras. While these cameras typically operate within closed, localized networks, the vulnerabilities could be exploited if an attacker gains access to the network, allowing for Man-in-the-Middle attacks, credential theft, or system disruptions. The cybersecurity agency CISA has alerted organizations, but Cognex has refused to release patches, citing that these flaws exist in outdated, legacy products not intended for modern use. Instead, Cognex recommends migrating to newer models, yet many companies still rely on these vulnerable devices; mitigation strategies like network segmentation and VPN use are advised in the meantime to reduce risk. The situation underscores the importance of proactive cybersecurity measures in industrial environments, especially when hardware vulnerabilities remain unpatched and potentially exploitable.

Critical Concerns

Certain Cognex industrial cameras, notably the In-Sight series, are vulnerable to critical security flaws—including hardcoded passwords, insecure data transmission, privilege escalation, and authentication bypass—that, although not directly exploitable via the internet due to their typical closed environments, pose significant risks if attackers gain indoor network access. Since these cameras play vital roles in guiding robots, quality inspection, and tracking within manufacturing, exploitation could lead to severe operational disruptions, unauthorized data access, or system control, especially considering the high-severity nature of most vulnerabilities. The manufacturer has decided against issuing patches, citing legacy product status, prompting reliance on mitigations such as network segmentation, access restrictions, and VPN use to reduce exposure. Given the widespread deployment of these devices in critical sectors, failure to address these vulnerabilities jeopardizes industrial security, potentially leading to compromised production processes, intellectual property theft, or even physical safety hazards, underscoring the urgent need for vigilant cybersecurity practices and strategic upgrades in industrial environments.

Possible Next Steps

Prompt attention to addressing vulnerabilities in Cognex industrial cameras is crucial to prevent potential exploitation, protect sensitive operations, and maintain system integrity.

Mitigation Strategies:

  • Apply Firmware Updates: Regularly install manufacturer-released patches to close security gaps.

  • Disable Unnecessary Features: Turn off unused functionalities that could be exploited.

  • Network Segmentation: Isolate cameras within separate network segments to contain potential breaches.

  • Implement Firewalls: Use firewalls to restrict access to camera systems only to trusted sources.

  • Strong Authentication: Enforce robust password policies and enable multi-factor authentication.

  • Routine Security Audits: Conduct periodic assessments to identify and address emerging vulnerabilities.

  • Vendor Engagement: Collaborate with the manufacturer to obtain timely security advisories and patches.

Explore More Security Insights

Discover cutting-edge developments in Emerging Tech and industry Insights.

Learn more about global cybersecurity standards through the NIST Cybersecurity Framework.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

CISO Update Cognex Cybersecurity ICS MX1 vulnerability
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleLLM-Powered LAMEHUG: Revolutionizing Malware for Recon and Data Theft
Next Article Meet LockBit 5.0: Faster ESXi Encryption & Smarter Evasion
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

WordPress Backdoor Reinstates via Files, Database, Shared Memory

October 1, 2026

Attackers Exploit ScreenConnect for Remote Access Breaching

October 1, 2026

MetaMask breach targets Ethereum validator security vulnerabilities

October 1, 2026

Comments are closed.

Latest Posts

Kimwolf v7 Android Botnet: Cloaking DDoS Traffic as Legitimate Browsing

September 28, 2026

Attackers Exploit SharePoint Authentication Bypass Post-PoC Release

September 25, 2026

Apple Alerts: 110 Countries at Risk of Spyware Attacks

September 22, 2026

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026
Don't Miss

WordPress Backdoor Reinstates via Files, Database, Shared Memory

By Staff WriterOctober 1, 2026

Quick Takeaways A sophisticated WordPress backdoor named "SC" employs multiple persistent, self-healing components across files,…

Attackers Exploit ScreenConnect for Remote Access Breaching

October 1, 2026

MetaMask breach targets Ethereum validator security vulnerabilities

October 1, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • WordPress Backdoor Reinstates via Files, Database, Shared Memory
  • Attackers Exploit ScreenConnect for Remote Access Breaching
  • MetaMask breach targets Ethereum validator security vulnerabilities
  • Clico cyber tool reveals Czech firms’ security weaknesses
  • Why Resilient OT Is Critical for Today’s Boards
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

WordPress Backdoor Reinstates via Files, Database, Shared Memory

October 1, 2026

Attackers Exploit ScreenConnect for Remote Access Breaching

October 1, 2026

MetaMask breach targets Ethereum validator security vulnerabilities

October 1, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026235 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026212 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026210 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.