
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

EU CRA: Report It—Even If You Don’t Have to Fix It

October 29, 2026

Hive and Nefilim Ransomware Affiliate Jailed for 70 Months

October 29, 2026

Anthropic’s IPO Security Risks

October 29, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » GMO Offers $1M Bounty for FX Cloud Hackers
Uncategorized

GMO Offers $1M Bounty for FX Cloud Hackers

Staff WriterBy Staff WriterOctober 28, 2026No Comments3 Mins Read2 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Fast Facts

  1. GMO is offering up to $1 million for credible tips leading to an arrest or international wanted notice after attackers demanded about $50 million.

  2. The Desktop Cloud breach may affect 26,739 servers. Stolen customer data and trading logins have been linked to unauthorized trades; the full impact remains unknown.

  3. GMO shut down the service and is investigating. Attackers threatened further leaks and ransomware, but the breach method and claims about compromised customer PCs remain unconfirmed.

  4. Customers should change passwords, end active sessions, enable two-factor authentication, and check accounts. GMO says it will compensate users and cover verified breach-related trading losses.

Japan’s GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach

A Reward for Actionable Tips

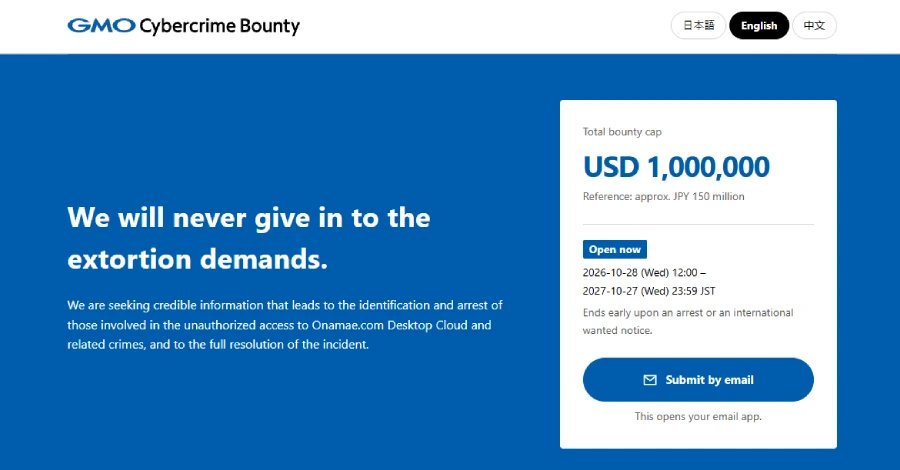
Japan’s GMO Internet Group is offering up to $1 million for information that helps authorities identify and arrest the people behind a breach of its Onamae.com Desktop Cloud service. The program opened on October 28 and runs until an arrest, an international wanted notice, or October 27, 2027.

GMO will pay only for tips that lead to one of those outcomes. It may award the full amount to one person or divide it among several tipsters. The company wants evidence connecting people, online accounts, servers, or cryptocurrency addresses to the attack or its proceeds—not guesses or information already available publicly.

Tipsters can contact GMO anonymously in Japanese, English, or Chinese. However, they must prove their identity to receive payment. GMO also warns people not to hack systems, contact the attackers, or buy leaked information.

The company has not confirmed how the attackers entered the service. GMO’s group head has acknowledged that staff did not respond quickly or thoroughly enough to earlier security warnings. The attackers have made claims about weaknesses in the service, but GMO has not verified them.

Trading Accounts and Customer Risks

GMO says the attackers stole customer information and demanded about $50 million. The service provided Windows desktops that customers used for foreign-exchange trading. GMO identified 26,739 servers as potentially affected, but that figure does not mean attackers broke into every server or stole data from every customer.

Some customers reported trades they did not recognize. Broker OANDA Japan confirmed that someone used login details it believes came from the breached servers to access and trade on some customer accounts. It restricted trading on accounts that might face risk. GMO has not yet confirmed the full scope of the leak or which losses qualify for compensation.

Meanwhile, customers should change trading passwords from a separate device, end active sessions, review account activity, and turn on two-factor authentication where available. These steps can reduce risk, though they cannot undo trades that already occurred. GMO says it will pay current users ¥5,000 and cover verified trading losses and fees caused by unauthorized trades.

Cloud desktops can make trading and other online work more convenient. However, this incident shows why users and service providers must protect stored passwords and respond quickly to security warnings.

Continue Your Tech Journey

Dive deeper into the world of Cryptocurrency and its impact on global finance.

Access comprehensive resources on technology by visiting Wikipedia.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleClickFix Campaign Uses Social Engineering to Deliver Malware
Next Article Cyber Defense Tool Prioritizes Security Risks
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

PeopleSoft Zero-Day: Three Flaws Chained Together

October 29, 2026

Keystone to Destroy 18,835 Wallets After Verification-Key Theft

October 28, 2026

CyberStrikeAI Unleashes 44 AI Agents on Japan Targets

October 27, 2026

Comments are closed.

Latest Posts

Hive and Nefilim Ransomware Affiliate Jailed for 70 Months

October 29, 2026

Anthropic’s IPO Security Risks

October 29, 2026

Exploited Vulnerabilities Are Driving More Breaches

October 29, 2026

Officials Seize Virtualine, Top Bulletproof Host’s Domain

October 29, 2026
Don't Miss

PeopleSoft Zero-Day: Three Flaws Chained Together

By Staff WriterOctober 29, 2026

Top Highlights Critical flaw: CVE-2026-35273 chains three PeopleSoft vulnerabilities, enabling unauthenticated remote code execution (CVSS…

Keystone to Destroy 18,835 Wallets After Verification-Key Theft

October 28, 2026

CyberStrikeAI Unleashes 44 AI Agents on Japan Targets

October 27, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • EU CRA: Report It—Even If You Don’t Have to Fix It

  • Hive and Nefilim Ransomware Affiliate Jailed for 70 Months
  • Anthropic’s IPO Security Risks

  • Exploited Vulnerabilities Are Driving More Breaches

  • AI-Enabled NIK C2 Framework Advances Command-and-Control Capabilities
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

EU CRA: Report It—Even If You Don’t Have to Fix It

October 29, 2026

Hive and Nefilim Ransomware Affiliate Jailed for 70 Months

October 29, 2026

Anthropic’s IPO Security Risks

October 29, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026338 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026220 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026216 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.