

Summary Points
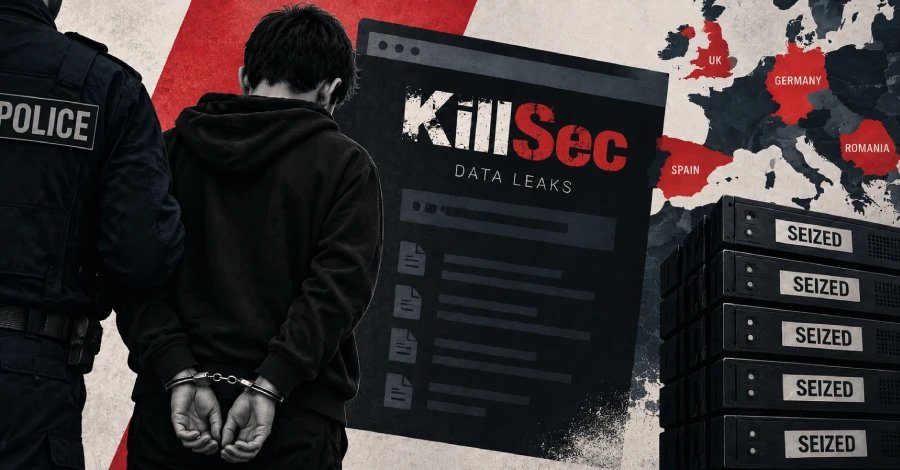
- Spanish police arrested a 16-year-old suspected of running the KillSec ransomware group, which steals and blackmails organizations using data extortion.
- Multiple countries, including the UK and Romania, participated in the takedown, seizing servers, data, and cryptocurrency linked to KillSec.
- The group exploited vulnerabilities, used AI, and bought stolen credentials to target around 1,000 organizations globally, extorting more than 280 victims.
- Authorities continue investigations into remaining members, potential victims, and the group’s financial activities, with efforts to dismantle its infrastructure ongoing.
Police Capture Key Suspect and Seize Ransomware Site
Recently, Spanish police arrested a 16-year-old suspect linked to the notorious KillSec ransomware group. This operation took place on September 30, when authorities also took control of the group’s leak website. Investigators believe the teen served as KillSec’s main operator and administrator. Alongside him, two other men in their 20s, one from the U.K. and the other from Romania, were also detained. The police executed multiple searches, including at a home and hotel in Alicante. They managed to confiscate servers, computers, phones, and cryptocurrency wallets. During the raid, authorities secured more than 110 terabytes of data and shut down several servers used for malicious activities. This coordinated effort involved agencies from Spain, Germany, Romania, and the U.S., illustrating the global scope of fighting cybercrime.
Group’s Methods and Ongoing Investigation
KillSec operated by exploiting vulnerabilities in software and cyber defenses, mainly targeting cloud storage systems. Once inside, members copied sensitive data and posted it on their dark web leak site. They then threatened organizations with public data release unless ransom payments were made. If victims refused to pay, the group often leaked or sold their stolen information. Authorities estimate the group carried out around 1,000 attacks worldwide, with over half believed successful. The group also used artificial intelligence to help identify targets and build their infrastructure, making their attacks more effective. Law enforcement continues examining seized devices and tracking the group’s finances, aiming to uncover additional victims and members. The operation marks a significant step in disrupting a cybercriminal network that caused extensive damage across multiple countries.
Stay Ahead with the Latest Tech Trends
Dive deeper into the world of Cryptocurrency and its impact on global finance.
Discover archived knowledge and digital history on the Internet Archive.
DataProtection-V1
