
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

AI Hacking Agents Exposed Online

November 11, 2026

Fireworks AI Breach Widens to Customer Data, Model Weights and Notion AI Chats

November 11, 2026

Iran Suspected in Cyberattacks on 700 European Supermarkets

November 11, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Attackers Exploit SharePoint Authentication Bypass Post-PoC Release
Cybercrime and Ransomware

Attackers Exploit SharePoint Authentication Bypass Post-PoC Release

Staff WriterBy Staff WriterSeptember 25, 2026No Comments2 Mins Read3 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Top Highlights

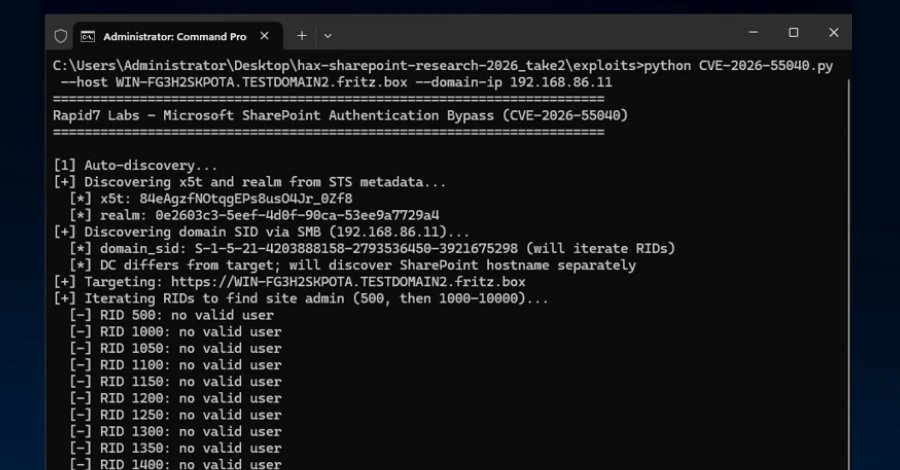
  1. Threat actors are actively exploiting CVE-2026-55040—a critical SharePoint vulnerability—using a newly released proof-of-concept to bypass security and impersonate users.
  2. The flaw stems from weak authentication, allowing attackers to forge JWT tokens by chaining multiple vulnerabilities in token validation.
  3. Successful exploitation enables unauthenticated remote attackers to perform arbitrary actions on SharePoint, potentially exposing and altering sensitive data.
  4. With recent activity spikes from multiple regions, organizations are urged to promptly update SharePoint instances to defend against ongoing exploitation efforts.

Attackers Use Public PoC to Exploit SharePoint Vulnerability

Recently, threat actors have started exploiting a newly discovered flaw in Microsoft SharePoint. This attack follows the public release of a proof-of-concept (PoC) code. The vulnerability, identified as CVE-2026-55040, scores a high 9.1 on the severity scale. It allows hackers to bypass key security checks, especially authentication measures. Microsoft patched this flaw in its July 2026 update, but the risk remains active. As proof, cybercriminals have begun leveraging the PoC to launch attacks. These steps demonstrate how quickly new security flaws can be exploited once publicly known.

What This Means for SharePoint Users and Security

This breach highlights how attackers forge valid tokens to impersonate users. Specifically, they exploit weaknesses in the JWT token validation process. By forging a token with “alg: none,” they bypass the usual signature verification, making impersonation simple. Once inside, hackers can access files, modify data, and perform actions as legitimate users. Over the past month, 12 such attack attempts occurred from various countries. These efforts show how dangerous the flaw is and why it’s essential for users to update their systems immediately. This incident underscores the ongoing challenge of keeping enterprise security tight in a rapidly evolving threat landscape.

Stay Ahead with the Latest Tech Trends

Learn how the Internet of Things (IoT) is transforming everyday life.

Stay inspired by the vast knowledge available on Wikipedia.

CyberAttacks-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleAI Identifies Dark Web Cyber Threats in Text and Images
Next Article Elementor CSRF flaw enables site takeover via crafted links
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

AI Hacking Agents Exposed Online

November 11, 2026

Iran Suspected in Cyberattacks on 700 European Supermarkets

November 11, 2026

GhostFrame Hijacks ESXi VMs, Steals Windows Credentials

November 11, 2026

Comments are closed.

Latest Posts

AI Hacking Agents Exposed Online

November 11, 2026

Iran Suspected in Cyberattacks on 700 European Supermarkets

November 11, 2026

GhostFrame Hijacks ESXi VMs, Steals Windows Credentials

November 11, 2026

N-able N-central Gets Urgent Fix After 33 Exploits Emerge

November 10, 2026
Don't Miss

AI Hacking Agents Exposed Online

By Staff WriterNovember 11, 2026

Quick Takeaways AI-powered hacking frameworks are exposed online: A November 7 Shodan snapshot found 1,428…

Iran Suspected in Cyberattacks on 700 European Supermarkets

November 11, 2026

GhostFrame Hijacks ESXi VMs, Steals Windows Credentials

November 11, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • AI Hacking Agents Exposed Online

  • Fireworks AI Breach Widens to Customer Data, Model Weights and Notion AI Chats
  • Iran Suspected in Cyberattacks on 700 European Supermarkets

  • GhostFrame Hijacks ESXi VMs, Steals Windows Credentials
  • SGLang RCE Exposes 18 Agents, 100 Users

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

AI Hacking Agents Exposed Online

November 11, 2026

Fireworks AI Breach Widens to Customer Data, Model Weights and Notion AI Chats

November 11, 2026

Iran Suspected in Cyberattacks on 700 European Supermarkets

November 11, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026388 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026266 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.