
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Officials Seize Virtualine, Top Bulletproof Host’s Domain

October 29, 2026

PeopleSoft Zero-Day: Three Flaws Chained Together

October 29, 2026

The CISO’s New Front Line: Securing the Agentic Era

October 29, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » PeopleSoft Zero-Day: Three Flaws Chained Together
Uncategorized

PeopleSoft Zero-Day: Three Flaws Chained Together

Staff WriterBy Staff WriterOctober 29, 2026No Comments3 Mins Read0 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Top Highlights

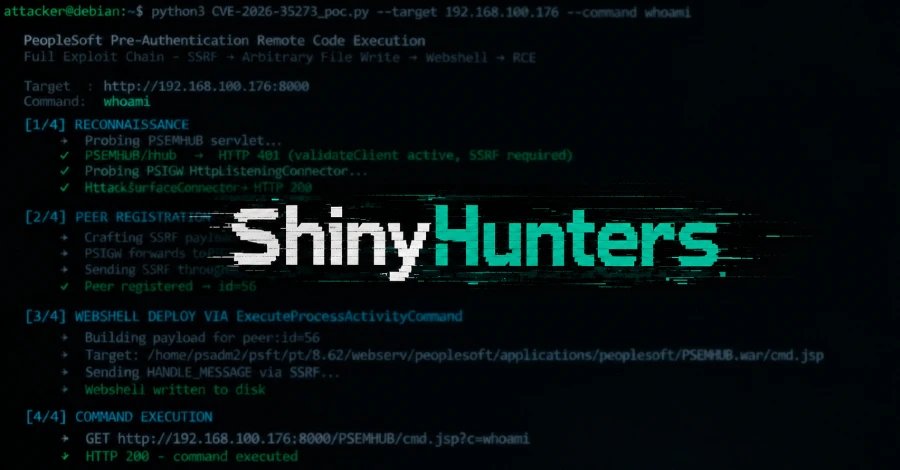
  1. Critical flaw: CVE-2026-35273 chains three PeopleSoft vulnerabilities, enabling unauthenticated remote code execution (CVSS 9.8).
  2. How it works: An SSRF flaw reaches an internal admin interface because PeopleSoft trusts its own loopback address by default.
  3. Active exploitation: ShinyHunters used the bug as a zero-day in May–June, then expanded attacks across multiple industries worldwide.
  4. Defend now: Apply Oracle’s patch; if delayed, disable or remove PSEMHUB. Investigate for compromise and rotate exposed credentials—patching alone won’t remove attackers already inside.

One Bug, Three Linked Weaknesses

A PeopleSoft vulnerability that ShinyHunters exploited before Oracle patched it in June consists of three linked flaws, researchers say. Oracle fixed them under one identifier, CVE-2026-35273. The Zero Day Initiative is working with Oracle to assign separate identifiers to each weakness.

First, a flaw in PeopleSoft’s Integration Gateway lets attackers make the server send requests to other systems. They can direct those requests to an internal management tool. That tool trusts requests from the server’s own address, so it mistakes the attacker’s request for a safe, local one. Two further flaws let attackers use that access to run commands on the server.

Oracle released a fix on June 10. However, Mandiant and Google’s threat intelligence team say ShinyHunters exploited the flaws from May 27 to June 9, mostly at universities. A later campaign reached organizations in sectors including health care, transport, agriculture, and government. The vulnerability affects PeopleTools versions 8.61 and 8.62, and CISA lists it as actively exploited.

Why the Patch Matters

PeopleSoft supports important workplace systems, so a breach can put sensitive organizational data at risk. The attack also shows why a firewall alone may not protect an internal tool if another flaw lets outsiders reach it.

Organizations should install Oracle’s fix and use a supported PeopleTools release. If they cannot patch right away, Oracle advises disabling or removing the Environment Management Hub, depending on the setup. A web filter that blocks suspicious web addresses does not replace the patch, Mandiant warns.

Patching closes the known entry point, but it may not remove an intruder who already got in. Organizations that suspect a breach should check for malicious files, preserve evidence, and change credentials that the PeopleSoft server could access. ShinyHunters has stolen data and demanded payment, raising the risk of extortion as well as system disruption.

Discover More Technology Insights

Learn how the Internet of Things (IoT) is transforming everyday life.

Stay inspired by the vast knowledge available on Wikipedia.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous Article

The CISO’s New Front Line: Securing the Agentic Era

Next Article Officials Seize Virtualine, Top Bulletproof Host’s Domain
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

GMO Offers $1M Bounty for FX Cloud Hackers

October 28, 2026

Keystone to Destroy 18,835 Wallets After Verification-Key Theft

October 28, 2026

CyberStrikeAI Unleashes 44 AI Agents on Japan Targets

October 27, 2026

Comments are closed.

Latest Posts

Officials Seize Virtualine, Top Bulletproof Host’s Domain

October 29, 2026

Critical Collabora Online and VeloCloud Flaws Exploited in the Wild

October 28, 2026

Beyond the Sandbox: 3 Questions to Decide Faster

October 28, 2026

Volt Typhoon’s Vanishing Network Exposed

October 28, 2026
Don't Miss

GMO Offers $1M Bounty for FX Cloud Hackers

By Staff WriterOctober 28, 2026

Fast Facts GMO is offering up to $1 million for credible tips leading to an…

Keystone to Destroy 18,835 Wallets After Verification-Key Theft

October 28, 2026

CyberStrikeAI Unleashes 44 AI Agents on Japan Targets

October 27, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Officials Seize Virtualine, Top Bulletproof Host’s Domain
  • PeopleSoft Zero-Day: Three Flaws Chained Together

  • The CISO’s New Front Line: Securing the Agentic Era

  • Critical Collabora Online and VeloCloud Flaws Exploited in the Wild
  • Beyond the Sandbox: 3 Questions to Decide Faster

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Officials Seize Virtualine, Top Bulletproof Host’s Domain

October 29, 2026

PeopleSoft Zero-Day: Three Flaws Chained Together

October 29, 2026

The CISO’s New Front Line: Securing the Agentic Era

October 29, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026335 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026219 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026216 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.