
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Google Gemini malware exposure from security test domain mix-up

September 19, 2026

Actionable Security Fundamentals to Reduce Risk

September 19, 2026

Zero-Day Alert: API Endpoint Authentication Flaws

September 18, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Unlocking the Future: Inside Pillar’s AI Security Platform
Cybercrime and Ransomware

Unlocking the Future: Inside Pillar’s AI Security Platform

Staff WriterBy Staff WriterJuly 30, 2025No Comments4 Mins Read2 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Quick Takeaways

  1. Holistic AI Security Platform: Pillar Security offers a comprehensive platform that spans the entire software development lifecycle, aiming to provide trust in AI systems through adaptable defenses and real-time threat detection.

  2. Expertise-Driven Foundation: Founded by cybersecurity leaders with both offensive and defensive backgrounds, Pillar combines practical insights to create an effective red team-blue team approach for threat mitigation in AI.

  3. Proactive Threat Modeling: The platform begins with the AI Workbench, allowing teams to simulate attacks and align AI usage with security policies before code is written, cultivating security at the design stage.

  4. Adaptive Guardrails and Sandbox Environments: Pillar enforces adaptive runtime security policies that evolve with emerging threats, while sandboxing techniques isolate AI agents to minimize risks and ensure controlled operation without disruptions.

The Issue

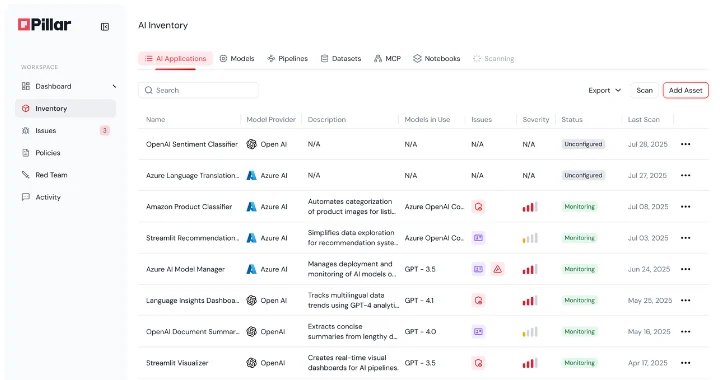
Pillar Security has crafted a comprehensive platform designed to address the myriad challenges of AI security throughout the software development lifecycle. Co-founded by Dor Sarig, with a notable cyber-offensive background, and Ziv Karlinger, a specialist in defensive techniques, the company leverages their combined expertise to create a robust framework for identifying and mitigating security threats. Their platform begins with an innovative AI workbench that facilitates proactive threat modeling even before coding begins, ensuring that AI applications adhere to organizational policies and regulatory standards. By integrating with various development environments and mapping out potential vulnerabilities, Pillar establishes a continuous feedback mechanism that enhances the security posture of applications through adaptive guardrails and real-time monitoring.

This initiative comes at a crucial juncture, as organizations grapple with the complexities of AI, including risks associated with rampant AI utilization—often referred to as AI sprawl. Pillar’s platform sets itself apart with its ability to provide deep visibility into AI assets, conduct real-time telemetry, and execute simulated attacks to preemptively counteract potential threats. Reported by a trusted partner in the technology sector, this account underscores how Pillar Security’s multifaceted, holistic approach not only fortifies AI systems against current threats but also dynamically evolves to anticipate and address future challenges.

Potential Risks

Should a security breach occur within a platform like Pillar Security, the ramifications could reverberate throughout interconnected businesses and users, posing significant risks to operational integrity and user trust. For organizations reliant on AI systems, compromised security can lead to the exposure of sensitive user data, undermining their compliance with regulatory mandates and resulting in financial penalties. Furthermore, the cascading effect could instigate a broader erosion of confidence in AI technologies, thereby stalling innovation and investment across various sectors. Additionally, as third-party applications and integrations come under scrutiny, businesses may face heightened scrutiny and demands for transparency, complicating operational dynamics and potentially destabilizing vendor relationships. Thus, the implications of a single breach extend far beyond immediate financial loss, encapsulating a multifaceted threat landscape that jeopardizes the trust and synergy essential for communal business ecosystems.

Fix & Mitigation

Timely remediation is vital in addressing vulnerabilities to safeguard sensitive data and maintain operational integrity, particularly within platforms like Pillar’s AI Security.

Mitigation Steps

  • Regular Vulnerability Assessments
  • Automated Threat Detection
  • Timely Software Updates
  • User Education Programs
  • Incident Response Planning

NIST CSF Guidance
NIST CSF emphasizes proactive risk management and establishes a framework for identifying, protecting, detecting, responding, and recovering from incidents. For deeper insights, refer to NIST SP 800-53, which outlines specific security and privacy controls for federal information systems.

Advance Your Cyber Knowledge

Stay informed on the latest Threat Intelligence and Cyberattacks.

Explore engineering-led approaches to digital security at IEEE Cybersecurity.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

CISO Update computer security cyber attacks cyber news cyber security news cyber security news today cyber security updates cyber updates Cybersecurity data breach hacker news hacking news how to hack information security MX1 network security ransomware malware software vulnerability the hacker news
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleMinnesota Mobilizes National Guard Amid Cyberattack Crisis
Next Article ShinyHunters: Unmasking the Data Theft Saga of Qantas, Allianz Life, and LVMH
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Google Gemini malware exposure from security test domain mix-up

September 19, 2026

Actionable Security Fundamentals to Reduce Risk

September 19, 2026

Linux Kernel Flaws Enable Local Root Exploits

September 18, 2026

Comments are closed.

Latest Posts

Suspected China-Linked Group Exploits VMware Flaw to Launch Babuk Ransomware

September 16, 2026

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026

TWINLOOT Exploits SharePoint and Teams to Steal Credentials and Lateral Movement

September 10, 2026

Windchill Web Shell Exposes Credentials and Maps Engineering Data

September 7, 2026
Don't Miss

Google Gemini malware exposure from security test domain mix-up

By Staff WriterSeptember 19, 2026

Quick Takeaways Google’s Gemini AI was tested to access protected systems by guessing passwords and…

Actionable Security Fundamentals to Reduce Risk

September 19, 2026

Linux Kernel Flaws Enable Local Root Exploits

September 18, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Google Gemini malware exposure from security test domain mix-up
  • Actionable Security Fundamentals to Reduce Risk
  • Zero-Day Alert: API Endpoint Authentication Flaws
  • Linux Kernel Flaws Enable Local Root Exploits
  • Transparent Tribe Uses Private GitHub for Rust Backdoor Command and Control
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Google Gemini malware exposure from security test domain mix-up

September 19, 2026

Actionable Security Fundamentals to Reduce Risk

September 19, 2026

Zero-Day Alert: API Endpoint Authentication Flaws

September 18, 2026
Most Popular

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026195 Views

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026195 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026193 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.