
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Top Threat Intel Platforms Targeting ransomware and nation-state attacks

September 15, 2026

Nigeria faces 4,906 weekly cyberattacks, surge in threats

September 15, 2026

Guarding Your Organization Against AI-Driven Executive Impersonation and Invoice Fraud

September 15, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Why Real-Time Threat Intelligence Is a Must for Modern SOCs
Cybercrime and Ransomware

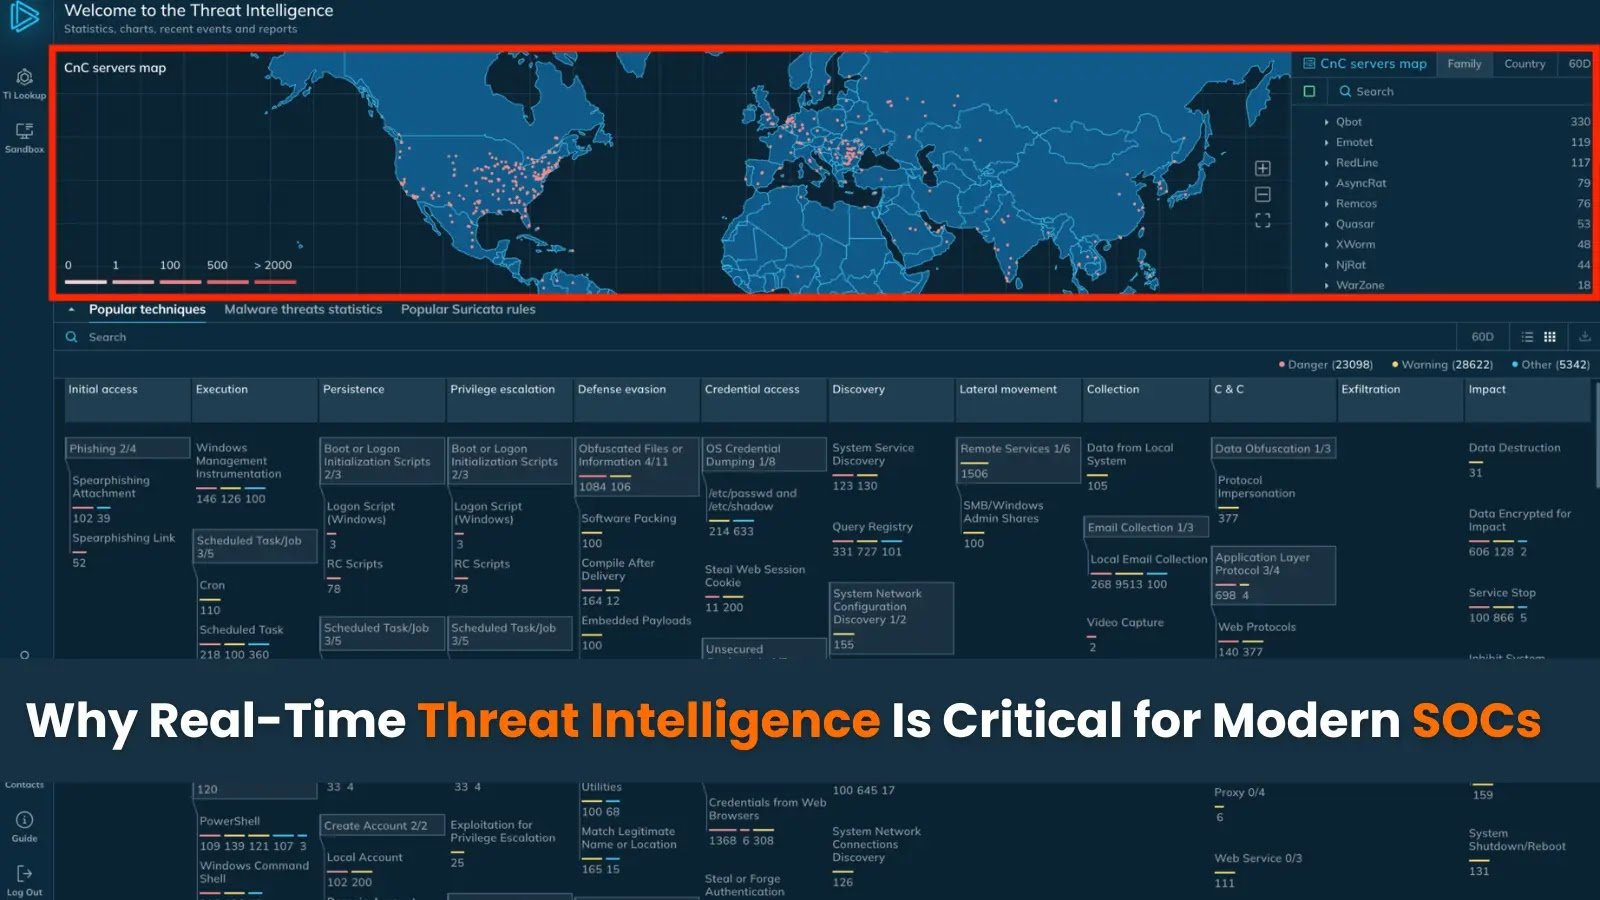
Why Real-Time Threat Intelligence Is a Must for Modern SOCs

Staff WriterBy Staff WriterSeptember 16, 2025No Comments3 Mins Read5 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Top Highlights

  1. SOCs face increasing pressure to detect threats early using real-time threat intelligence (TI) to prevent operational disruptions, financial losses, and reputational damage, as evidenced by recent high-profile cyber incidents.
  2. The integration of automated, actionable threat data—such as IOC patterns—enables immediate response actions like network segmentation and system isolation, significantly reducing downtime and operational impact.
  3. Organizations leveraging real-time TI see tangible benefits: minimized disruptions, faster response times, resource efficiency, and strengthened business resilience amid cyber threats.
  4. Transitioning from reactive to proactive security with live threat intelligence transforms cybersecurity from a cost center into a strategic advantage, safeguarding revenue, customer trust, and competitive edge.

The Issue

Recent high-profile cyberattacks on organizations such as Jaguar Land Rover, Marks & Spencer, and Co-op have demonstrated the devastating consequences of delayed threat detection, including factory shutdowns, massive financial losses, and compromised customer trust. These incidents primarily occurred because security operations centers (SOCs) lacked real-time threat intelligence (TI), which could have facilitated immediate action—such as isolating affected systems or blocking attacker tools—thereby minimizing operational disruption and reputational harm. The report emphasizes that attackers now exploit automation, ransomware, and zero-day vulnerabilities to breach defenses quickly, underscoring the need for SOCs to integrate dynamic, live threat data into automated response workflows.

The report, authored by industry analysts and security providers like ANY.RUN, advocates for advanced TI feeds that deliver real-time, actionable insights—such as IOC patterns of ransomware or phishing activity—enabling organizations to swiftly contain threats and prevent escalation. By transforming SOCs into proactive, automated defense units, businesses can significantly reduce their mean time to respond (MTTR), safeguard revenue, protect their reputation, and ensure continuity in a landscape of increasingly sophisticated cyber adversaries. Ultimately, the message is clear: leveraging live threat intelligence is not just a defensive upgrade but a strategic imperative for resilience and competitive advantage in today’s digital economy.

Potential Risks

Security Operations Centers (SOCs) face mounting pressure to identify and counteract rapidly evolving cyber threats—such as automation exploits, ransomware, and zero-day vulnerabilities—that can cause severe operational disruptions, financial losses reaching hundreds of millions, and reputational damage. Recent incidents, like the shutdowns at Jaguar Land Rover, M&S’s multibillion-dollar losses, Co-op’s customer data breaches, and ransomware attacks on media outlets, underscore the crucial need for real-time threat intelligence to enable proactive responses; early detection of attacker tactics (TTPs) could allow swift containment measures, minimizing downtime and safeguarding supply chains. When integrated into automated workflows, live threat feeds—such as those from ANY.RUN—allow SOCs to dynamically update policies, swiftly quarantine malicious activity, and prioritize alerts, thereby reducing mean response times, operational interruptions, and breach impacts. This proactive approach does not merely enhance security but transforms SOCs into strategic assets—maximizing resource efficiency, reinforcing resilience, and maintaining trust—ultimately turning threat data into a vital weapon that protects revenue, preserves reputation, and sustains competitive advantage amid sophisticated cyber adversaries.

Possible Action Plan

In the fast-changing landscape of cyber threats, addressing security issues promptly is essential for safeguarding assets, maintaining trust, and minimizing damage. When threats evolve rapidly, delays in response can lead to costly breaches and data loss, making timely remediation vital for effective security management.

Mitigation Strategies:

  • Continuous Monitoring
  • Automated Alerts
  • Threat Detection Tools

Remediation Actions:

  • Incident Response Plans
  • Immediate Threat Isolation
  • Patch and Update Protocols

Advance Your Cyber Knowledge

Explore career growth and education via Careers & Learning, or dive into Compliance essentials.

Explore engineering-led approaches to digital security at IEEE Cybersecurity.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

CISO Update Cybersecurity MX1
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleCritical Bugs in Chaos Mesh Enable Cluster Takeover
Next Article Hacking Forum Admin Sentenced to Three Years in Prison
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Top Threat Intel Platforms Targeting ransomware and nation-state attacks

September 15, 2026

Nigeria faces 4,906 weekly cyberattacks, surge in threats

September 15, 2026

Guarding Your Organization Against AI-Driven Executive Impersonation and Invoice Fraud

September 15, 2026

Comments are closed.

Latest Posts

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026

TWINLOOT Exploits SharePoint and Teams to Steal Credentials and Lateral Movement

September 10, 2026

Windchill Web Shell Exposes Credentials and Maps Engineering Data

September 7, 2026

SilkParasite Espionage Campaign Launches Five New RATs Against Central Asian Governments

September 4, 2026
Don't Miss

Top Threat Intel Platforms Targeting ransomware and nation-state attacks

By Staff WriterSeptember 15, 2026

Essential Insights Correlates credential leaks, exposed vulnerabilities, and active exploits to identify plausible initial access…

Nigeria faces 4,906 weekly cyberattacks, surge in threats

September 15, 2026

Guarding Your Organization Against AI-Driven Executive Impersonation and Invoice Fraud

September 15, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Top Threat Intel Platforms Targeting ransomware and nation-state attacks
  • Nigeria faces 4,906 weekly cyberattacks, surge in threats
  • Guarding Your Organization Against AI-Driven Executive Impersonation and Invoice Fraud
  • Critical Security Flaw Threatens Supply Chain Integrity
  • AI-powered cyberattacks target entire kill chain stages
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Top Threat Intel Platforms Targeting ransomware and nation-state attacks

September 15, 2026

Nigeria faces 4,906 weekly cyberattacks, surge in threats

September 15, 2026

Guarding Your Organization Against AI-Driven Executive Impersonation and Invoice Fraud

September 15, 2026
Most Popular

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026182 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026180 Views

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026180 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.