
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension

November 15, 2026

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

November 15, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension
Uncategorized

Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension

Staff WriterBy Staff WriterNovember 15, 2026No Comments3 Mins Read0 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Essential Insights

  1. Fireworks AI breach exposed Cursor data: A stolen vendor key let attackers access coding-session traces and credentials, affecting API credentials for fewer than 0.01% of Cursor customers.
  2. Stolen credentials enabled wider access: Attackers reached select Cursor SaaS tools and accessed limited support, usage, contact, and internal repository data.
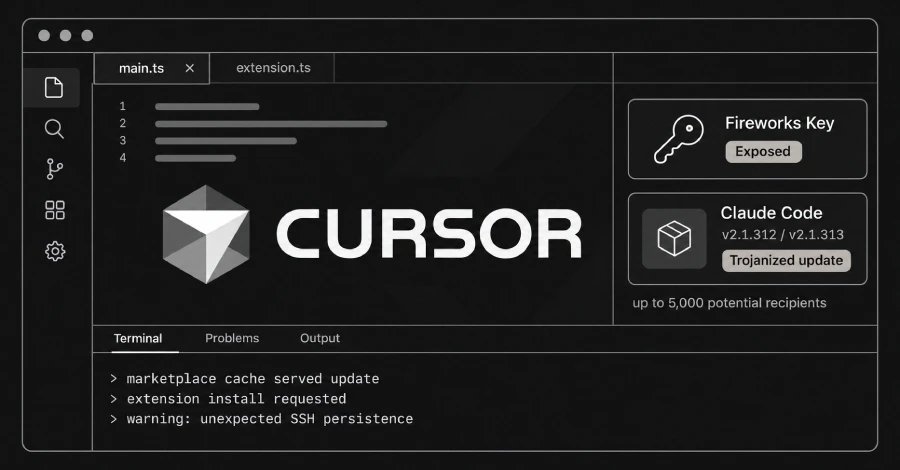
  3. Claude Code extension was trojanized: Up to 5,000 users may have received a malicious version on October 29; it was available for about 11 hours and attempted to install an SSH backdoor.
  4. Cursor says the threat is contained: It revoked credentials and cut ties with Fireworks; no activity has been detected since Nov. 1. Uber and Notion also reported data exposure linked to the provider.

A Stolen Key Opened a Path to the Extension Attack

Cursor says an attacker used an access key exposed during a breach involving Fireworks AI to copy data from a storage bucket. Cursor had shared the bucket with the AI company. The attacker then used credentials found in the copied data to reach some of Cursor’s business tools.

The bucket held limited records from coding-agent sessions that took place mostly in 2025. Cursor says those sessions did not use Privacy Mode and could be used for model training. Some records contained credentials that had not been removed. Fewer than 0.01% of Cursor customers had API credentials exposed, the company said.

On October 29, the attacker used a stolen credential to place altered versions of Anthropic’s Claude Code extension in Cursor’s marketplace cache. The malicious versions could install a persistent backdoor that lets an attacker maintain access to a computer. Up to 5,000 users who requested specific cached versions may have received the files during an 11-hour window. Cursor says it found no evidence of further malicious activity after November 1.

What the Incident Means for AI Coding Tools

Cursor removed the extension, took its marketplace offline, and worked with a cloud provider to shut down the attacker’s server. It also revoked credentials, moved its AI processing away from Fireworks, and contacted users who installed versions 2.1.312 or 2.1.313 during the exposure window.

The company says it found no evidence that Privacy Mode users, customer code repositories, or Cursor’s production systems were affected. Still, the incident shows how a breach at one service provider can reach other companies through shared keys and software channels.

AI coding tools can help people build and review software faster. As more teams adopt them, companies must protect credentials and carefully check the updates they distribute. Those safeguards can help people benefit from AI without losing control of their data or devices.

Expand Your Tech Knowledge

Learn how the Internet of Things (IoT) is transforming everyday life.

Discover archived knowledge and digital history on the Internet Archive.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleUber Confirms Breach: Users’ Personal Data Stolen
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

4,837 Hijacked GitHub Accounts Power CI Secret Stealer Across 1,806+ Repos

November 12, 2026

Stolen AI Keys Rack Up $740K in Unauthorized Charges at Railway

November 12, 2026

Fireworks AI Breach Widens to Customer Data, Model Weights and Notion AI Chats

November 11, 2026

Comments are closed.

Latest Posts

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

November 15, 2026

Maersk Probes Breach After WhiteArmor Claims 100GB Data Theft

November 14, 2026

AI Is Rewriting Cyberattacks

November 14, 2026
Don't Miss

4,837 Hijacked GitHub Accounts Power CI Secret Stealer Across 1,806+ Repos

By Staff WriterNovember 12, 2026

Summary Points GitHub accounts compromised: Stolen credentials from 4,837 accounts were used to test access…

Stolen AI Keys Rack Up $740K in Unauthorized Charges at Railway

November 12, 2026

Fireworks AI Breach Widens to Customer Data, Model Weights and Notion AI Chats

November 11, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension
  • Uber Confirms Breach: Users’ Personal Data Stolen
  • OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

  • Maersk Probes Breach After WhiteArmor Claims 100GB Data Theft

  • AI Is Rewriting Cyberattacks

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension

November 15, 2026

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

November 15, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026403 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026281 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.