
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Storm-0501: Exploiting Entra ID to Exfiltrate & Delete Azure Data in Hybrid Cloud Attacks
Cybercrime and Ransomware

Storm-0501: Exploiting Entra ID to Exfiltrate & Delete Azure Data in Hybrid Cloud Attacks

Staff WriterBy Staff WriterAugust 27, 2025No Comments4 Mins Read5 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Essential Insights

  1. Storm-0501, a hacking group active since 2021, has evolved from on-premises to cloud-based attacks, focusing on data exfiltration, destruction, and extortion in cloud environments using native capabilities instead of traditional malware.
  2. Their tactics include exploiting stolen credentials, privilege escalation, lateral movement, and advanced techniques like DCSync attacks to compromise Active Directory and cloud tenants, often targeting unmanaged devices and security gaps.
  3. The group exfiltrates data, then destroys backups and resources before executing extortion schemes—demanding ransom via platforms like Microsoft Teams—often after resetting admin passwords and creating backdoors.
  4. Microsoft has responded with security updates, including measures to prevent abuse of Directory Synchronization Accounts and support for Modern Authentication, aiming to mitigate Storm-0501’s tactics and safeguard cloud environments.

Problem Explained

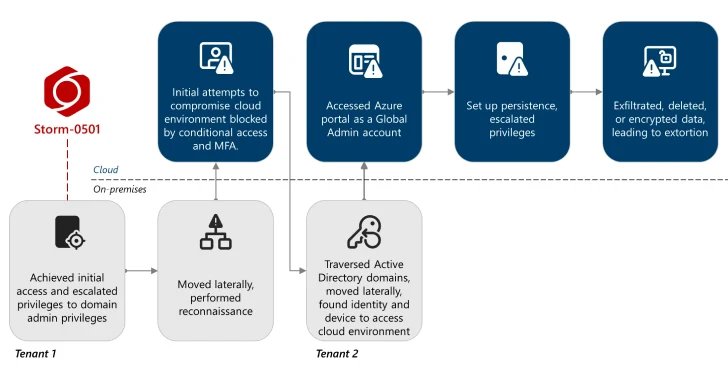
The story details a sophisticated cyberattack carried out by the threat actor known as Storm-0501, which has shifted its tactics from traditional ransomware to targeting cloud environments using advanced exfiltration and extortion methods. Since 2021, this group has evolved into a ransomware-as-a-service operation, leveraging cloud-native tools to quickly steal significant amounts of data, destroy backups and security controls, and demand ransoms—all without deploying conventional malware. In a recent attack on a large multinational enterprise, Storm-0501 exploited vulnerabilities within the organization’s hybrid cloud infrastructure by gaining initial access via stolen credentials, escalating privileges through Active Directory manipulation, and moving laterally across the network using specialized tools like Evil-WinRM and DCSync attacks. They compromised a high-level admin account with no multi-factor authentication, used it to create backdoors, and ultimately exfiltrated sensitive data before deleting it to hinder recovery efforts. Following this, they demanded ransom payments via Microsoft Teams. Microsoft has responded by updating security measures, including safeguards in Microsoft Entra ID and Entra Connect, to prevent similar breaches in the future, emphasizing how adaptable and persistent these threat actors have become in exploiting cloud environments.

Risks Involved

Cyber risks posed by threat groups like Storm-0501 highlight a disturbing evolution in cyberattacks, where malicious actors leverage cloud-native capabilities to conduct sophisticated, multi-stage operations including data exfiltration, destruction, and extortion without relying solely on traditional malware. By exploiting vulnerabilities in hybrid cloud environments, manipulating unmanaged devices, and abusing privileged accounts—such as compromising Global Admin identities through techniques like DCSync—attackers can traverse interconnected systems, escalate privileges, and gain persistent access across on-premises and cloud segments. Their tactics often involve stealthy reconnaissance, lateral movement, deactivation of backups, and resource deletion to impede recovery efforts, ultimately enabling large-scale data breaches and extortion campaigns. This evolving threat landscape underscores the critical need for enhanced security protocols, rigorous credential management, multi-factor authentication, and proactive monitoring to mitigate the profound impacts of such cyber risks on organizational integrity, operational continuity, and data privacy.

Fix & Mitigation

Rapid response is critical when facing threats like Storm-0501 exploits because swift action can prevent extensive data loss and mitigate the potential damage from hybrid cloud attacks. The speed of remediation can mean the difference between containment and widespread compromise.

Mitigation Steps

  • Immediate Isolation: Disconnect affected systems from the network to prevent further exploitation.
  • Access Revocation: Reset compromised credentials and revoke any suspicious permissions.
  • Patch Deployment: Apply the latest security updates and patches to vulnerable Entra ID components.
  • Monitoring & Detection: Increase monitoring for unusual activities and implement intrusion detection systems.
  • Incident Analysis: Conduct a thorough investigation to understand the attack vector and scope.
  • Backup Restoration: Restore data from secure backups if data exfiltration or deletion has occurred.
  • User Training: Educate users on security best practices and phishing awareness to prevent credential compromise.
  • Enhanced Security Controls: Implement multi-factor authentication, conditional access policies, and least privilege principles.
  • Collaborate & Report: Engage with security vendors and report the incident to relevant authorities for coordinated response.

Continue Your Cyber Journey

Stay informed on the latest Threat Intelligence and Cyberattacks.

Access world-class cyber research and guidance from IEEE.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

CISO Update computer security cyber attacks cyber news cyber security news cyber security news today cyber security updates cyber updates Cybersecurity data breach hacker news hacking news how to hack information security MX1 network security ransomware malware software vulnerability the hacker news
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleUnlocking Security: Mimic Achieves FedRAMP Ready Status for Real-Time Ransomware Defense
Next Article Enhancing Workforce Security: CyberArk and Optiv Unite on Privileg
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026

Comments are closed.

Latest Posts

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Suspected China-Linked Group Exploits VMware Flaw to Launch Babuk Ransomware

September 16, 2026

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026

TWINLOOT Exploits SharePoint and Teams to Steal Credentials and Lateral Movement

September 10, 2026
Don't Miss

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

By Staff WriterSeptember 19, 2026

Quick Takeaways A critical SAP Commerce Cloud vulnerability (CVE-2026-58231) with a CVSS score of 10.0…

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat
  • Mastering Security: The One-Incident Test for Unified Platform Evaluation
  • GISEC 2026: Quantum, AI escalate cyberattack sophistication
  • CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies
  • SolarWinds ARM Hard-Coded Key Enables RCE Exploitation
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026200 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026199 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026197 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.