
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » NightEagle APT Exploits Microsoft Exchange to Target China’s Military and Tech
Cybercrime and Ransomware

NightEagle APT Exploits Microsoft Exchange to Target China’s Military and Tech

Staff WriterBy Staff WriterJuly 4, 2025No Comments4 Mins Read28 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Essential Insights

  1. Introduction of NightEagle: A new threat actor, NightEagle (APT-Q-95), targeting Microsoft Exchange servers through a zero-day exploit chain is focused on sectors in China such as government, defense, and technology since 2023.

  2. Attack Details: NightEagle has rapidly changed its network infrastructure and utilizes a modified version of the Go-based Chisel utility for advanced intranet penetration, enabling intelligence gathering from high-tech and military entities.

  3. Trojan Delivery Mechanism: The trojan is delivered via a .NET loader implanted into the Internet Information Server (IIS) of Microsoft Exchange, exploiting a zero-day vulnerability to obtain unauthorized access and read mailbox data.

  4. Timing and Attribution: The attacks predominantly occur between 9 p.m. and 6 a.m. Beijing time, suggesting a possible North American origin for the threat actor, according to QiAnXin’s findings presented at CYDES 2025.

What’s the Problem?

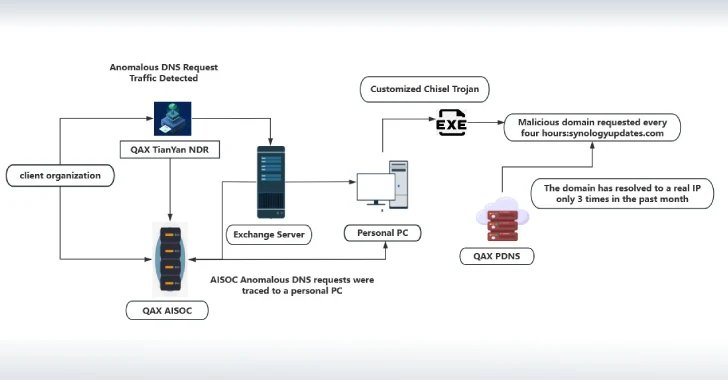
On July 4, 2025, cybersecurity experts unveiled the activities of an enigmatic threat actor dubbed NightEagle (also known as APT-Q-95), which has been targeting Microsoft Exchange servers through a sophisticated zero-day exploit. This shadowy group, active since 2023, has primarily focused on government, defense, and technology sectors within China, conducting cyber espionage to gather sensitive intelligence. The analysis by QiAnXin’s RedDrip Team, presented at the CYDES 2025 conference, revealed that NightEagle operates with remarkable agility, rapidly shifting its network infrastructure to evade detection while executing attacks predominantly during nocturnal hours.

The investigation was prompted by the discovery of a tailored version of the Go-based Chisel tool on a client’s endpoint, indicative of an advanced infiltration strategy. By exploiting a zero-day vulnerability, the attackers compromised the Microsoft Exchange Server’s machineKey, enabling the deployment of a Trojan and unauthorized access to mailbox data. Notably, QiAnXin suggested the perpetrator may be from North America, as attack patterns correlated with nighttime activity in Beijing. As the story unfolds, The Hacker News has reached out to Microsoft for additional insights, indicating an ongoing effort to address this significant cybersecurity threat.

Risks Involved

The emergence of the NightEagle threat actor poses significant risks not only to targeted entities but also to a broader ecosystem of businesses, users, and organizations. Should these attacks proliferate, they could catalyze a chain reaction of cybersecurity breaches, undermining trust in digital infrastructure across sectors reliant on Microsoft Exchange servers. Organizations involved in critical innovation—such as semiconductor manufacturing and AI development—might find sensitive data compromised, leading to intellectual property theft and financial instability. Moreover, the cascading effect of a compromised reputation could deter clients from engaging with firms perceived as vulnerable, exacerbating economic ramifications and potentially resulting in regulatory scrutiny. In essence, the repercussions of such attacks extend far beyond immediate victims, threatening the integrity of entire industries and the confidence of users in digital transactions.

Possible Remediation Steps

In an era where cyber threats evolve incessantly, the expedient addressal of vulnerabilities is paramount, particularly when state-sponsored actors exploit them to target sensitive sectors.

Mitigation Steps

  1. Patch Deployment: Apply the latest security updates from Microsoft immediately.
  2. Access Control: Limit access to critical systems based on the principle of least privilege.
  3. Network Segmentation: Isolate vulnerable systems from the main network to minimize exposure.
  4. Monitoring and Detection: Implement robust monitoring tools to identify unusual activities indicative of exploitation.
  5. Incident Response Plan: Develop and rehearse an incident response strategy to efficiently react to breaches.
  6. User Training: Enhance awareness among personnel regarding phishing and other social engineering tactics.
  7. Backup Systems: Ensure regular backups of data and systems to facilitate recovery following an incident.

NIST CSF Guidance
The NIST Cybersecurity Framework (CSF) emphasizes continuous risk assessment and swift remediation of vulnerabilities. Specifically, Subcategory PR.IP-3 under the Protection function pertains to the timely application of security patches. For more in-depth guidance, refer to NIST Special Publication 800-53, which outlines security and privacy controls necessary for federal information systems.

Continue Your Cyber Journey

Stay informed on the latest Threat Intelligence and Cyberattacks.

Explore engineering-led approaches to digital security at IEEE Cybersecurity.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

CISO Update computer security cyber attacks cyber news cyber security news cyber security news today cyber security updates cyber updates Cybersecurity data breach hacker news hacking news how to hack information security MX1 network security ransomware malware software vulnerability the hacker news
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleDaily CyberTech Highlights: Essential News and Analysis
Next Article Ingram Micro Faces Global Outage: Internal Systems Down
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026

Comments are closed.

Latest Posts

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Suspected China-Linked Group Exploits VMware Flaw to Launch Babuk Ransomware

September 16, 2026

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026

TWINLOOT Exploits SharePoint and Teams to Steal Credentials and Lateral Movement

September 10, 2026
Don't Miss

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

By Staff WriterSeptember 19, 2026

Quick Takeaways A critical SAP Commerce Cloud vulnerability (CVE-2026-58231) with a CVSS score of 10.0…

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat
  • Mastering Security: The One-Incident Test for Unified Platform Evaluation
  • GISEC 2026: Quantum, AI escalate cyberattack sophistication
  • CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies
  • SolarWinds ARM Hard-Coded Key Enables RCE Exploitation
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026200 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026199 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026197 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.