
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » US Expands Sanctions on Russian Crypto Firm Garantex and Affiliates
Cybercrime and Ransomware

US Expands Sanctions on Russian Crypto Firm Garantex and Affiliates

Staff WriterBy Staff WriterAugust 16, 2025Updated:August 17, 2025No Comments3 Mins Read10 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Essential Insights

  1. U.S. sanctions targeted Russian cryptocurrency platforms Garantex and Grinex, accusing them of processing over $96 billion in illicit transactions linked to crimes like ransomware, hacking, and drug trafficking.

  2. Authorities seized domains, servers, and froze more than $26 million in cryptocurrency after a law enforcement operation, leading to arrests including Garantex co-founder Aleksej Besciokov.

  3. The U.S. offers up to $6 million in rewards for information on the leaders of Garantex, notably including $5 million for co-founder Aleksandr Mira Serda.

  4. Additional sanctions were imposed on six entities supporting Garantex and Grinex, highlighting efforts to disrupt the facilitation of ransomware proceeds and cybercrime through these exchanges.

Key Challenge

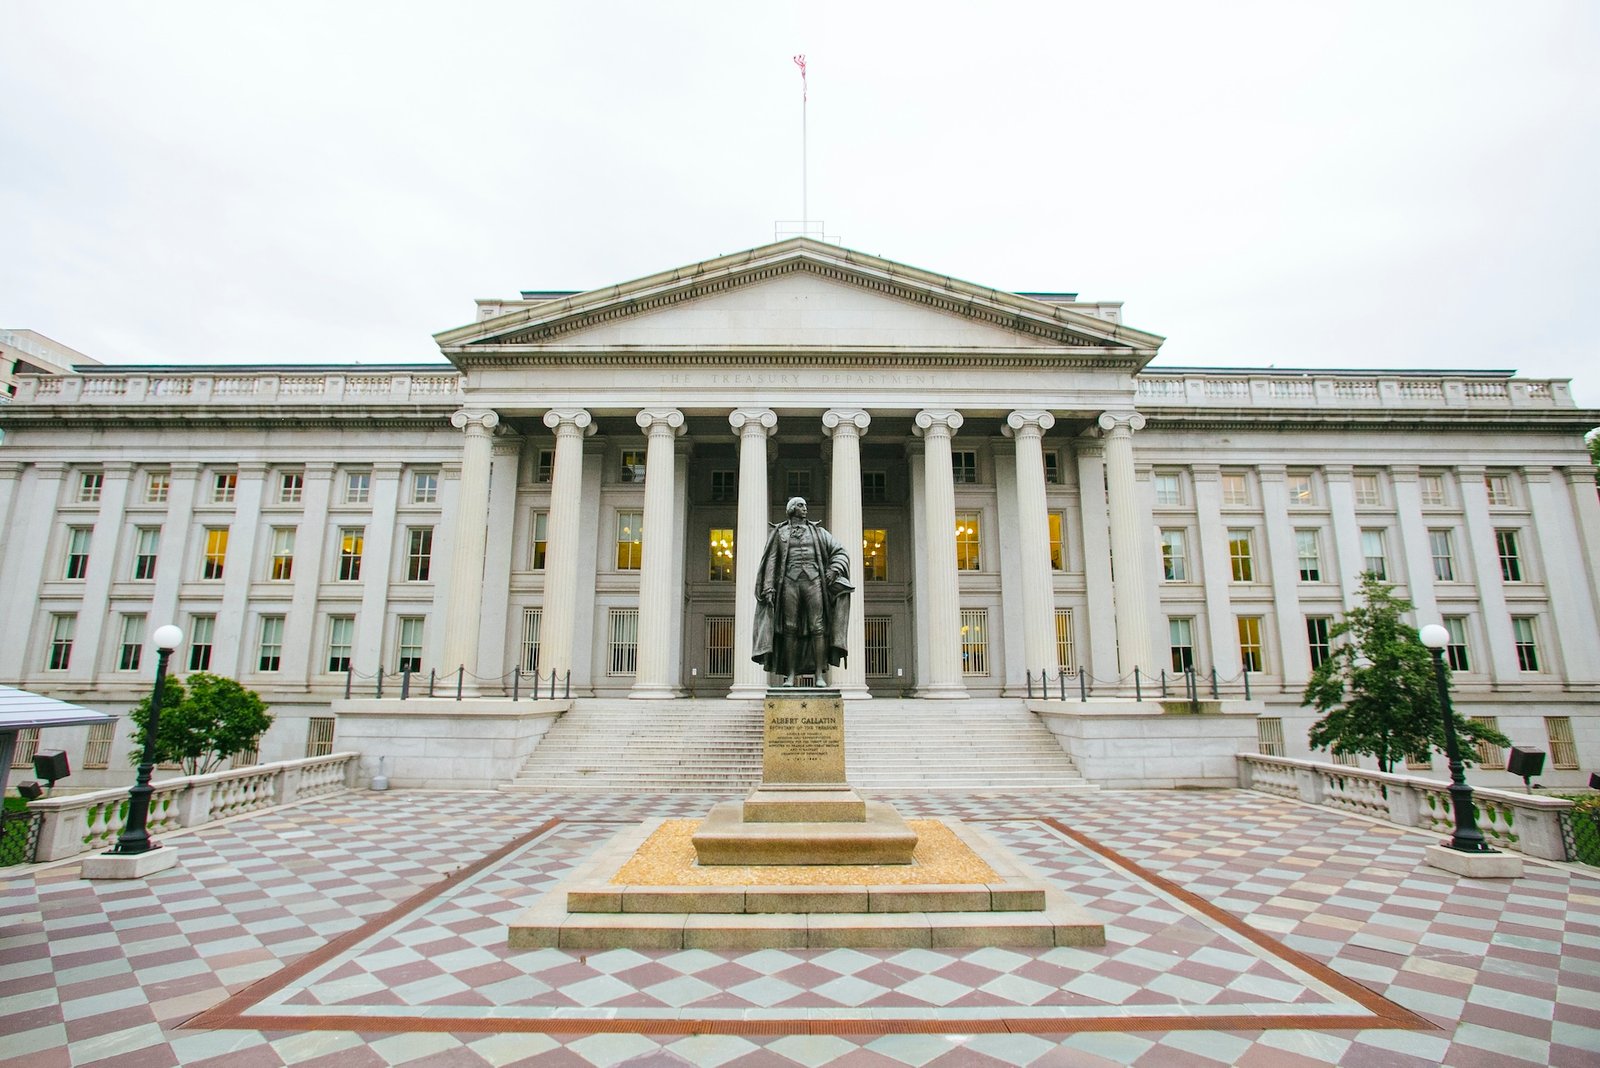
U.S. officials have taken aggressive actions against the Russian cryptocurrency exchange Garantex and its successor Grinex, aiming to disrupt their role in facilitating criminal activities like ransomware payments, hacking, terrorism, and drug trafficking. Garantex, which processed over $96 billion in transactions from 2019 to 2025 and received hundreds of millions of dollars from ransomware affiliates linked to Russian groups such as Conti, Black Basta, and LockBit, was designated for sanctions by the Treasury Department’s Office of Foreign Assets Control (OFAC). This followed a major law enforcement operation in March where authorities seized servers, froze assets, and arrested key figures—including Aleksej Besciokov—who were indicted for their leadership roles. To bolster these efforts, the State Department announced rewards up to $6 million for information leading to the arrest or conviction of Garantex’s leaders, including Aleksandr Mira Serda. The continued sanctions against Garantex, its executives, and related entities reflect the U.S. government’s commitment to targeting the infrastructure used by cybercriminals, highlighting the broader fight against the misuse of digital currencies—especially when it erodes security and causes harm to American victims.

Potential Risks

U.S. authorities have imposed sanctions on Russian cryptocurrency exchanges Garantex and Grinex, alongside their key figures, after uncovering billions in illicit transactions tied to ransomware, hacking, terrorism, and drug trafficking, primarily originating from Russia-linked criminal groups such as Conti, Black Basta, and LockBit. Garantex processed approximately $96 billion from 2019 to 2025, serving as a conduit for laundering criminal proceeds and enabling cybercriminal operations that cause significant harm to U.S. victims. The crackdown, involving domain seizures, server confiscations, and targeted rewards of up to $6 million, underscores the profound cyber risks associated with unregulated digital asset platforms, highlighting their role in facilitating ransomware payments and money laundering. These activities threaten national security, undermine the reputation of legitimate virtual asset providers, and demonstrate the ongoing challenge of securing the cryptocurrency ecosystem against malicious actors intent on exploiting the anonymity and cross-border nature of digital currencies.

Fix & Mitigation

Promptly addressing the expansion of sanctions on Russian crypto exchanges like Garantex and its affiliates is vital to ensure compliance, mitigate legal risks, and maintain financial stability. Swift remediation can also preserve reputation and prevent operational disruptions in an increasingly scrutinized regulatory environment.

Mitigation Strategies:

  • Conduct Immediate Compliance Audits
  • Enhance Due Diligence Procedures
  • Update Internal Policies
  • Engage Legal Advisors
  • Train Staff on New Regulations
  • Implement Continuous Monitoring

Stay Ahead in Cybersecurity

Explore career growth and education via Careers & Learning, or dive into Compliance essentials.

Access world-class cyber research and guidance from IEEE.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

CISO Update crypto cryptocurrency Cybersecurity garantex grinex MX1 office of foreign assets control (ofac) Ransomware Russia sanctions state department treasury department
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleAccenture to Acquire CyberCX, Boosting APAC Cybersecurity Leadership
Next Article Cyberscope Files U.S. Patent for AI Blockchain Trust Scorin
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026

Comments are closed.

Latest Posts

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

Secure Remote Service. Standardize Access. Strengthen Compliance.

October 19, 2026

AI Threats Are Rising: Enforce Accountability. Trust Nothing.

October 19, 2026
Don't Miss

Three Critical NGINX Flaws Get Emergency Fixes

By Staff WriterOctober 20, 2026

Top Highlights F5 issued emergency patches for three NGINX flaws—CVE-2026-15176, CVE-2026-97205, and CVE-2026-93479—each rated critical…

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Three Critical NGINX Flaws Get Emergency Fixes
  • Known Cosmos EVM Flaw Exploited Across Blockchains

  • The Context Layer Enterprise AI Agents Need

  • Secure Remote Service. Standardize Access. Strengthen Compliance.

  • Rank Math PRO Hijacked to Deliver Self-Restoring WordPress Backdoor
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026298 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026214 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026210 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.