
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

ConnectWise Resets Credentials After Incident; Cloud Backup Remains Offline

October 20, 2026

9 Malware Trends Security Pros Can’t Ignore

October 20, 2026

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Windows Device ID Unveiled: Key to FBI’s Capture of Alleged Scattered Spider Hacker
Uncategorized

Windows Device ID Unveiled: Key to FBI’s Capture of Alleged Scattered Spider Hacker

Staff WriterBy Staff WriterJuly 7, 2026No Comments2 Mins Read3 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Fast Facts

  1. U.S. prosecutors linked hacker Peter Stokes to a 2025 retail break-in using a persistent Windows device ID tied to his online activity and locations.
  2. The attack involved manipulating help desk staff via phone, gaining control of admin accounts, and exfiltrating 77 GB of data, despite antivirus efforts.
  3. The case highlights how sophisticated identity verification is crucial, as attackers often hide behind VPNs and aliases, exploiting weak help desk protocols.
  4. Experts stress that arresting individual members like Stokes doesn’t significantly diminish the threat, which is driven by a loose collection of hacking groups operating globally.

Technology’s Role in Tracking Cybercriminals

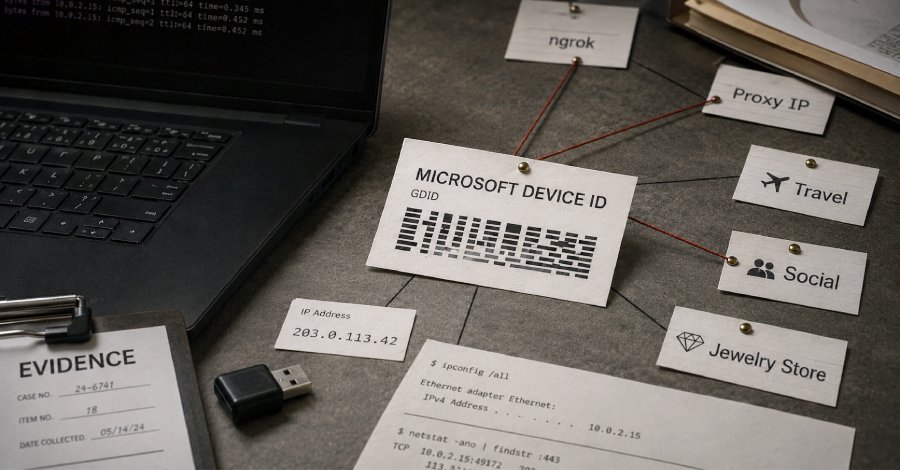
Recently, a federal complaint revealed that the FBI used a unique Windows Device ID to connect a suspect to a major cyberattack. This ID is a persistent marker linked to a single Windows installation, and it can be crucial for investigations. Microsoft provided this ID after analyzing the device involved in the attack. The ID first appeared when the hacker created a tunneling account and later connected to the retailer’s website through the same proxy, making it a key piece of evidence. This shows how digital identifiers can help law enforcement trace cybercriminals, even when they try to hide their tracks. Such technology makes it easier to pinpoint suspects in a complex online environment, which is essential as cyber threats grow more sophisticated.

Implications for Cybersecurity and Law Enforcement

The investigation demonstrated that capturing one operator might not stop the larger threat. Experts argue that groups like Scattered Spider operate as loose collectives, with small cells working independently but sharing tools and techniques. Arrests may temporarily disrupt their activities, but the overall threat remains active. This case also highlights the importance of good security practices. The breach exploited a help desk process, where attackers called pretending to be authorized employees. Preventive steps, such as verifying identities before resetting accounts, can reduce risks. On a broader scale, technology like persistent device IDs is a valuable tool for investigations, but it is just one part of a larger puzzle to combat cybercrime effectively.

Stay Ahead with the Latest Tech Trends

Explore the future of technology with our detailed insights on Artificial Intelligence.

Stay inspired by the vast knowledge available on Wikipedia.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleSuspicious Kakao transfer emails pose account hijacking risk
Next Article Bridging the $50K to $5M Gap: Modernizing Your SOC SLA for 2026 with AI Innovation
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

OpenCode Breach May Expose OpenAI, Anthropic & Google API Keys

October 19, 2026

PEERSTITCH Malware Bypasses VPN Checks via FortiOS Flaw

October 16, 2026

Urgent: Ivanti Connect Secure Flaws Trigger 105 Exploit Attempts

October 14, 2026

Comments are closed.

Latest Posts

9 Malware Trends Security Pros Can’t Ignore

October 20, 2026

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

Secure Remote Service. Standardize Access. Strengthen Compliance.

October 19, 2026
Don't Miss

OpenCode Breach May Expose OpenAI, Anthropic & Google API Keys

By Staff WriterOctober 19, 2026

Quick Takeaways Potential key exposure: An intruder accessed a legacy OpenCode system on October 16;…

PEERSTITCH Malware Bypasses VPN Checks via FortiOS Flaw

October 16, 2026

Urgent: Ivanti Connect Secure Flaws Trigger 105 Exploit Attempts

October 14, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • ConnectWise Resets Credentials After Incident; Cloud Backup Remains Offline
  • 9 Malware Trends Security Pros Can’t Ignore

  • Three Critical NGINX Flaws Get Emergency Fixes
  • Known Cosmos EVM Flaw Exploited Across Blockchains

  • The Context Layer Enterprise AI Agents Need

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

ConnectWise Resets Credentials After Incident; Cloud Backup Remains Offline

October 20, 2026

9 Malware Trends Security Pros Can’t Ignore

October 20, 2026

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026301 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026214 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026210 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.