
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

One compromised laptop. A $6.3B Binance breach.

November 2, 2026

XCPE Botnet Disruption Targets Its Command Infrastructure

November 2, 2026

Fake Teams Support, Stolen Company Data

November 2, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Password Managers at Risk: Clickjacking Vulnerability Exposed
Uncategorized

Password Managers at Risk: Clickjacking Vulnerability Exposed

Staff WriterBy Staff WriterAugust 20, 2025No Comments2 Mins Read11 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Summary Points

  1. Vulnerability Disclosure: Popular password manager browser plugins, including 1Password and Bitwarden, have been found vulnerable to a new clickjacking attack that could lead to credential theft, 2FA code capture, and credit card information leakage.

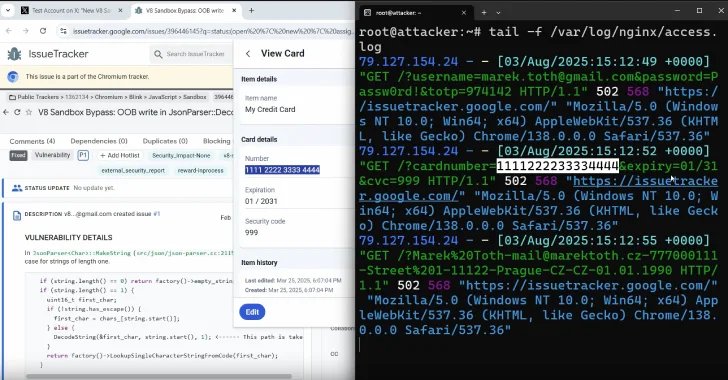
  2. DOM Manipulation Technique: The attack, presented by Marek Tóth at DEF CON 33, exploits browser extensions by manipulating UI elements in the DOM, allowing an invisible pop-up to capture user inputs without their knowledge.

  3. Widespread Impact: Eleven widely-used password managers were tested, with most being susceptible to this attack, revealing a significant risk for millions of users due to auto-fill features functioning on any domain and subdomain.

  4. Precautionary Measures: Until fixes are released by vendors, users are advised to disable auto-fill in their password managers and utilize manual copy/paste methods for sensitive data to mitigate the risk of exploitation.

Widespread Vulnerability in Password Managers

Recent reports reveal that popular password manager browser extensions are vulnerable to a security exploit known as DOM-based extension clickjacking. This flaw allows cybercriminals to potentially steal sensitive user information, including login credentials and credit card details, through manipulated web interfaces.

Researchers unveiled this issue at the DEF CON 33 security conference, highlighting that a simple click on a compromised website could lead to significant data breaches. The technique, developed by Marek Tóth, leverages malicious scripts to manipulate user interface elements such as auto-fill prompts. Consequently, users may unintentionally share their credentials when trying to dismiss harmful pop-ups.

Steps Toward Protection and Remediation

Among the password managers affected are well-known options like 1Password, Bitwarden, and iCloud Passwords, which serve millions of users. In light of this discovery, vendors have begun working on patches, though some have yet to address the vulnerability. Users should disable the auto-fill feature in their password managers and resort to copy-and-paste methods until fixes are available.

For optimal safety, experts recommend configuring auto-fill settings for Chromium-based browsers to require manual activation. By taking these precautions, users can better protect their sensitive information while waiting for official updates from software providers.

Stay Ahead with the Latest Tech Trends

Dive deeper into the world of Cryptocurrency and its impact on global finance.

Explore past and present digital transformations on the Internet Archive.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleUnlocking Security: Keeper Launches Biometric Passkey Login
Next Article Shadow Games: DPRK and China Linked to South Korean Embassy Attacks
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Fake Teams Support, Stolen Company Data

November 2, 2026

Hackers Steal $2.7M from Polymarket Traders via Hijacked Script

November 1, 2026

Chainalysis Breach Exposes Customer Identity Data

October 31, 2026

Comments are closed.

Latest Posts

One compromised laptop. A $6.3B Binance breach.

November 2, 2026

Security That Survives 2027
Build for what’s next.

November 2, 2026

Volt Typhoon May Be Preparing to Strike Critical Infrastructure

November 2, 2026

Hacktober: Cyberattacks Strike PHP, Binance, the Pentagon & More

November 1, 2026
Don't Miss

Fake Teams Support, Stolen Company Data

By Staff WriterNovember 2, 2026

Fast Facts Fake IT support opened the door: Attackers used Microsoft Teams and Quick Assist…

Hackers Steal $2.7M from Polymarket Traders via Hijacked Script

November 1, 2026

Chainalysis Breach Exposes Customer Identity Data

October 31, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • One compromised laptop. A $6.3B Binance breach.
  • XCPE Botnet Disruption Targets Its Command Infrastructure
  • Fake Teams Support, Stolen Company Data

  • Security That Survives 2027
    Build for what’s next.

  • Volt Typhoon May Be Preparing to Strike Critical Infrastructure

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

One compromised laptop. A $6.3B Binance breach.

November 2, 2026

XCPE Botnet Disruption Targets Its Command Infrastructure

November 2, 2026

Fake Teams Support, Stolen Company Data

November 2, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026353 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026231 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026217 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.