

Fast Facts
- The U.S. government’s acting CIO prioritizes enterprise cyber defense, operational resilience, and securing a modern government, emphasizing a whole-of-government approach.
- An upcoming tabletop exercise will focus on assessing agencies’ readiness for cyber incidents, including interagency collaboration and process improvements.
- Agencies are urged to act proactively on resilience and share best practices across government, as adversaries exploit gaps between agencies.
- Securing a modern government involves managing data and emerging technologies like AI and post-quantum cryptography, building on existing federal security frameworks.
The Issue
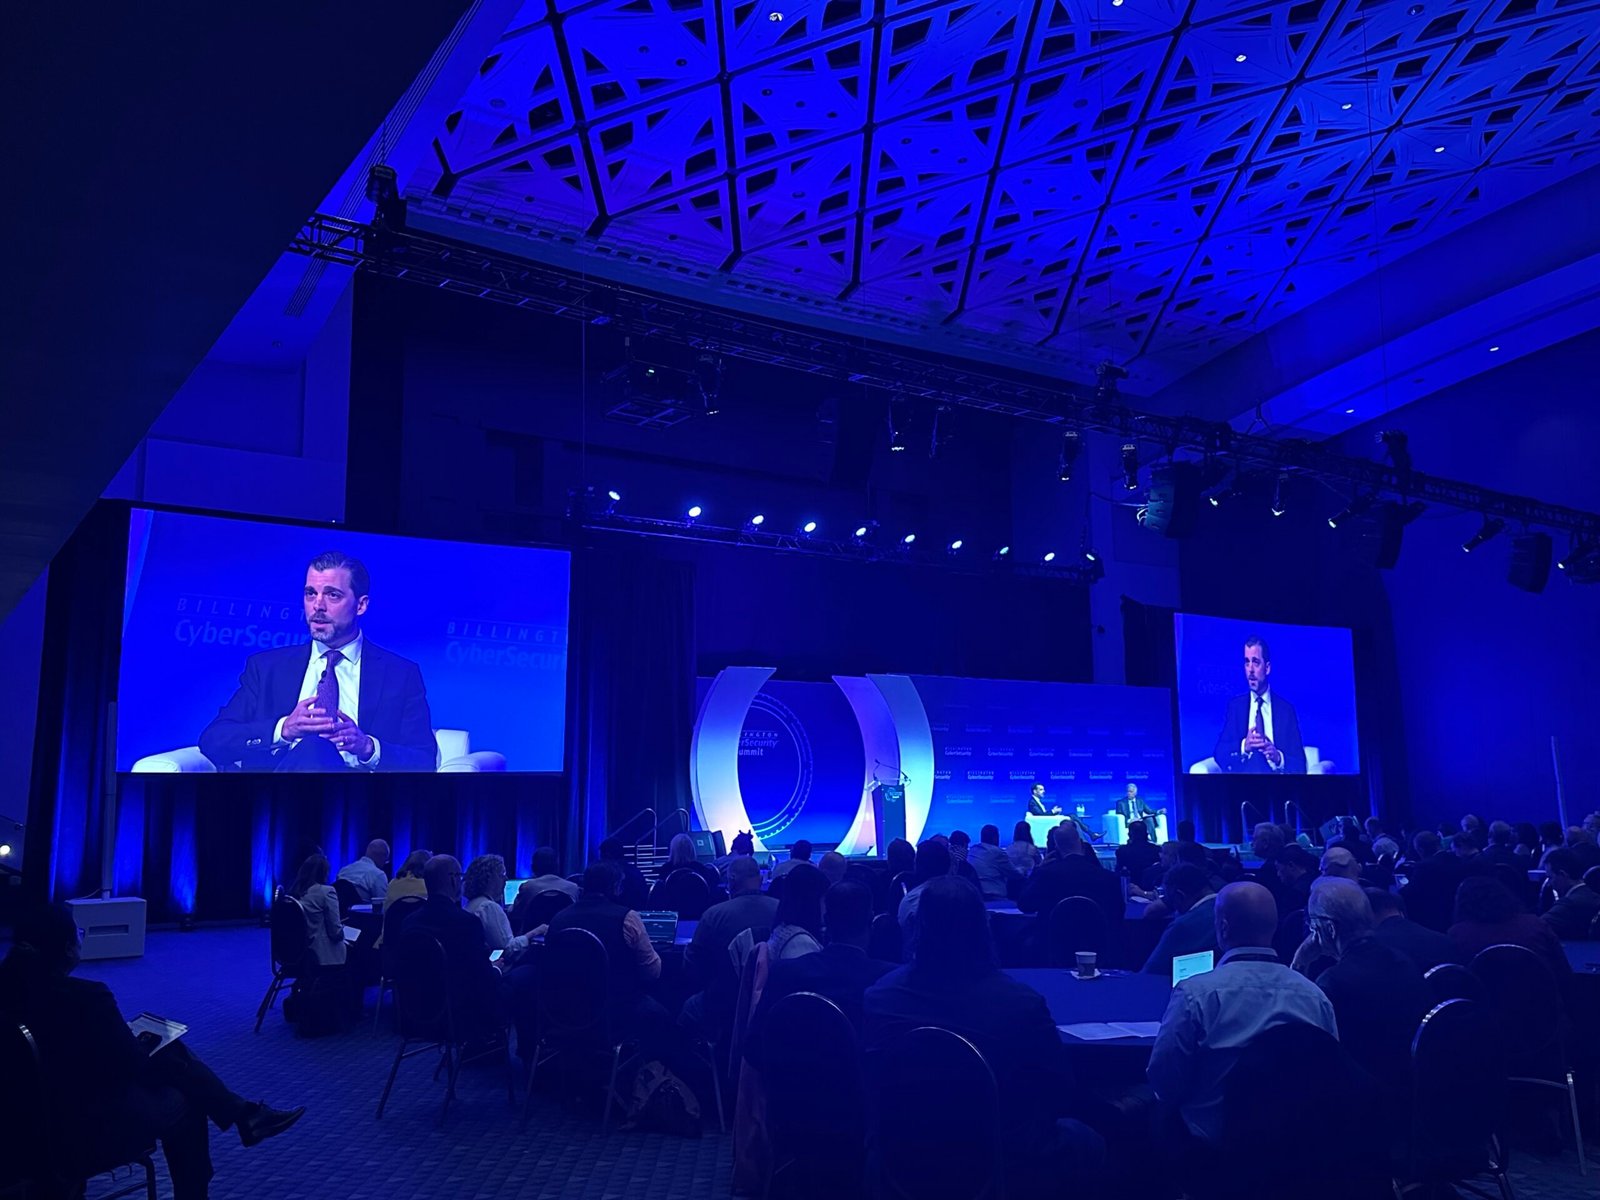
At a cybersecurity event in Washington, acting Chief Information Security Officer Michael Duffy outlined his top priorities for federal cybersecurity officials, emphasizing the importance of collaboration across government agencies. He highlighted three key focus areas: strengthening enterprise cyber defense, boosting operational resilience, and securing a modernized government system. Duffy revealed that in the coming month, the CISO Council will conduct a tabletop exercise aimed at fostering honest discussions among cybersecurity leaders about their readiness to respond to cyber incidents, ensuring they consider both technological and procedural factors—including having the right personnel on call and clear interagency collaboration processes. These efforts are driven by the understanding that cyber threats do not recognize agency boundaries, and a unified, whole-of-government approach is essential to closing vulnerabilities and adapting to evolving adversaries.
Duffy’s emphasis on these priorities reflects a strategic shift toward proactive stance and interagency teamwork, urging agencies to act swiftly rather than wait for crises. The focus on enterprise-wide defense underscores the need for shared responsibility and clear expectations across agencies, while resilience planning aims to preempt future attacks influenced by past incidents like the SolarWinds breach. Securing a modern government involves enhancing data security and privacy, especially as new technologies like AI and quantum cryptography are integrated. This outlook is part of a broader effort to modernize cybersecurity standards, with Duffy and federal leaders working together to develop policies that close gaps and safeguard the nation’s digital infrastructure, as reported by Madison Alder of FedScoop.
What’s at Stake?
The U.S. government’s acting Chief Information Security Officer, Michael Duffy, emphasized a comprehensive, collaborative approach to cybersecurity over the next year, highlighting three key priorities: enhancing enterprise cyber defense, boosting operational resilience, and securing a modern government infrastructure. He underscored the importance of cross-agency cooperation, exemplified by upcoming tabletop exercises designed to evaluate and improve readiness, processes, and interagency collaboration, recognizing that cyber threats do not respect organizational boundaries. Duffy stressed that focusing on vulnerabilities, supply chains, and incident responses collectively, rather than in isolation, is essential to prevent adversaries from exploiting gaps. He called for immediate, proactive action to fortify defenses, citing past breaches as stark reminders, and emphasized the need to integrate evolving technologies like AI and post-quantum cryptography to modernize government security and safeguard public data, all within a unified, resilient national cyber ecosystem.
Fix & Mitigation
Acting federal cyber chief outlines his three priorities for the next year, emphasizing the critical need for timely remediation to protect national security, infrastructure, and data integrity. Addressing vulnerabilities swiftly helps minimize damage, reduce recovery costs, and maintain public trust.
Rapid Response
- Immediate patching of known vulnerabilities
- Activation of incident response teams
- Conducting quick threat assessments
Proactive Measures
- Regular system updates and patches
- Implementing intrusion detection systems
- Ongoing security awareness training
Strategic Planning
- Developing comprehensive cybersecurity policies
- Conducting regular vulnerability assessments
- Coordinating with federal and private sector partners
Stay Ahead in Cybersecurity
Explore career growth and education via Careers & Learning, or dive into Compliance essentials.
Understand foundational security frameworks via NIST CSF on Wikipedia.
Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.
Cyberattacks-V1
