
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Expanding Attack Surfaces Increase Cyber Risk

November 10, 2026

Notion AI Chats Exposed in Fireworks Breach

November 10, 2026

Hackers Exploit Qubole’s AWS Access to Steal Customer Data

November 10, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » National Cyber Chief Unveils Top Three Priorities for Coming Year
Cybercrime and Ransomware

National Cyber Chief Unveils Top Three Priorities for Coming Year

Staff WriterBy Staff WriterSeptember 11, 2025No Comments4 Mins Read6 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Fast Facts

  1. The U.S. government’s acting CIO prioritizes enterprise cyber defense, operational resilience, and securing a modern government, emphasizing a whole-of-government approach.
  2. An upcoming tabletop exercise will focus on assessing agencies’ readiness for cyber incidents, including interagency collaboration and process improvements.
  3. Agencies are urged to act proactively on resilience and share best practices across government, as adversaries exploit gaps between agencies.
  4. Securing a modern government involves managing data and emerging technologies like AI and post-quantum cryptography, building on existing federal security frameworks.

The Issue

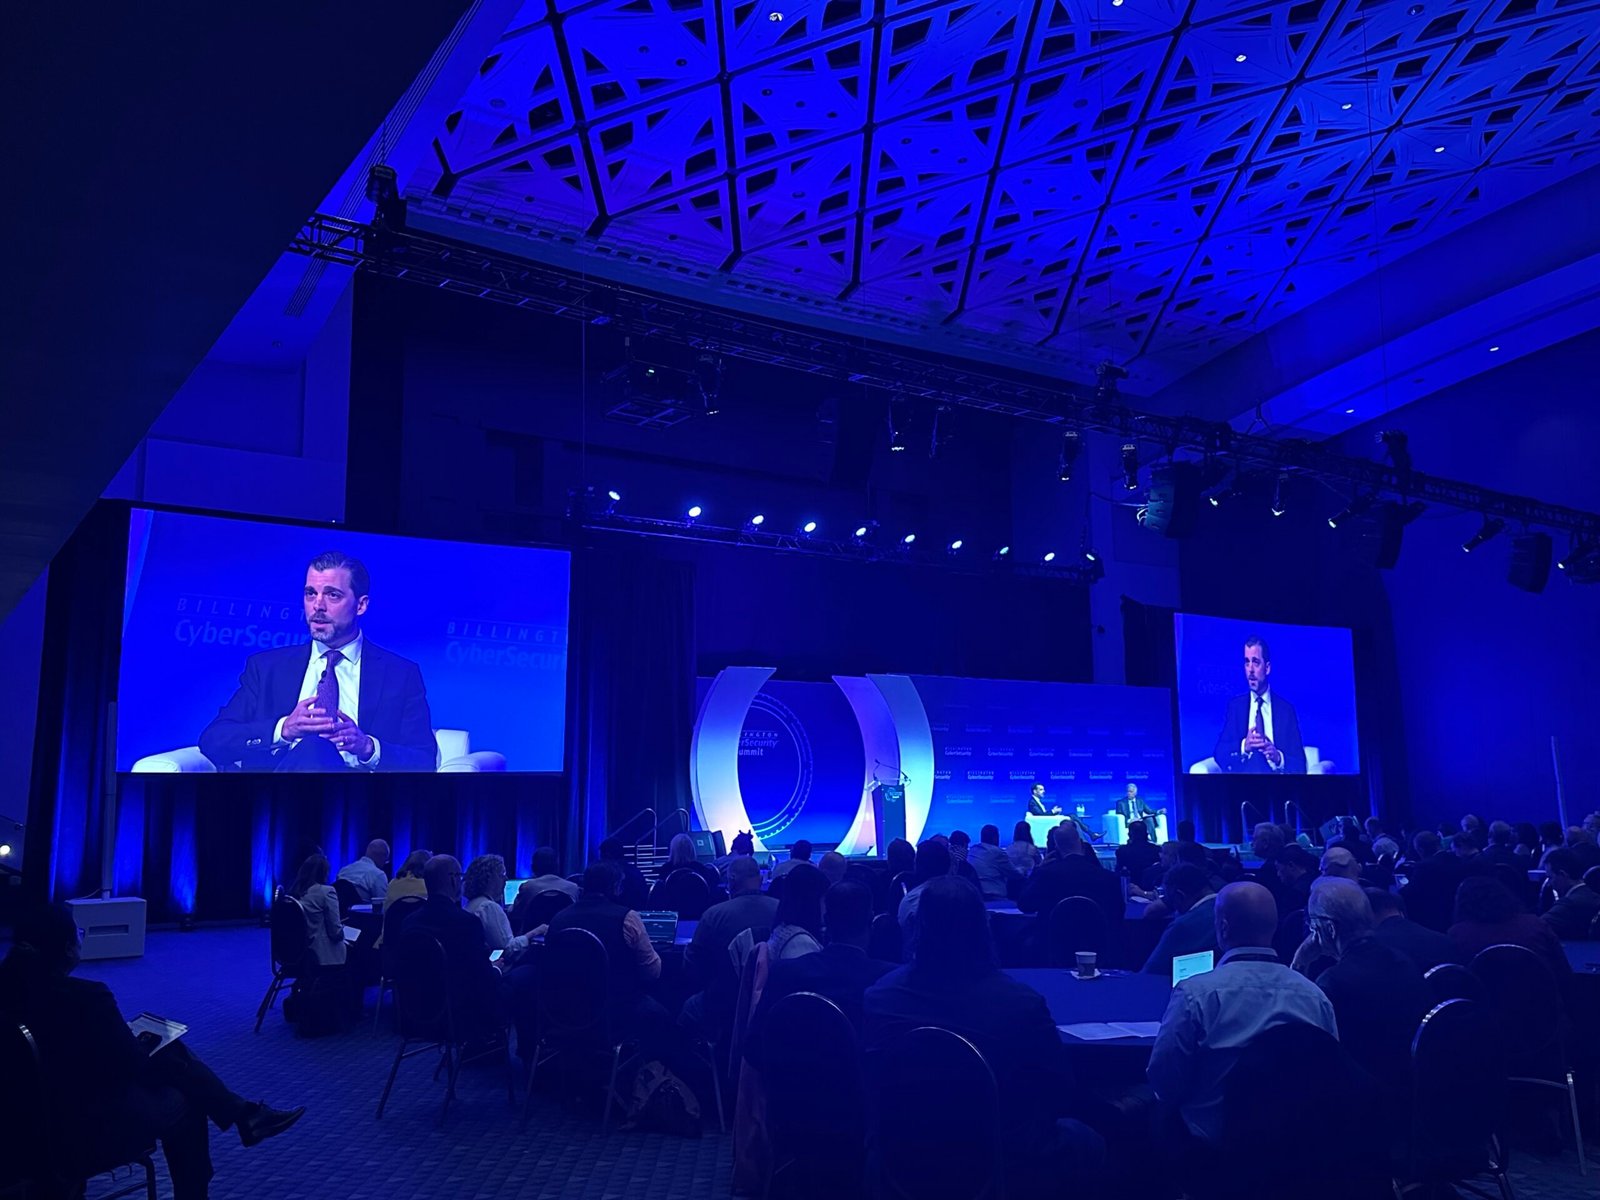
At a cybersecurity event in Washington, acting Chief Information Security Officer Michael Duffy outlined his top priorities for federal cybersecurity officials, emphasizing the importance of collaboration across government agencies. He highlighted three key focus areas: strengthening enterprise cyber defense, boosting operational resilience, and securing a modernized government system. Duffy revealed that in the coming month, the CISO Council will conduct a tabletop exercise aimed at fostering honest discussions among cybersecurity leaders about their readiness to respond to cyber incidents, ensuring they consider both technological and procedural factors—including having the right personnel on call and clear interagency collaboration processes. These efforts are driven by the understanding that cyber threats do not recognize agency boundaries, and a unified, whole-of-government approach is essential to closing vulnerabilities and adapting to evolving adversaries.

Duffy’s emphasis on these priorities reflects a strategic shift toward proactive stance and interagency teamwork, urging agencies to act swiftly rather than wait for crises. The focus on enterprise-wide defense underscores the need for shared responsibility and clear expectations across agencies, while resilience planning aims to preempt future attacks influenced by past incidents like the SolarWinds breach. Securing a modern government involves enhancing data security and privacy, especially as new technologies like AI and quantum cryptography are integrated. This outlook is part of a broader effort to modernize cybersecurity standards, with Duffy and federal leaders working together to develop policies that close gaps and safeguard the nation’s digital infrastructure, as reported by Madison Alder of FedScoop.

What’s at Stake?

The U.S. government’s acting Chief Information Security Officer, Michael Duffy, emphasized a comprehensive, collaborative approach to cybersecurity over the next year, highlighting three key priorities: enhancing enterprise cyber defense, boosting operational resilience, and securing a modern government infrastructure. He underscored the importance of cross-agency cooperation, exemplified by upcoming tabletop exercises designed to evaluate and improve readiness, processes, and interagency collaboration, recognizing that cyber threats do not respect organizational boundaries. Duffy stressed that focusing on vulnerabilities, supply chains, and incident responses collectively, rather than in isolation, is essential to prevent adversaries from exploiting gaps. He called for immediate, proactive action to fortify defenses, citing past breaches as stark reminders, and emphasized the need to integrate evolving technologies like AI and post-quantum cryptography to modernize government security and safeguard public data, all within a unified, resilient national cyber ecosystem.

Fix & Mitigation

Acting federal cyber chief outlines his three priorities for the next year, emphasizing the critical need for timely remediation to protect national security, infrastructure, and data integrity. Addressing vulnerabilities swiftly helps minimize damage, reduce recovery costs, and maintain public trust.

Rapid Response

  • Immediate patching of known vulnerabilities
  • Activation of incident response teams
  • Conducting quick threat assessments

Proactive Measures

  • Regular system updates and patches
  • Implementing intrusion detection systems
  • Ongoing security awareness training

Strategic Planning

  • Developing comprehensive cybersecurity policies
  • Conducting regular vulnerability assessments
  • Coordinating with federal and private sector partners

Stay Ahead in Cybersecurity

Explore career growth and education via Careers & Learning, or dive into Compliance essentials.

Understand foundational security frameworks via NIST CSF on Wikipedia.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

billington cybersecurity summit CISO Update Cybersecurity federal ciso federal ciso council michael duffy MX1 trump administration
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleAuthorities Crack Down on Major Ransomware Groups
Next Article Urgent: SonicWall Access Control Flaw Under Active Attack
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Expanding Attack Surfaces Increase Cyber Risk

November 10, 2026

Notion AI Chats Exposed in Fireworks Breach

November 10, 2026

Iranian Hackers Hijack Refrigeration at 700 Supermarkets

November 10, 2026

Comments are closed.

Latest Posts

Notion AI Chats Exposed in Fireworks Breach

November 10, 2026

Iranian Hackers Hijack Refrigeration at 700 Supermarkets

November 10, 2026

SonicWall patches 7 firewall flaws—most exploitable without login

November 10, 2026

China-Linked Hackers Deploy ARTEX AI Agents in ConnectWise Supply Chain Attack

November 10, 2026
Don't Miss

Expanding Attack Surfaces Increase Cyber Risk

By Staff WriterNovember 10, 2026

Essential Insights AI agents let solo operators develop exploits within hours and run multi-country attacks.…

Notion AI Chats Exposed in Fireworks Breach

November 10, 2026

Iranian Hackers Hijack Refrigeration at 700 Supermarkets

November 10, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Expanding Attack Surfaces Increase Cyber Risk
  • Notion AI Chats Exposed in Fireworks Breach
  • Hackers Exploit Qubole’s AWS Access to Steal Customer Data

  • Iranian Hackers Hijack Refrigeration at 700 Supermarkets

  • Mobile Threats in Q3 2026
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Expanding Attack Surfaces Increase Cyber Risk

November 10, 2026

Notion AI Chats Exposed in Fireworks Breach

November 10, 2026

Hackers Exploit Qubole’s AWS Access to Steal Customer Data

November 10, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026384 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026262 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.