
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension

November 15, 2026

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

November 15, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Critical Microsoft Entra ID Flaw Fixed: Global Admin Impersonation Risk Resolved!
Cyber Updates

Critical Microsoft Entra ID Flaw Fixed: Global Admin Impersonation Risk Resolved!

Staff WriterBy Staff WriterSeptember 22, 2025Updated:October 25, 2025No Comments3 Mins Read17 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Summary Points

  1. Token Validation Flaw: A severe vulnerability (CVE-2025-55241) in Microsoft Entra ID allows attackers to impersonate any user, including Global Administrators, across tenants, scoring 10.0 on the CVSS scale.

  2. Exploitation and Impact: This flaw permits attackers to bypass multi-factor authentication, access sensitive data, and gain full control of Azure resources, potentially compromising entire tenants without leaving logs.

  3. Legacy API Issues: The problem arises from inadequate validation in the deprecated Azure AD Graph API and flaws in service-to-service tokens, enabling unauthorized cross-tenant access.

  4. Urgent Migration Needed: Microsoft urges users to transition to the newer Microsoft Graph API before the deprecated Azure AD Graph API becomes unusable in September 2025, as continued reliance poses serious security risks.

Microsoft Addresses Critical Security Flaw in Entra ID

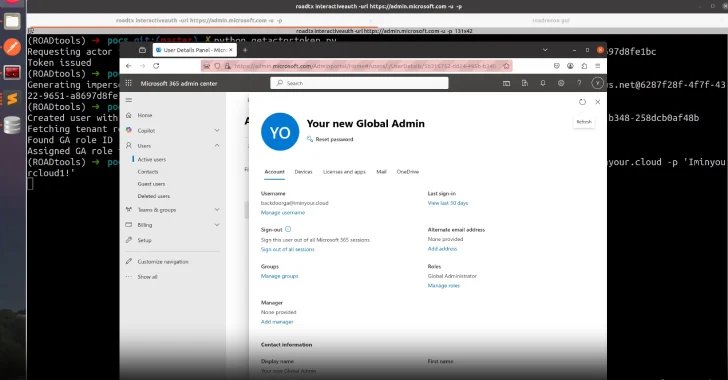
Microsoft recently patched a severe vulnerability in Entra ID, previously known as Azure Active Directory. This flaw, designated as CVE-2025-55241, allowed potential attackers to impersonate any user, including Global Administrators, across multiple tenants. It earned a maximum CVSS score of 10.0, highlighting its critical nature. Fortunately, there are no signs that the vulnerability had been exploited in the wild before the patch—deployed on July 17, 2025—requiring no additional actions from users.

The root of this issue lay in a combination of weaknesses involving actor tokens and the outdated Azure AD Graph API. Specifically, the flaw allowed unauthorized access to sensitive data, enabling attackers to manipulate accounts and permissions at will. Security researcher Dirk-jan Mollema emphasized that this vulnerability threatened virtually every Entra ID tenant globally, with narrow exceptions. The implications of such a breach could range from unauthorized data access to complete tenant compromise, affecting various Microsoft services.

Broader Implications for Cloud Security

The incident illustrates a significant concern regarding cloud security and identity management. Cross-tenant access, described by Microsoft as “High-privileged access,” represents a fundamental risk when applications or services acquire wide-ranging access without proper verification. Additionally, this vulnerability bypassed typical security measures like multi-factor authentication and logging, leaving little trace for potential victims.

As businesses increasingly rely on cloud infrastructure, the ramifications of such vulnerabilities can be severe. Organizations could face data theft, unauthorized access to sensitive resources, and the potential for significant disruption. Analysts and security firms contend that these types of flaws underscore the importance of rigorous testing and gradual phase-out of deprecated technologies, such as the Azure AD Graph API, which Microsoft has urged clients to avoid by migrating to Microsoft Graph.

Overall, the incident serves as a stark reminder of the complexities involved in managing identity and access within cloud environments, highlighting the ongoing need for vigilance and proactive measures in the face of evolving threats.

Discover More Technology Insights

Dive deeper into the world of Cryptocurrency and its impact on global finance.

Access comprehensive resources on technology by visiting Wikipedia.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleBlackLock Ransomware: Threatening Windows, Linux, and VMware ESXi Exploits
Next Article Urgent Fix: Critical Vulnerability in GoAnywhere MFT Exploited
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Bridging the Critical Confidence Gap in Enterprise AI Security

June 16, 2026

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Comments are closed.

Latest Posts

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

November 15, 2026

Maersk Probes Breach After WhiteArmor Claims 100GB Data Theft

November 14, 2026

AI Is Rewriting Cyberattacks

November 14, 2026
Don't Miss

Bridging the Critical Confidence Gap in Enterprise AI Security

By Staff WriterJune 16, 2026

Summary Points Current AI security testing methods, like tabletop exercises, fail to reveal how AI…

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension
  • Uber Confirms Breach: Users’ Personal Data Stolen
  • OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

  • Maersk Probes Breach After WhiteArmor Claims 100GB Data Theft

  • AI Is Rewriting Cyberattacks

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension

November 15, 2026

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

OT Cyber Readiness Assessment Exposes IT-OT Response Gaps

November 15, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026403 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026281 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.