

Fast Facts
- DERs and microgrids are transforming energy generation and consumption but expand the cyber attack surface, making them attractive targets for hackers including nation-states and ransomware groups.
- Common vulnerabilities include internet-exposed controllers, insecure vendor access, outdated firmware, and reliance on risky industrial protocols, which enable disruption and potential cascading failures across critical infrastructure.
- Adversaries are actively probing these assets, exploiting exposed systems, conducting campaigns such as credential phishing, ransomware attacks, and low-skill tactics like DoS and device reconnaissance.
- Securing DER and microgrids demands OT-specific visibility, threat detection, and resilient defense strategies—treating them as core OT assets with hardened architectures, secure remote access, and comprehensive incident response plans.
The Core Issue
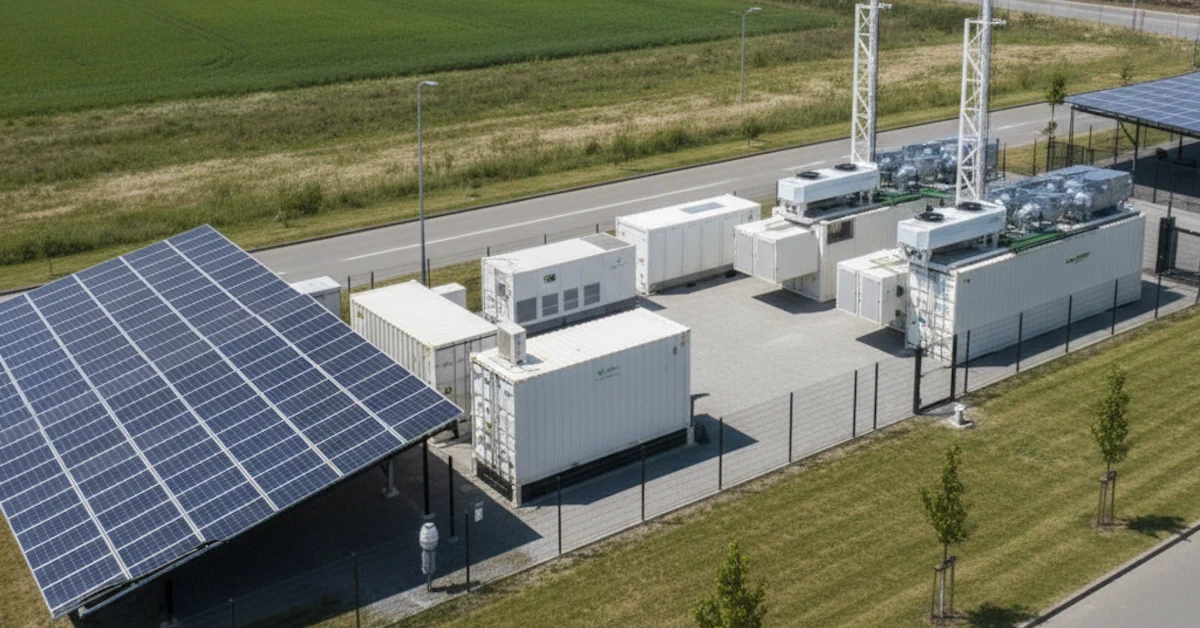
Recent findings by the cybersecurity firm Dragos reveal that as industries increasingly integrate distributed energy resources (DERs) and microgrids—such as solar panels, wind turbines, and local storage—these systems, once considered peripheral, have now become vital components of the modern energy infrastructure. However, this surge in adoption expands the attack surface, making these assets attractive targets for a variety of adversaries, including state-sponsored groups, ransomware operators, and hacktivists. These malicious actors exploit common vulnerabilities—like exposed controllers, insecure remote access, outdated firmware, and unencrypted communications—facilitating disruptions that can halt industrial processes, compromise critical infrastructure, or cause widespread outages. The report emphasizes that attackers are already probing these systems, with documented incidents involving infiltration via exposed firewalls and phishing campaigns aimed at harvesting credentials, aiming to gain persistence and cause operational chaos. To counter these threats, Dragos advocates for a strategic shift towards comprehensive operational technology (OT) visibility, threat detection, and resilient response plans, urging industries to treat DER and microgrids as core assets that require robust security measures aligned with established industrial cybersecurity standards.
The report underscores that the sophisticated exploitation of vulnerabilities in DER and microgrid infrastructure stems from their widespread deployment across geographically dispersed locations, often with minimal physical and cyber protections. The interconnected nature, necessary for real-time energy management and remote oversight, inadvertently broadens the attack surface, enabling adversaries to exploit shared protocols like IEC 61850, DNP3, and Modbus, which are vital for system integration but prone to misuse. Recognizing the escalating risks, Dragos reports that malicious groups are actively scanning and probing these environments, using tactics such as device reconnaissance, denial-of-service attacks, and malware campaigns to undermine the grid’s stability. To mitigate these threats, organizations are urged to implement fortified security architectures—restrict internet exposure, enforce multi-factor authentication for remote access, monitor protocol communications, and actively test incident response plans—reflecting a growing consensus on the need for specialized OT security measures in the face of emerging cyber threats.
Potential Risks
The integration of distributed energy resources (DERs) and microgrids into industrial operations presents both a transformative advantage and a significant cyber risk, as highlighted by Dragos. These assets are increasingly used across sectors such as manufacturing, oil and gas, and data centers for cost savings and resilience, but their widespread deployment expands the attack surface. Vulnerabilities stem from internet-exposed controllers, insecure remote access, legacy configurations, and reliance on vulnerable protocols like IEC 61850 and DNP3, allowing adversaries—from ransomware groups to nation-state actors—to execute disruptive actions like unauthorized shutdowns, ransomware infections, or data theft. Proven attack methods include exploiting firmware flaws, phishing, DDoS, and device reconnaissance, with real-world groups already probing these defenses, risking operational shutdowns and widespread outages. Effective mitigation demands OT-specific visibility, threat detection, and resilient security practices—moving beyond traditional IT security—such as minimizing internet exposure, securing remote access, monitoring protocols, and testing incident response plans, to prevent adversary infiltration and safeguard critical infrastructure.
Possible Remediation Steps
In the rapidly evolving landscape of energy infrastructure, swift and effective remediation of cyber threats targeting distributed energy and industrial microgrids is essential to prevent catastrophic failures, safeguard critical assets, and ensure uninterrupted power delivery.
Mitigation Steps:
- Implement advanced threat detection tools
- Conduct regular vulnerability assessments
- Strengthen network security protocols
Remediation Steps:
- Contain and isolate affected systems
- Perform forensic analysis to understand breach
- Apply necessary patches and updates
- Restore systems from secure backups
- Enhance staff training on cybersecurity best practices
Stay Ahead in Cybersecurity
Discover cutting-edge developments in Emerging Tech and industry Insights.
Understand foundational security frameworks via NIST CSF on Wikipedia.
Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.
Cyberattacks-V1
