
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Claude Code File Exposes Secrets in 1,122 Public GitHub Copies

November 7, 2026

Binance Heist Exposes AI Governance and Security Failures

November 7, 2026

GPT-6 Cyber: Better Performance, Stronger Guardrails

November 7, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Claude Code File Exposes Secrets in 1,122 Public GitHub Copies
Uncategorized

Claude Code File Exposes Secrets in 1,122 Public GitHub Copies

Staff WriterBy Staff WriterNovember 7, 2026No Comments3 Mins Read2 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Quick Takeaways

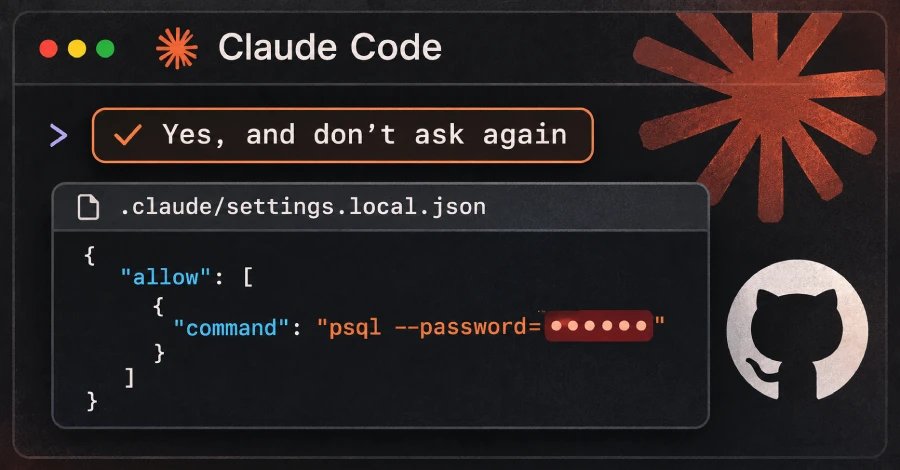
  1. “Yes, and don’t ask again” can save commands verbatim—including passwords and API keys—in .claude/settings.local.json.
  2. Apiiro found 1,122 public files containing 1,379 secrets; broader checks found 2,539 secrets across repositories, histories, and logs.
  3. Deleting the file isn’t enough: secrets can remain in Git history, forks, and other shared copies; some had been exposed for months.
  4. Rotate exposed credentials first, then clean Git history, add the file to .gitignore, and keep secrets out of commands.

A Convenience Setting Can Preserve Secrets

A Claude Code setting meant to save time may also save passwords and access keys. When developers choose “Yes, and don’t ask again,” the tool can store the approved command in a project file. If that command contains a secret, the file may preserve it in plain text.

Security researchers found at least one secret in 1,122 public copies of the file on GitHub. Those copies held 1,379 different secrets, including database passwords, login details, and cloud access keys. The researchers did not test whether every secret still worked. However, one company they contacted confirmed that its key remained active.

Claude Code tries to keep this local settings file out of Git, a system that tracks changes to software projects. But that protection applies only to one user’s computer. It cannot protect a file that someone already uploaded. Even after deletion, earlier versions and copies in other repositories may remain.

The feature shows a practical trade-off in AI coding tools: fewer interruptions can help developers work faster, but convenience can also carry risks when a command includes sensitive information.

How Developers Can Reduce the Risk

Developers should change any password, token, or key that appeared in an exposed file. They should do this before removing the file, because deletion does not erase older copies.

Teams should also check project history for the file and add it to the project’s ignore list. Developers can keep secrets out of commands by using references to a secure password store instead. They can also approve command patterns, rather than exact commands that may contain private details.

Common security scanners did not catch every exposed file. Therefore, teams should review AI tool folders and saved command files as carefully as they review other places where secrets may appear. As AI assistants become part of everyday software work, safe habits will help people gain their speed without giving away the keys to their systems.

Continue Your Tech Journey

Explore the future of technology with our detailed insights on Artificial Intelligence.

Explore past and present digital transformations on the Internet Archive.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous Article

Binance Heist Exposes AI Governance and Security Failures

Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Chainalysis Breach Exposes All User Credentials, Shuts Key Services

November 6, 2026

Hijacked cPGuard Updates Backdoor Linux Servers, Harvest Password Hashes

November 4, 2026

Fake Interviews, AI Abuse: The $6.43B Crypto Heist

November 4, 2026

Comments are closed.

Latest Posts

Binance Heist Exposes AI Governance and Security Failures

November 7, 2026

GPT-6 Cyber: Better Performance, Stronger Guardrails

November 7, 2026

PHP2Shell Exploit Attempt Came 4 Days Before Disclosure

November 7, 2026

Exposed OT Controllers Disrupt Supermarket Cooling Across Europe

November 6, 2026
Don't Miss

Chainalysis Breach Exposes All User Credentials, Shuts Key Services

By Staff WriterNovember 6, 2026

Quick Takeaways Chainalysis exposed sensitive user data: Its investigation found names, usernames, password hashes, and…

Hijacked cPGuard Updates Backdoor Linux Servers, Harvest Password Hashes

November 4, 2026

Fake Interviews, AI Abuse: The $6.43B Crypto Heist

November 4, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Claude Code File Exposes Secrets in 1,122 Public GitHub Copies
  • Binance Heist Exposes AI Governance and Security Failures

  • GPT-6 Cyber: Better Performance, Stronger Guardrails
  • PHP2Shell Exploit Attempt Came 4 Days Before Disclosure
  • Exposed OT Controllers Disrupt Supermarket Cooling Across Europe

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Claude Code File Exposes Secrets in 1,122 Public GitHub Copies

November 7, 2026

Binance Heist Exposes AI Governance and Security Failures

November 7, 2026

GPT-6 Cyber: Better Performance, Stronger Guardrails

November 7, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026371 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026247 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.