
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

PHP Patches Two Critical PHP2Shell Flaws as Exploits Emerge

November 16, 2026

2,700 Passwords Crack SQL Servers, Install Remote-Access Malware

November 15, 2026

Why Does Access Outlast the Job?

November 15, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » PHP Patches Two Critical PHP2Shell Flaws as Exploits Emerge
Cybercrime and Ransomware

PHP Patches Two Critical PHP2Shell Flaws as Exploits Emerge

Staff WriterBy Staff WriterNovember 16, 2026No Comments3 Mins Read0 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Fast Facts

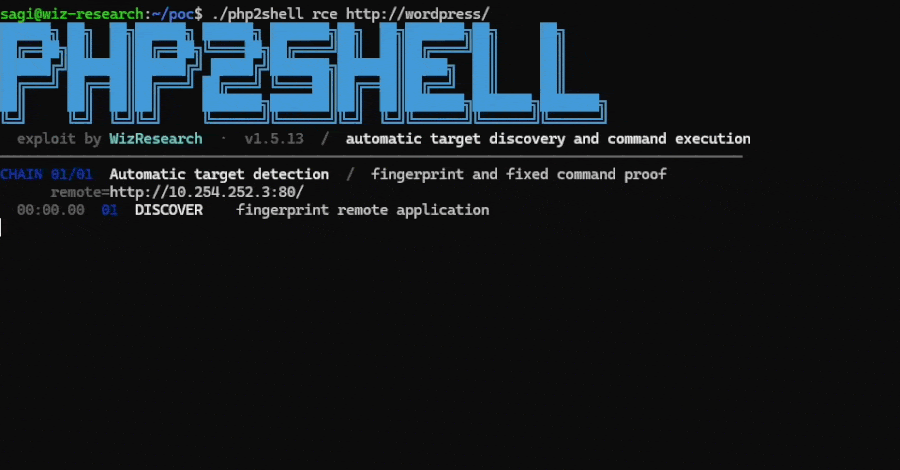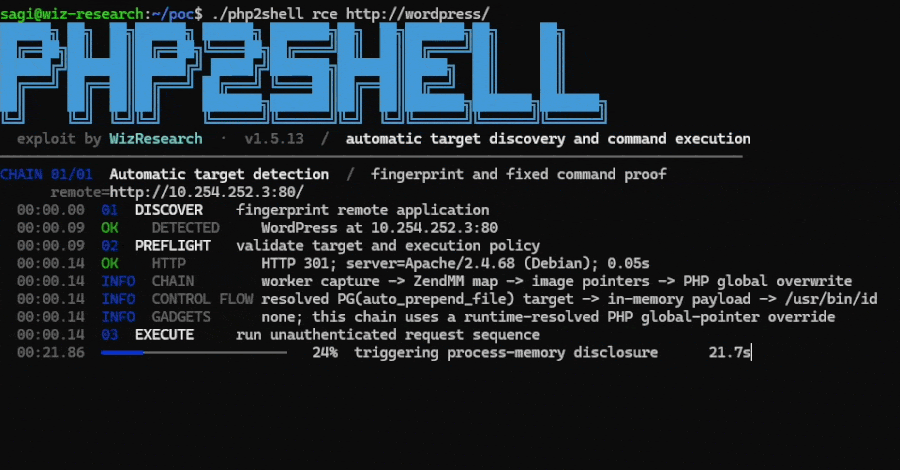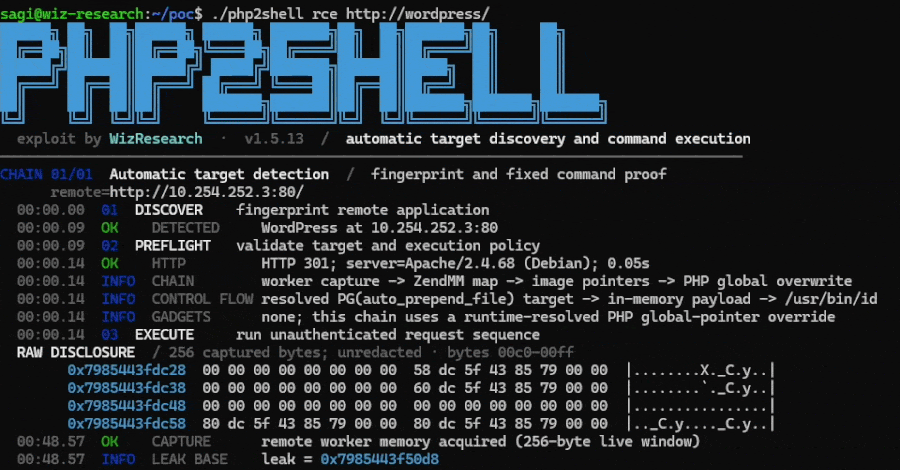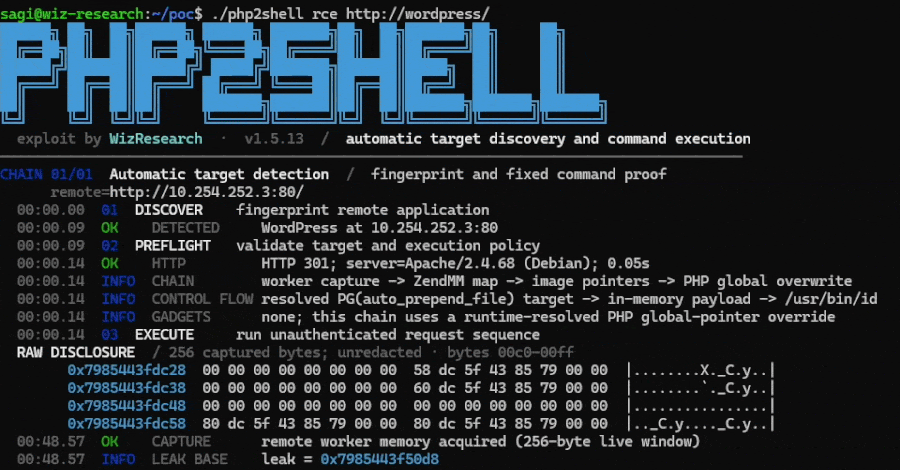
  1. Critical PHP2Shell flaws (CVSS 9.2) can enable unauthenticated code execution and expose sensitive PHP worker memory—even when the application itself is secure.

  2. All web-serving PHP setups are affected, including Apache mod_php, PHP-FPM, CGI, FrankenPHP, and LiteSpeed; mod_php is highlighted as especially exposed.

  3. Patch immediately: install PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 (or your vendor’s patched package), then restart PHP services and workers.

  4. Workarounds are not a complete fix. Exploitation attempts were reported, but no confirmed breach was reported in the article; review logs and watch for suspicious requests, errors, cookies, or worker restarts.

PHP has issued emergency updates for two critical flaws that could let attackers run code on vulnerable web servers without an account. Security teams have reported attempts to exploit the flaws, but no successful break-in has been confirmed.

What the Flaws Mean for PHP Servers

The flaws, known together as PHP2Shell, affect the PHP runtime—the software that runs PHP sites. As a result, even a secure website can face risk if its server uses an unpatched PHP version. The danger is greatest for servers that use Apache’s mod_php, where one request may trigger an attack before the website’s own code runs.

PHP rates both flaws 9.2 out of 10 for severity. The fixes appear in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Older versions also face risk, though some no longer receive updates from the PHP project.

Meanwhile, reports of attack attempts make prompt action important. However, attempts do not prove that attackers have broken into a specific server. Some organizations temporarily took services offline as a precaution, showing how a software flaw can disrupt services people rely on for work and everyday tasks.

How Administrators Can Respond

Administrators should update the PHP runtime that handles web requests, then restart the related server processes. Updating a website or its applications alone does not fix the PHP software underneath them. Hosts and organizations should also check whether their system vendor has included the security fixes in its packages.

PHP says only an update fully protects a server. Some settings can reduce exposure while administrators prepare a fix, but they do not remove the risk. After updating, teams should review memory limits and watch for unusual requests, repeated server errors or unexplained worker restarts.

The incident also highlights a practical challenge: PHP runs a large range of websites and services, so a flaw in the shared runtime can affect many systems at once. Fast updates help protect that broad ecosystem—and the people who depend on it.

Discover More Technology Insights

Dive deeper into the world of Cryptocurrency and its impact on global finance.

Explore past and present digital transformations on the Internet Archive.

CyberAttacks-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous Article

2,700 Passwords Crack SQL Servers, Install Remote-Access Malware

Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

2,700 Passwords Crack SQL Servers, Install Remote-Access Malware

November 15, 2026

Why Does Access Outlast the Job?

November 15, 2026

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

Comments are closed.

Latest Posts

PHP Patches Two Critical PHP2Shell Flaws as Exploits Emerge

November 16, 2026

2,700 Passwords Crack SQL Servers, Install Remote-Access Malware

November 15, 2026

Why Does Access Outlast the Job?

November 15, 2026

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026
Don't Miss

2,700 Passwords Crack SQL Servers, Install Remote-Access Malware

By Staff WriterNovember 15, 2026

Quick Takeaways Attackers are brute-forcing internet-exposed Microsoft SQL Server systems using more than 2,700 passwords,…

Why Does Access Outlast the Job?

November 15, 2026

Uber Confirms Breach: Users’ Personal Data Stolen

November 15, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • PHP Patches Two Critical PHP2Shell Flaws as Exploits Emerge
  • 2,700 Passwords Crack SQL Servers, Install Remote-Access Malware

  • Why Does Access Outlast the Job?

  • Stolen Fireworks AI Key Linked to Trojanized Claude Code Extension
  • Uber Confirms Breach: Users’ Personal Data Stolen
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

PHP Patches Two Critical PHP2Shell Flaws as Exploits Emerge

November 16, 2026

2,700 Passwords Crack SQL Servers, Install Remote-Access Malware

November 15, 2026

Why Does Access Outlast the Job?

November 15, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026404 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026283 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.