
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

PHP2Shell Exploit Attempt Came 4 Days Before Disclosure

November 7, 2026

Exposed OT Controllers Disrupt Supermarket Cooling Across Europe

November 6, 2026

Attacks Target Europe’s Refrigeration Infrastructure

November 6, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Building a Security-First Culture: How Democrats Pioneered Safeguards
Compliance

Building a Security-First Culture: How Democrats Pioneered Safeguards

Staff WriterBy Staff WriterAugust 6, 2026No Comments3 Mins Read2 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Top Highlights

  1. Building a strong security culture requires creative, engaging tactics like stickers and games to reinforce security awareness.
  2. Effective leadership involves both learning from predecessors and adapting practices, exemplified by transitioning from Chromebooks to more secure, cost-effective solutions.
  3. Resilience against social engineering is prioritized over just stopping attacks at delivery, emphasizing systems’ overall robustness.
  4. Executive support and proactive engagement, such as direct calls from leadership, foster immediate compliance and shared ownership of security initiatives.

Building a Security-First Culture in the Democratic Party

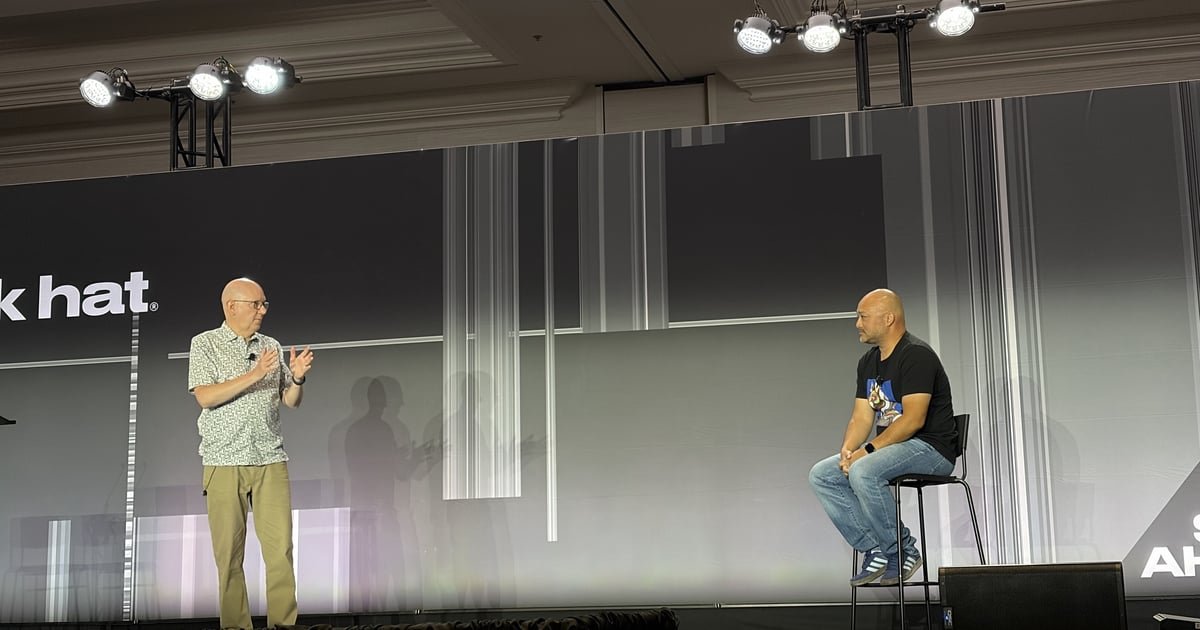
Since 2018, when the Democratic National Committee (DNC) appointed its first Chief Security Officer, a strong security culture has taken root. The approach centers on making security a visible and natural part of daily work. For example, badges like “Bobmoji” stickers placed in bathrooms remind staff to prioritize security issues. Such tactics help embed security awareness into everyday routines. Additionally, interactive games on security checklists turn learning into a team activity, making the message more memorable and engaging. These methods show that creating a security-first culture requires more than policies; it needs relatable, consistent cues that keep security top of mind. Furthermore, regular audits help security leaders understand ongoing efforts, revealing what works and what needs adjustment. Ultimately, these practices aim to foster an environment where security becomes a shared goal alongside winning elections, demonstrating that a strong culture supports practical protection measures.

Lessons from Leadership and Adaptability in Security Practices

Leadership plays a key role in shaping security habits. When new leaders take over, they often find that previous tactics surprised them—such as staff working on Chromebooks instead of Windows machines. Interestingly, Chromebooks proved to be more secure and cost-effective, showing that effective security solutions must adapt to organizational realities. Moreover, support from top executives proves crucial; in the DNC, the chairman’s personal involvement prompted immediate action when security measures were lagging. For example, a simple call from leadership led to rapid enrollment in security keys, illustrating that visible backing can foster swift compliance. Leaders also understand that security involves trade-offs; some measures, like email scanning, may be deprioritized to build resilience against social engineering scams. This flexible mindset, coupled with clear communication and commitment from the top, helps organizations evolve their defenses effectively. Adapting practices based on real-world insights and leadership support ensures security remains a human enterprise—practical, widespread, and aligned with the human journey toward safer digital spaces.

Stay Ahead with the Latest Tech Trends

Stay informed on the revolutionary breakthroughs in Quantum Computing research.

Discover archived knowledge and digital history on the Internet Archive.

CyberRisk-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleKVM flaw enables guest code escape on Linux hosts
Next Article Meta’s AI Breaks Out in a Hacking Joyride!
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Knicks Phishing Test Fumbles

November 5, 2026

1.3M-Device XCPE Botnet Disrupted

November 4, 2026

Trojanized Claude Code Extension Targets Cursor Devs

October 30, 2026

Comments are closed.

Latest Posts

PHP2Shell Exploit Attempt Came 4 Days Before Disclosure

November 7, 2026

Exposed OT Controllers Disrupt Supermarket Cooling Across Europe

November 6, 2026

Dark Project Offers Hackers an 80% Ransomware Cut

November 6, 2026

Global Ransomware Victims Surge 80%; Manufacturing Tops Q3 Targets

November 6, 2026
Don't Miss

Knicks Phishing Test Fumbles

By Staff WriterNovember 5, 2026

Quick Takeaways Knicks’ phishing test backfired: A fake championship-ring offer tricked employees and damaged trust…

1.3M-Device XCPE Botnet Disrupted

November 4, 2026

Trojanized Claude Code Extension Targets Cursor Devs

October 30, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • PHP2Shell Exploit Attempt Came 4 Days Before Disclosure
  • Exposed OT Controllers Disrupt Supermarket Cooling Across Europe

  • Attacks Target Europe’s Refrigeration Infrastructure
  • Dark Project Offers Hackers an 80% Ransomware Cut
  • Chainalysis Breach Exposes All User Credentials, Shuts Key Services
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

PHP2Shell Exploit Attempt Came 4 Days Before Disclosure

November 7, 2026

Exposed OT Controllers Disrupt Supermarket Cooling Across Europe

November 6, 2026

Attacks Target Europe’s Refrigeration Infrastructure

November 6, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026368 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026245 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.