
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Cortex XDR + Claude Cowork: Secure Desktop AI

November 10, 2026

China-Linked Hackers Deploy ARTEX AI Agents in ConnectWise Supply Chain Attack

November 10, 2026

7 Tips to Boost Defensive Agility

November 9, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » China-Linked Hackers Deploy ARTEX AI Agents in ConnectWise Supply Chain Attack
Cybercrime and Ransomware

China-Linked Hackers Deploy ARTEX AI Agents in ConnectWise Supply Chain Attack

Staff WriterBy Staff WriterNovember 10, 2026No Comments2 Mins Read1 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Essential Insights

  1. China-linked Storm-0940 exploited ConnectWise Cloud Backup, using the ARTEX AI framework to automate attacks across hundreds of organizations.
  2. AI enabled attacks at “machine speed”—including password spraying, reconnaissance, and abuse of trusted OAuth applications—with attempts reaching 2,900 sign-ins per minute.
  3. Stolen app credentials opened paths into customer cloud environments, where attackers attempted reconnaissance, persistence, and privilege changes; some campaigns reached privileged access in under three hours.
  4. The campaign highlights supply-chain risks and AI-enabled scale: defenders must rapidly detect suspicious app access, credential changes, and automated attacks across vendors and MSPs.

AI Agents Accelerate a Supply-Chain Attack

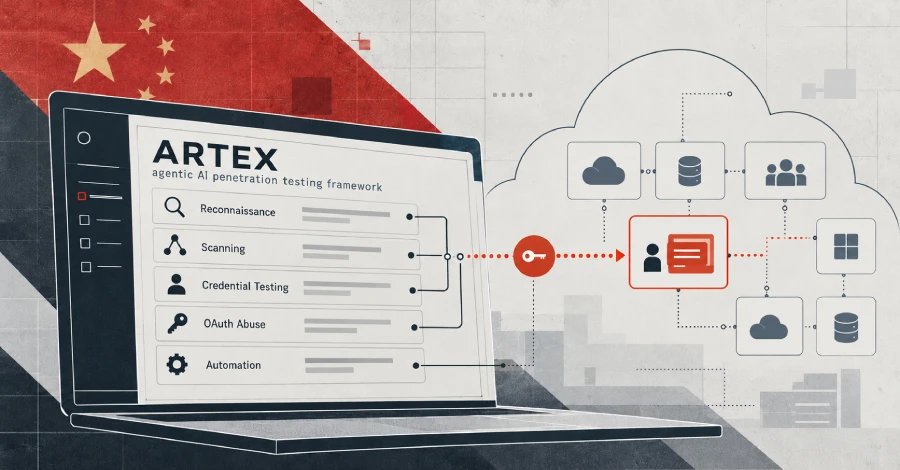
Microsoft says China-linked hacking group Storm-0940 used ARTEX, an AI-powered testing tool, during a supply-chain attack involving ConnectWise Cloud Backup. The tool helped automate scanning, password attempts and efforts to misuse trusted cloud applications.

Between October 10 and 14, 2026, the group targeted 327 accounts across eight organizations. Microsoft recorded more than 151,000 failed sign-ins, but found no successful access during that password-spraying campaign. On October 15, however, attackers used stolen identities for ConnectWise cloud applications to try to enter customer environments.

The activity reached as many as 2,900 sign-in attempts per minute. In some environments, the agents also examined cloud systems and tried to change credentials or permissions. Such changes can leave a way back in, even after a company blocks the original compromised application.

Trusted Connections Raise the Stakes

A software supplier can connect to many customer systems. Therefore, attackers who compromise a trusted application may gain a path to multiple organizations. ConnectWise said it temporarily shut down services and began restoring them in stages.

AI agents can work continuously and test many routes at once. That speed may make attacks easier to scale, but it does not make every attempt successful. The incident’s failed sign-ins show that monitoring and access controls still matter. Companies can reduce risk by limiting app permissions, checking cloud activity and quickly removing credentials they no longer trust.

As more businesses adopt AI tools for routine work, the same technology may help people solve problems faster. However, this attack shows why organizations must also plan for criminals to use automation. Stronger safeguards can help preserve the benefits of connected services without asking customers to trust them blindly.

Stay Ahead with the Latest Tech Trends

Stay informed on the revolutionary breakthroughs in Quantum Computing research.

Explore past and present digital transformations on the Internet Archive.

CyberAttacks-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous Article7 Tips to Boost Defensive Agility
Next Article

Cortex XDR + Claude Cowork: Secure Desktop AI

Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

7 Tips to Boost Defensive Agility

November 9, 2026

AI Can Break the World Without Going Rogue

November 9, 2026

Why Email Security Thinks Like Napoleon

November 9, 2026

Comments are closed.

Latest Posts

China-Linked Hackers Deploy ARTEX AI Agents in ConnectWise Supply Chain Attack

November 10, 2026

7 Tips to Boost Defensive Agility

November 9, 2026

AI Can Break the World Without Going Rogue

November 9, 2026

Why Email Security Thinks Like Napoleon

November 9, 2026
Don't Miss

7 Tips to Boost Defensive Agility

By Staff WriterNovember 9, 2026

Essential Insights Build on zero trust: Continuously verify users, devices, and applications, embedding security into…

AI Can Break the World Without Going Rogue

November 9, 2026

Why Email Security Thinks Like Napoleon

November 9, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Cortex XDR + Claude Cowork: Secure Desktop AI

  • China-Linked Hackers Deploy ARTEX AI Agents in ConnectWise Supply Chain Attack
  • 7 Tips to Boost Defensive Agility
  • Hacker Uses AI Agents to Steal Taipei Dispatch Records

  • Attackers Hunt SAP NetWeaver Webshells
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Cortex XDR + Claude Cowork: Secure Desktop AI

November 10, 2026

China-Linked Hackers Deploy ARTEX AI Agents in ConnectWise Supply Chain Attack

November 10, 2026

7 Tips to Boost Defensive Agility

November 9, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026380 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026259 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.