
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

TASK#STOMP PowerShell malware exfiltrates sensitive data and credentials

September 21, 2026

PNG steganography used for covert data exfiltration

September 21, 2026

ClickFix Lures with ChainScript RAT on Polygon Network

September 21, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » DragonForce Claims Responsibility for Belk Data Breach
Uncategorized

DragonForce Claims Responsibility for Belk Data Breach

Staff WriterBy Staff WriterJuly 15, 2025No Comments2 Mins Read6 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Quick Takeaways

  1. Attack Claim: The cybercriminal group DragonForce has claimed responsibility for a recent data breach at Belk, a North Carolina department store chain, boasting approximately 156 GB of stolen data.

  2. Established Patterns: DragonForce is linked to a broader series of attacks on retail firms, including a significant breach of Marks & Spencer, indicating a collaboration with another group, Scattered Spider.

  3. Ransomware-as-a-Service Model: DragonForce operates as a Ransomware-as-a-Service, allowing various affiliates to access its infrastructure, complicating the identification of specific victims.

  4. Expanding Target Base: The group’s operations affect notable retailers in both the U.S. and the U.K., with evolving focus shifting towards new sectors like insurance and airlines after recent campaigns.

The Rise of DragonForce

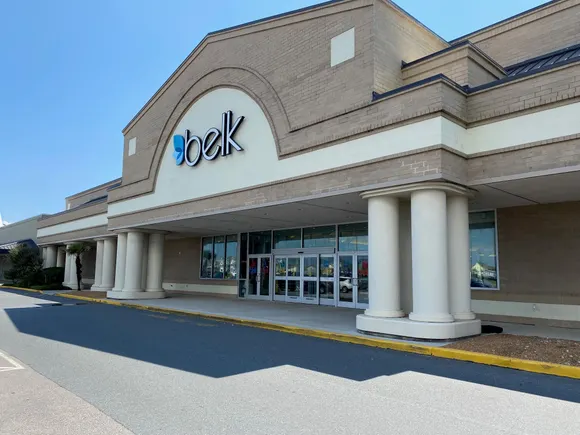
DragonForce, a cybercriminal group, has recently claimed responsibility for a significant data breach at Belk, a North Carolina-based department store chain. The group asserts that it stole approximately 156 gigabytes of data. This attack aligns with DragonForce’s ongoing spree against retail firms, raising alarms about security in the industry.

Researchers have tied DragonForce to an earlier attack on Marks & Spencer, marking the start of an unsettling trend in which multiple high-profile retailers have fallen victim. DragonForce operates on a model known as Ransomware-as-a-Service, allowing various affiliates to access its leak site and target different victims. Consequently, this structure complicates attempts to track individual breaches. Thus, the challenges in cybersecurity grow even more complex.

Implications for Retail Security

The impact of DragonForce’s actions is profound. As breaches affect well-known retailers like Harrods and Victoria’s Secret, the need for robust cybersecurity becomes clearer. These incidents have forced companies to reevaluate their security protocols, particularly in industries that traditionally relied heavily on customer trust.

Meanwhile, DragonForce continues to evolve. Following its rebranding as a cartel, it allows other operators to utilize its hacking infrastructure, increasing its reach and influence. The ongoing cyber threats highlight the urgency for retailers to adopt advanced security measures and foster a culture of vigilance. This situation serves as a critical reminder of the evolving landscape of cybercrime, emphasizing the need for continuous improvement in cybersecurity practices.

Stay Ahead with the Latest Tech Trends

Stay informed on the revolutionary breakthroughs in Quantum Computing research.

Stay inspired by the vast knowledge available on Wikipedia.

Cybersecurity-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticlePolice Unravel Ransomware Gang Targeting NAS Devices
Next Article Businesses’ Overconfidence Fuels Mobile Phishing Surge
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies

September 19, 2026

Gyazo Breach Exposes Over 23 Million User Records and Nearly 500 Million Image Metadata Entries

September 17, 2026

Russian State Hackers Rebuild Malware Using Claude After Detection

September 11, 2026
Leave A Reply Cancel Reply

Latest Posts

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Suspected China-Linked Group Exploits VMware Flaw to Launch Babuk Ransomware

September 16, 2026

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026

TWINLOOT Exploits SharePoint and Teams to Steal Credentials and Lateral Movement

September 10, 2026
Don't Miss

CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies

By Staff WriterSeptember 19, 2026

Essential Insights CrowdSec’s private GitHub repositories were copied by an attacker using an employee’s compromised…

Gyazo Breach Exposes Over 23 Million User Records and Nearly 500 Million Image Metadata Entries

September 17, 2026

Russian State Hackers Rebuild Malware Using Claude After Detection

September 11, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • TASK#STOMP PowerShell malware exfiltrates sensitive data and credentials
  • PNG steganography used for covert data exfiltration
  • ClickFix Lures with ChainScript RAT on Polygon Network
  • Setting the Benchmark for AI Security
  • Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

TASK#STOMP PowerShell malware exfiltrates sensitive data and credentials

September 21, 2026

PNG steganography used for covert data exfiltration

September 21, 2026

ClickFix Lures with ChainScript RAT on Polygon Network

September 21, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026203 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026202 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026200 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.