
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Jaguar Land Rover Set to Reignite Manufacturing Soon
Cyber Updates

Jaguar Land Rover Set to Reignite Manufacturing Soon

Staff WriterBy Staff WriterSeptember 29, 2025Updated:October 25, 2025No Comments3 Mins Read4 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Top Highlights

  1. Production Resumption: Jaguar Land Rover plans to restart some production shortly, following a cyberattack that occurred nearly a month ago and disrupted operations.

  2. Cyberattack Consequences: The attack, disclosed on September 2, involved stolen customer data and led to significant production and retail capacity disruptions.

  3. Government Support: The U.K. Department for Business and Trade announced a $2 billion loan guarantee to aid JLR in recovering and supporting its severely impacted supply chain.

  4. Economic Importance: JLR is a key exporter and employer in the U.K., supporting 34,000 direct jobs and a supply chain that employs around 120,000 workers.

Resuming Production and Recovery

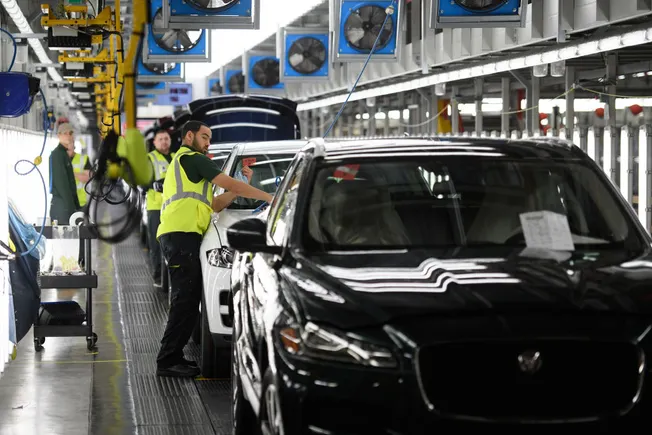
Jaguar Land Rover (JLR) is set to restart some manufacturing within days, marking a significant step in its recovery from a cyberattack that occurred nearly a month ago. This attack not only stole customer data but also severely disrupted production and retail operations. The company took proactive measures by shutting down certain systems to enhance security and prevent further threats. Therefore, their decision to resume operations indicates a phased return to normalcy.

The situation reflects the resilience of the automotive sector, underscoring its importance to the UK economy. Following the disruption, the Department for Business and Trade announced a substantial $2 billion loan guarantee. This financial support aims to stabilize JLR’s supply chain, which suffered greatly due to the cyber incident. Moreover, the government recognizes the broader implications of such an attack on an iconic British brand, emphasizing the livelihoods at stake for thousands of workers.

Impact on the Auto Industry

Jaguar Land Rover stands as one of the UK’s top exporters and employers, with roughly 34,000 workers at various sites. Additionally, the company manages a vast supply chain that supports around 120,000 jobs. By resuming production, JLR contributes not just to its own recovery but also to the overall health of the automotive industry. This incident raises awareness about the vulnerabilities that major corporations face in today’s digital age.

The phased restoration of services, which includes addressing inventory backlogs and enhancing supplier relationships, signals a commitment to both immediate recovery and long-term efficacy. With the backing of significant financial resources, JLR aims to emerge stronger. Therefore, their ongoing recovery efforts will likely inspire innovation and bolster confidence in the UK’s automotive sector as a whole.

Discover More Technology Insights

Learn how the Internet of Things (IoT) is transforming everyday life.

Access comprehensive resources on technology by visiting Wikipedia.

Cybersecurity-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleHarrods Data Breach Escalates: 430,000 Customer Records Exposed
Next Article Dutch Teens Caught Assisting Russian Hackers
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Bridging the Critical Confidence Gap in Enterprise AI Security

June 16, 2026

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Comments are closed.

Latest Posts

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

Secure Remote Service. Standardize Access. Strengthen Compliance.

October 19, 2026

AI Threats Are Rising: Enforce Accountability. Trust Nothing.

October 19, 2026
Don't Miss

Bridging the Critical Confidence Gap in Enterprise AI Security

By Staff WriterJune 16, 2026

Summary Points Current AI security testing methods, like tabletop exercises, fail to reveal how AI…

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Three Critical NGINX Flaws Get Emergency Fixes
  • Known Cosmos EVM Flaw Exploited Across Blockchains

  • The Context Layer Enterprise AI Agents Need

  • Secure Remote Service. Standardize Access. Strengthen Compliance.

  • Rank Math PRO Hijacked to Deliver Self-Restoring WordPress Backdoor
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026300 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026214 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026210 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.