
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Global Malware Takedown Exposes 6.4M Stolen Credentials

November 13, 2026

U.S. Seizes North Korean Hack Network After $1.2B Binance Crypto Heist

November 13, 2026

Massive Microsoft 365 Outage Disrupts Exchange, Teams, SharePoint, Copilot & Defender XDR

November 13, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Lawmakers Urge Action on Open-Source Software Risks
Cyber Updates

Lawmakers Urge Action on Open-Source Software Risks

Staff WriterBy Staff WriterDecember 19, 2025No Comments3 Mins Read5 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Top Highlights

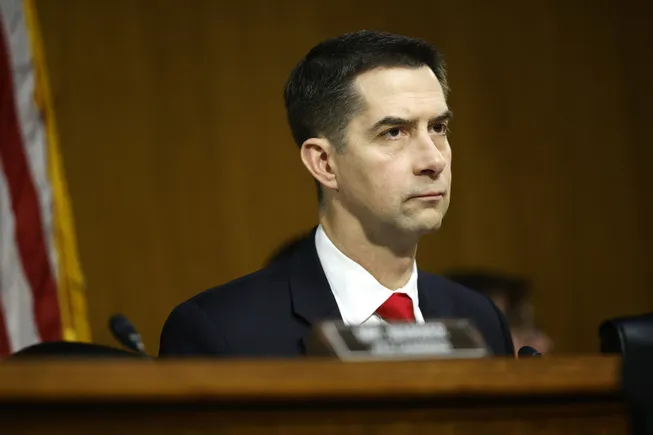
  1. Cybersecurity Risks: Senate Intelligence Committee Chair Tom Cotton warns that U.S. dependence on open-source software (OSS) poses significant cybersecurity risks, especially due to unstable foundations within the OSS ecosystem.

  2. Malicious Code Infiltration: State-sponsored developers are exploiting open-source platforms, inserting harmful code amid an assumed environment of benevolence from contributors, raising alarm over security vulnerabilities.

  3. Request for Action: Cotton urges the National Cyber Director to enhance federal government capabilities for monitoring OSS, focusing on tracking contributions from developers in adversary nations.

  4. Government Commitment: Uncertainty surrounds the Biden-era investment of $11 million in OSS security, with Congressional leaders expressing concern that insufficient measures are being taken to protect the open-source landscape.

Growing Concerns in Cybersecurity

A top Senate Republican recently urged the White House to tackle the rising risks associated with open-source software (OSS). Lawmakers fear that relying on OSS without adequate oversight exposes the nation to significant threats. They highlight troubling incidents, such as the XZ Utils crisis, which revealed vulnerabilities within systems that the military uses for sensitive operations. This situation, alongside concerns over contributions from developers in adversary nations, has fueled anxiety. Notably, foreign developers operating under restrictive laws may compromise software security. Hence, lawmakers stress the need for heightened awareness of OSS provenance and foreign influence.

While open-source software boasts collaborative strength, its decentralized nature poses challenges. State-sponsored actors exploit assumptions of goodwill in this communal environment to insert harmful code. Consequently, Congress is pushing for the federal government to enhance its capabilities in monitoring OSS contributions. The Office of the National Cyber Director has yet to clarify its stance on addressing these concerns. Without addressing these vulnerabilities, the U.S. risks falling behind in cybersecurity preparedness.

A Path Forward for Open-Source Security

Policymakers have long recognized the implications of the nation’s dependence on open-source solutions. Often maintained by volunteers, OSS frequently lacks robust support and funding. Recent events, including vulnerabilities discovered in significant libraries, reignite fears that the government may not have sufficiently fortified the OSS ecosystem. The previous administration’s commitment to investing in open-source security reflects an understanding of its critical role.

Looking ahead, it is essential for the ONCD to reaffirm its focus on open-source software security as a national priority. The tech industry advocates for greater governmental investment, highlighting the need for collaboration between public and private sectors. By addressing these vulnerabilities head-on, the government can contribute positively to the open-source community, ultimately supporting both national security and innovation. Balancing security with the advantages of open-source foundations is vital for the future of technology and cybersecurity.

Discover More Technology Insights

Learn how the Internet of Things (IoT) is transforming everyday life.

Explore past and present digital transformations on the Internet Archive.

Cybersecurity-1
cyber risk cybercrime Cybersecurity MX1 risk management Threats
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleThreat Alert: Cisco VPNs and Email Services Under Attack
Next Article PREMI3NS Achieves SecNumCloud Qualification: Elevating Trusted Cloud Solutions
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Global Malware Takedown Exposes 6.4M Stolen Credentials

November 13, 2026

U.S. Seizes North Korean Hack Network After $1.2B Binance Crypto Heist

November 13, 2026

Massive Microsoft 365 Outage Disrupts Exchange, Teams, SharePoint, Copilot & Defender XDR

November 13, 2026

Comments are closed.

Latest Posts

Global Malware Takedown Exposes 6.4M Stolen Credentials

November 13, 2026

U.S. Seizes North Korean Hack Network After $1.2B Binance Crypto Heist

November 13, 2026

Massive Microsoft 365 Outage Disrupts Exchange, Teams, SharePoint, Copilot & Defender XDR

November 13, 2026

LiteLLM Supply-Chain Attack Steals Credentials, Plants Backdoor

November 13, 2026
Don't Miss

Global Malware Takedown Exposes 6.4M Stolen Credentials

By Staff WriterNovember 13, 2026

Essential Insights Police in nine countries disrupted three malware services under Operation Endgame, seizing 235…

U.S. Seizes North Korean Hack Network After $1.2B Binance Crypto Heist

November 13, 2026

Massive Microsoft 365 Outage Disrupts Exchange, Teams, SharePoint, Copilot & Defender XDR

November 13, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Global Malware Takedown Exposes 6.4M Stolen Credentials

  • U.S. Seizes North Korean Hack Network After $1.2B Binance Crypto Heist
  • Massive Microsoft 365 Outage Disrupts Exchange, Teams, SharePoint, Copilot & Defender XDR
  • Macfinger ClickFix Campaign Deploys DownTheDRAIN macOS Infostealer
  • LiteLLM Supply-Chain Attack Steals Credentials, Plants Backdoor

About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Global Malware Takedown Exposes 6.4M Stolen Credentials

November 13, 2026

U.S. Seizes North Korean Hack Network After $1.2B Binance Crypto Heist

November 13, 2026

Massive Microsoft 365 Outage Disrupts Exchange, Teams, SharePoint, Copilot & Defender XDR

November 13, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026396 Views

Fortinet VPN vulnerability exploited for remote access compromise

June 19, 2026274 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026218 Views

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.