
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Trump AI Order Calls for Voluntary Frontier Model Testing
Compliance

Trump AI Order Calls for Voluntary Frontier Model Testing

Staff WriterBy Staff WriterJune 5, 2026No Comments3 Mins Read5 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Fast Facts

  1. The new executive order prioritizes cybersecurity and encourages voluntary private sector sharing of frontier AI models with the government to enhance early review and security.
  2. It mandates upgrading US systems for AI defense, expediting cyber protections for national security and civilian infrastructure while establishing new federal AI cybersecurity initiatives.
  3. A voluntary framework will enable AI firms to provide early access to models for security review, with incentives to participate and build responsible AI deployment standards.
  4. The order aims to bolster system hardening, create a central AI vulnerability sharing hub, and enforce legal measures against AI-related cyber crimes, fostering collaboration across sectors.

Government Seeks Voluntary Testing of Frontier AI Models

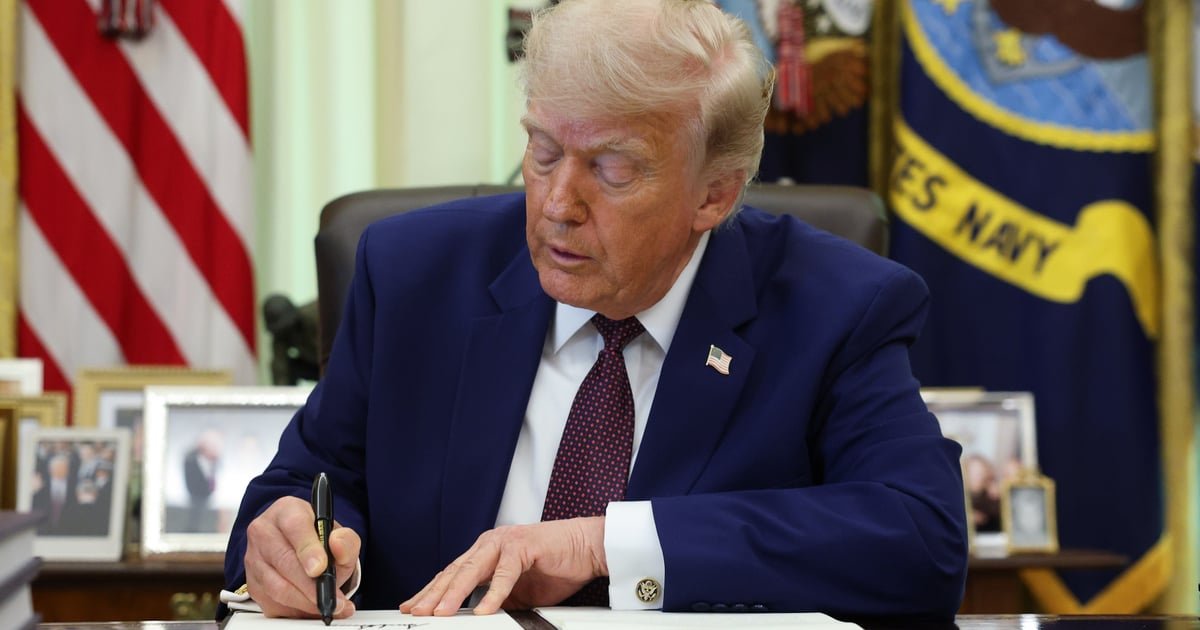
Recently, the White House announced a new executive order aimed at boosting cybersecurity related to artificial intelligence (AI). The order encourages private companies to voluntarily share their advanced AI models with the federal government before public release. This move intends to give government agencies early access to these models, such as Anthropic’s Claude Mythos, which is capable of identifying system vulnerabilities. However, participation remains optional, meaning companies can choose whether to share their models. Experts believe this approach can help spot security concerns early, but the success depends on how well companies and government work together. The order also calls for establishing standards for AI safety and creating a new cybersecurity hub to share information on AI vulnerabilities. Overall, this initiative signals a focus on improving cybersecurity without forcing private sector involvement, hoping to balance innovation with safety.

How the Executive Order Could Change AI and Cybersecurity Practices

The executive order also orders federal agencies, including the Department of Defense and cybersecurity agencies, to prioritize the protection of important systems. It mandates faster sharing of cybersecurity tools and the expansion of programs to defend AI systems against threats. Additionally, there will be efforts to build a dedicated “AI Cybersecurity Clearinghouse” to coordinate responses to AI-related security issues. Companies involved in developing AI models might feel increased pressure to participate, especially since involvement could influence access to government contracts. Experts say that while the voluntary nature of testing creates incentives for participation, it also depends on how well the government and private sector collaborate. For cybersecurity teams, the order emphasizes preparing now by strengthening defenses and integrating AI risk management into their routines, rather than waiting for government-led guidance. This shift indicates a proactive effort to adapt security practices to the evolving AI landscape, aiming to protect critical infrastructure and foster responsible AI development.

Continue Your Tech Journey

Stay informed on the revolutionary breakthroughs in Quantum Computing research.

Stay inspired by the vast knowledge available on Wikipedia.

CyberRisk-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleChinese APT VerdantBamboo Exploits BRICKSTORM Malware to Breach Firewalls and Devices
Next Article Adaptive AI Worms: The Next Enterprise Threat
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

SecTor 2026 Unveils a Rapidly Evolving Cybersecurity Frontier

October 15, 2026

Prioritizing Context Over Scores in Vulnerability Management

October 15, 2026

Yam Store: The Phishing Network Behind a Billion Messages

October 14, 2026

Comments are closed.

Latest Posts

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

Secure Remote Service. Standardize Access. Strengthen Compliance.

October 19, 2026

AI Threats Are Rising: Enforce Accountability. Trust Nothing.

October 19, 2026
Don't Miss

SecTor 2026 Unveils a Rapidly Evolving Cybersecurity Frontier

By Staff WriterOctober 15, 2026

Fast Facts SecTor, Canada’s largest cybersecurity conference, experienced 22% growth, highlighting the rapid evolution of…

Prioritizing Context Over Scores in Vulnerability Management

October 15, 2026

Yam Store: The Phishing Network Behind a Billion Messages

October 14, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Three Critical NGINX Flaws Get Emergency Fixes
  • Known Cosmos EVM Flaw Exploited Across Blockchains

  • The Context Layer Enterprise AI Agents Need

  • Secure Remote Service. Standardize Access. Strengthen Compliance.

  • Rank Math PRO Hijacked to Deliver Self-Restoring WordPress Backdoor
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Three Critical NGINX Flaws Get Emergency Fixes

October 20, 2026

Known Cosmos EVM Flaw Exploited Across Blockchains

October 19, 2026

The Context Layer Enterprise AI Agents Need

October 19, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026300 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026214 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026210 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.