
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

TLP misuse risks data leaks and insider threats

October 10, 2026

FBI Nabs ShinyHunters Suspect Over Jobs Portal Hack

October 10, 2026

Uncovering Vulnerabilities: Practical Strategies to Reduce Identity Risks

October 9, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Critical Pre-Auth Exploit Chains in Commvault Open Door to Remote Code Execution
Uncategorized

Critical Pre-Auth Exploit Chains in Commvault Open Door to Remote Code Execution

Staff WriterBy Staff WriterAugust 21, 2025No Comments2 Mins Read5 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Summary Points

  1. Security Updates Released: Commvault has addressed four critical vulnerabilities in versions prior to 11.36.60 that could enable remote code execution.

  2. Vulnerability Details: Key vulnerabilities include unauthenticated API access (CVE-2025-57788), exploitation of default credentials during installation (CVE-2025-57789), path traversal vulnerabilities (CVE-2025-57790), and input validation issues allowing command-line injection (CVE-2025-57791).

  3. Exploitation Risks: These vulnerabilities could be chained together to achieve unauthorized code execution, particularly if default admin passwords remain unchanged post-installation.

  4. Previous Critical Flaw: This disclosure follows the identification of a severe vulnerability (CVE-2025-34028) by watchTowr Labs, which prompted CISA to include it in their Known Exploited Vulnerabilities catalog.

Commvault Issues Critical Updates to Address Vulnerabilities

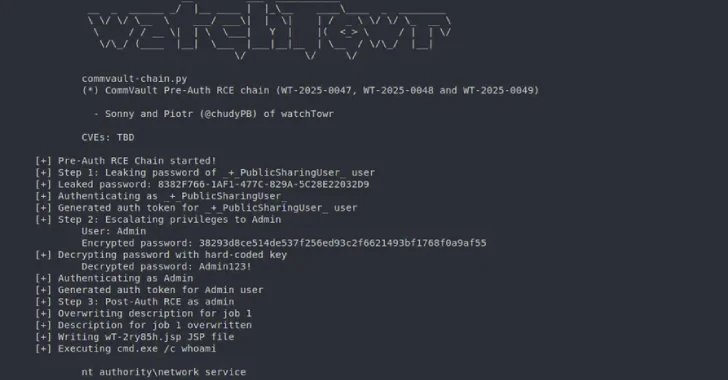
Commvault recently released updates to patch four significant security vulnerabilities. These flaws could allow attackers to execute remote code on vulnerable systems. Notably, these vulnerabilities affect versions prior to 11.36.60. The issues include a problematic login mechanism that enables unauthorized API access (CVE-2025-57788). Additionally, a setup vulnerability allows attackers to exploit default credentials during the initial login phase (CVE-2025-57789). A critical path traversal vulnerability (CVE-2025-57790) permits unauthorized file system access, while another issue enables command-line argument manipulation (CVE-2025-57791). Each of these vulnerabilities has received a Common Vulnerability Scoring System (CVSS) score, indicating their severity.

In April 2025, researchers identified and reported these vulnerabilities, emphasizing their potential risks. Commvault addressed these flaws in versions 11.32.102 and 11.36.60. Importantly, the company’s SaaS solution remains unaffected. The vulnerabilities can be exploited through two pre-authenticated chains, with one reliant on the default admin password remaining unchanged. This news comes after a previous critical flaw (CVE-2025-34028) was flagged, leading to its inclusion in the U.S. Cybersecurity and Infrastructure Security Agency’s Known Exploited Vulnerabilities catalog. With cyber threats evolving continuously, organizations that use Commvault should assess their security posture and implement the latest updates to protect their systems.

Discover More Technology Insights

Dive deeper into the world of Cryptocurrency and its impact on global finance.

Stay inspired by the vast knowledge available on Wikipedia.

DataProtection-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleBalancing Innovation and Security: The AI and Cloud Dilemma
Next Article $50,000 Qilin Ransomware Reward Turned Out to Be Fake
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

FBI Nabs ShinyHunters Suspect Over Jobs Portal Hack

October 10, 2026

China-Linked Hackers Operated Portal Accessing Stolen Emails

October 9, 2026

ARTEX AI: Unmasking Data Theft Attacks on South Korean Financial Firms

October 9, 2026

Comments are closed.

Latest Posts

Malicious Servers Divide Instructions to Force AI Agents to Leak Secrets

October 4, 2026

DeadLock Ransomware Escalates Threats by Exploiting Polygon Smart Contracts

October 1, 2026

Kimwolf v7 Android Botnet: Cloaking DDoS Traffic as Legitimate Browsing

September 28, 2026

Attackers Exploit SharePoint Authentication Bypass Post-PoC Release

September 25, 2026
Don't Miss

FBI Nabs ShinyHunters Suspect Over Jobs Portal Hack

By Staff WriterOctober 10, 2026

Fast Facts The FBI arrested a Canadian citizen suspected of involvement with ShinyHunters, a group…

China-Linked Hackers Operated Portal Accessing Stolen Emails

October 9, 2026

ARTEX AI: Unmasking Data Theft Attacks on South Korean Financial Firms

October 9, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • TLP misuse risks data leaks and insider threats
  • FBI Nabs ShinyHunters Suspect Over Jobs Portal Hack
  • Uncovering Vulnerabilities: Practical Strategies to Reduce Identity Risks
  • Hunt.io Spotlights BraZetsu Evolved Infrastructure Threat
  • AI Power Surge Sparks Cybersecurity M&A Boom
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

TLP misuse risks data leaks and insider threats

October 10, 2026

FBI Nabs ShinyHunters Suspect Over Jobs Portal Hack

October 10, 2026

Uncovering Vulnerabilities: Practical Strategies to Reduce Identity Risks

October 9, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026271 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026214 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026210 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.