

Quick Takeaways
- Michael John Peters, a college-educated art gallery owner from Hawaii, was identified through surveillance footage as a mail thief in Portland, accessing multiple apartment complexes late at night and leaving behind counterfeit postal keys and a Flipper Zero device used for hacking access controls.
- His apartment contained over 170 postal keys, 15 counterfeit identification cards, approximately 300 pieces of mail, gift cards, check printers, and a Flipper Zero device capable of cloning access cards, indicating a sophisticated scheme of identity theft and mail theft.
- Peters had prior convictions for felony possession of identification, fraudulent check use, and credit card theft, and was linked to multiple package deliveries to his Oregon address, suggesting ongoing criminal activity.
- Following a search warrant, authorities arrested Peters, uncovering evidence of identity theft and counterfeiting, and detained him as a serious flight risk due to his criminal history and outstanding warrants.
Underlying Problem
The story centers on Michael John Peters, a seemingly unlikely suspect in a mail theft case in Portland, Oregon, where he is accused of stealing mail from multiple apartment complexes. The USPS identified Peters through surveillance footage showing him entering apartment buildings during odd hours, carrying a backpack, and using keys to access mailboxes. His apartment was found to contain over 170 postal keys, counterfeit identification, stolen mail, and tools like a Flipper Zero, which can clone and gain unauthorized access to secured electronic locks. Watkins, with a criminal history that includes charges related to identity theft, fraud, and possession of false documents, Peters is believed to have orchestrated an elaborate scheme to steal mail and commit identity theft. He was apprehended after investigators linked him to various incidents through video evidence and postal records, leading to a search warrant at his residence. The authorities reported this case, highlighting the extensive evidence that points to Peters’ involvement in mail theft and identity fraud, and he is currently in custody awaiting trial, deemed a flight risk and facing multiple charges.
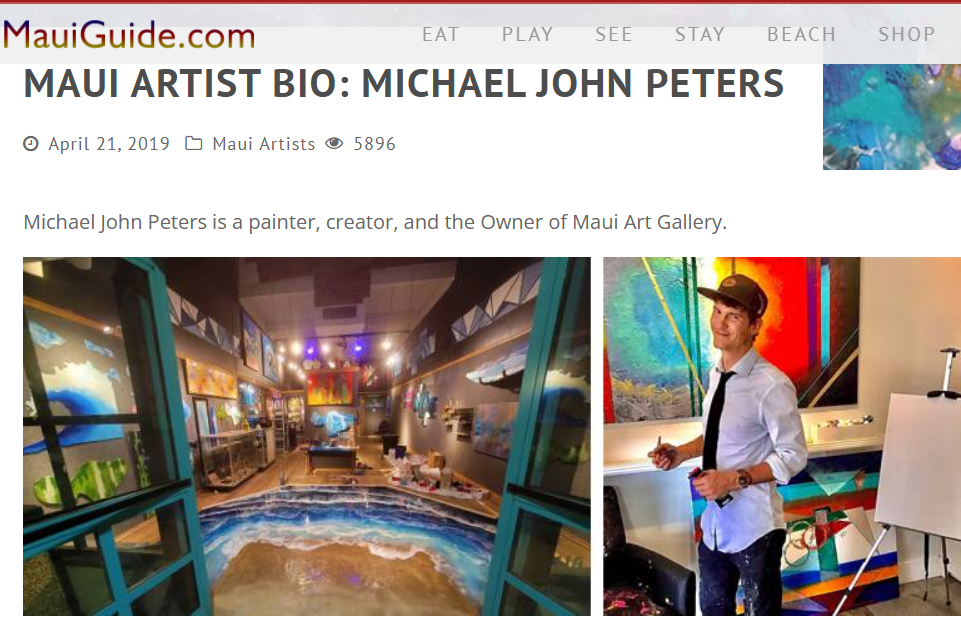
This arrest reveals a surprising deviation from typical mail thieves, as Peters is a college-educated artist who has reinvented himself during the pandemic, creating a unique painting style. The case’s reporting stems from a combination of USPS surveillance, court documents, and media coverage like Oregon Live, emphasizing the meticulous investigation that uncovered Peters’ detailed alleged criminal activities. The investigation illustrates how a seemingly innocuous case of mail theft can unravel into a broader identity theft operation, exposing vulnerabilities in mail security and digital access control systems.
What’s at Stake?
This case underscores the escalating cyber risks associated with physical mail theft and identity fraud, illustrating how digital and physical vulnerabilities intersect to amplify criminal impact. Theft of postal keys, counterfeit identification, and stolen mail—facilitated by advanced tools like the Flipper Zero—highlight how cyber-enabled techniques enable sophisticated and opportunistic criminal activities that threaten personal financial security and undermine trust in the postal system. The extensive collection of mail, fraudulent documents, and stolen identities in Peters’ possession exemplify how cyber and physical risks converge to compromise individual privacy, facilitate broader identity theft schemes, and challenge law enforcement’s ability to combat increasingly complex cyber-physical threats. As such, firms and agencies must intensify security, monitoring, and digital safeguards to mitigate these evolving risks that blend traditional theft with digital manipulation, ultimately impacting financial stability, national security, and public confidence.
Possible Actions
Prompt action in addressing incidents like the arrest of a postal thief in Oregon is crucial to prevent further damage, ensure community safety, and restore public trust in postal services. Swift and effective mitigation measures can help contain risks, recover stolen property, and uphold the integrity of the postal system.
Immediate Response
- Secure and document evidence
- Notify law enforcement authorities
- Coordinate with postal security teams
Public Communication
- Issue press releases
- Inform affected customers
- Provide safety tips
Legal and Disciplinary Actions
- Pursue prosecution thoroughly
- Review and reinforce legal compliance policies
- Suspend or terminate employee privileges if applicable
Operational Improvements
- Implement enhanced security measures (cameras, alarms)
- Increase staff training on theft prevention
- Conduct regular audits and inspections
Prevention Strategies
- Foster community vigilance
- Strengthen internal controls
- Partner with local law enforcement for ongoing surveillance
Continue Your Cyber Journey
Stay informed on the latest Threat Intelligence and Cyberattacks.
Explore engineering-led approaches to digital security at IEEE Cybersecurity.
Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.
Cyberattacks-V1
