

Top Highlights
- Spanish Guardia Civil dismantled the "GXC Team," a cybercrime group led by Brazilian “GoogleXcoder,” responsible for phishing, malware, and voice-scam tools targeting multiple countries.
- The group operated a high-level crime-as-a-service platform offering AI-powered phishing kits, Android malware, and campaign support, creating over 250 phishing sites and intercepting OTPs.
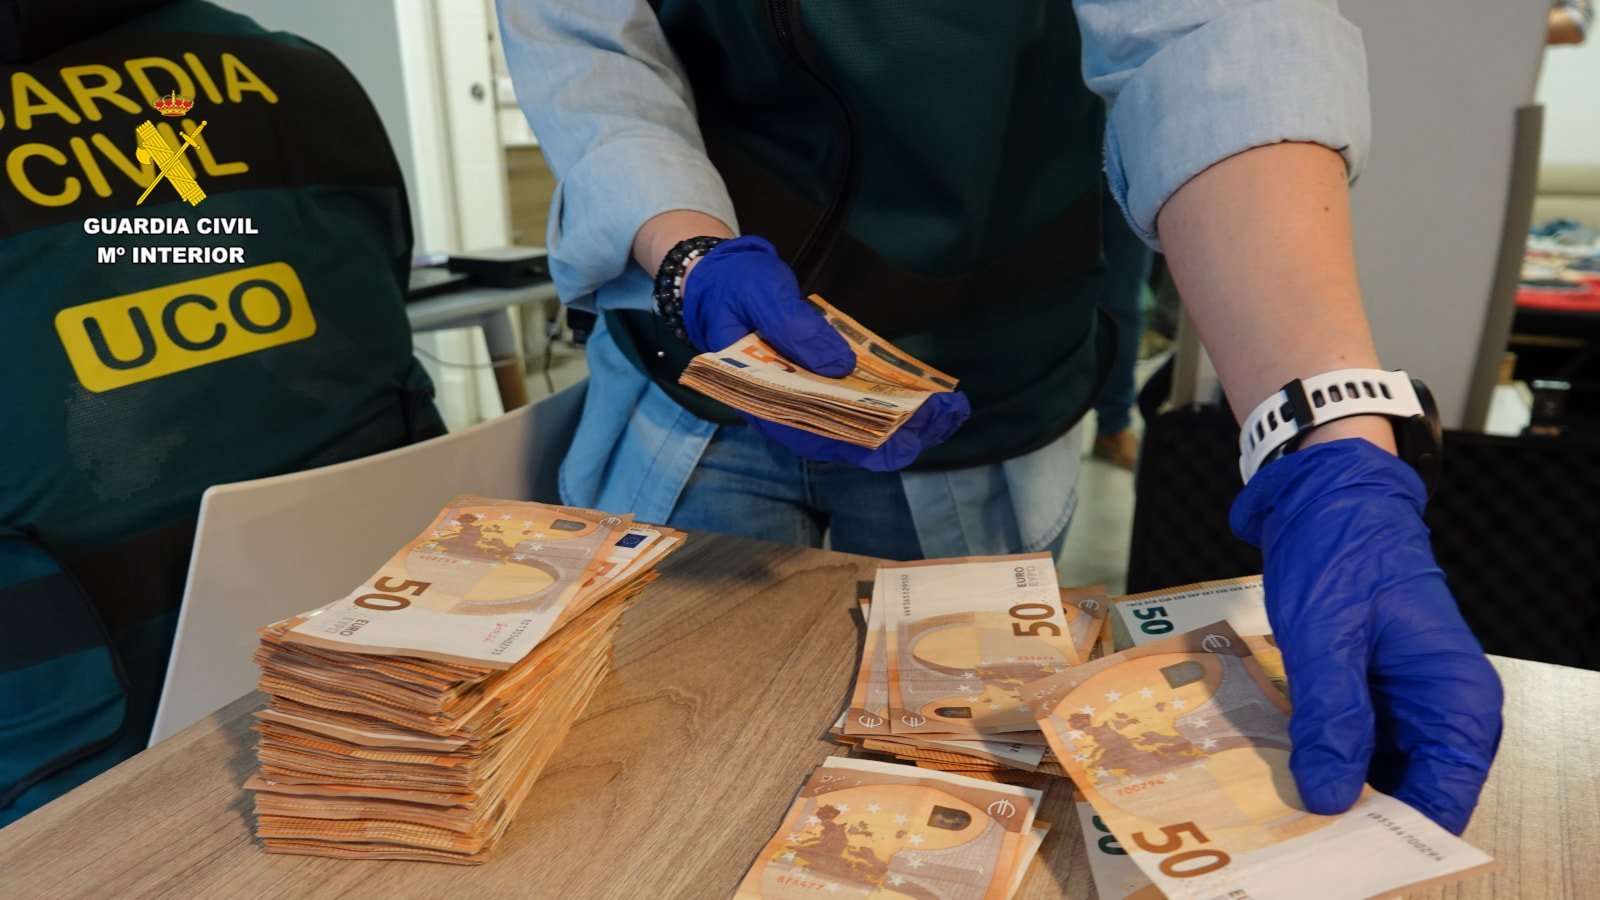
- Police raids across several Spanish cities recovered devices, source code, communications, and financial records, seizing cryptocurrency and shutting down scam-promoting Telegram channels.
- Ongoing investigations, aided by forensic analysis and transaction tracking of the arrested leader, could lead to more arrests and reveal a broader criminal network.
What’s the Problem?
The Spanish Guardia Civil, in a significant crackdown on cybercrime, successfully dismantled the notorious “GXC Team,” a sophisticated operation responsible for extensive phishing and malware campaigns across multiple countries, including Spain, the UK, the US, and Brazil. Led by a 25-year-old Brazilian known as “GoogleXcoder,” this group functioned as a crime-as-a-service platform, providing AI-driven phishing kits, Android malware, and voice-scam tools via Telegram and Russian-language hacker forums to facilitate credential theft and financial fraud. The law enforcement’s meticulous investigation—spanning over a year—utilized device analysis and cryptocurrency tracking to unveil the complex network behind the crime, leading to numerous arrests and seizure of evidence like source codes and financial documents during coordinated raids targeting various Spanish cities. The report, issued by the Guardia Civil, highlights the scale and danger of this operation, including the seizure of cryptocurrency stolen from victims and the shutdown of criminal channels, while indicating ongoing efforts to apprehend additional members involved.
The report underscores the extensive reach and technical sophistication of the GXC Team’s activities, which included creating more than nine types of Android malware to hijack accounts and intercept passwords, and deploying at least 250 phishing sites ominously mimicking reputable institutions. As authorities continue their investigation, the case reveals the alarming scope of cybercrime-as-a-service architectures that enable cybercriminals to operate with high efficiency and minimal risk, prompting concerns about future threats and the need for ongoing vigilance and advanced cybersecurity measures.
Risk Summary
The dismantling of the GXC Team by Spanish law enforcement underscores the profound security threats posed by sophisticated cybercriminal operations that leverage AI-enhanced tools for extensive financial and data breaches. Operating a crime-as-a-service platform, the group specialized in phishing, Android malware, and voice scams targeted across multiple countries, jeopardizing banks, e-commerce, and transport sectors by replicating trusted websites and intercepting one-time passwords through malicious Android strains. Their operations not only facilitated massive credential theft but also demonstrated the alarming capacity of cybercriminals to offer technical support and customization, thus amplifying their reach and effectiveness. The seizure of source code, digital communications, and stolen cryptocurrency reveals a meticulously organized network capable of sustaining complex, prolonged campaigns. This case highlights how such operations exploit digital anonymity and technological vulnerabilities, causing significant financial losses, erosion of trust in digital services, and emphasizing the urgent need for robust, AI-enabled security measures to counteract these evolving threats.
Possible Remediation Steps
Early intervention in tackling cybercrime syndicates like the dismantling of the "GXC Team" is crucial to prevent further illegal activities, safeguard sensitive information, and maintain public confidence in digital security. Prompt remediation ensures that vulnerabilities are addressed swiftly, reducing potential damages and deterring future cybercriminal endeavors.
Mitigation Strategies:
- Conduct comprehensive system audits to identify vulnerabilities.
- Strengthen network defenses with updated firewalls and anti-malware tools.
- Implement regular security training for staff to recognize phishing and social engineering tactics.
- Increase monitoring and anomaly detection to identify suspicious activities.
- Ensure timely software and security patch updates to close exploited entry points.
Remediation Steps:
- Isolate affected systems to prevent further intrusion.
- Perform thorough forensic analysis to understand breach scope and origin.
- Reset compromised credentials and reinforce access controls.
- Collaborate with law enforcement to gather intelligence and track cybercriminal operations.
- Communicate transparently with stakeholders and affected users about the incident and remediation efforts.
Explore More Security Insights
Stay informed on the latest Threat Intelligence and Cyberattacks.
Explore engineering-led approaches to digital security at IEEE Cybersecurity.
Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.
Cyberattacks-V1
