
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

F5 BIG-IP APM Zero-Day Enables Unauthenticated Remote Exploits

September 23, 2026

ShinyHunters Claims Data on FBI Agents and Job Applicants Stolen

September 23, 2026

Macfinger ClickFix exploits browser vulnerabilities via phishing.

September 23, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Revolutionizing Cybersecurity: The Future of Worldwide Extended Detection and Response (XDR) in 2025
Cybercrime and Ransomware

Revolutionizing Cybersecurity: The Future of Worldwide Extended Detection and Response (XDR) in 2025

Staff WriterBy Staff WriterSeptember 29, 2025No Comments4 Mins Read7 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Quick Takeaways

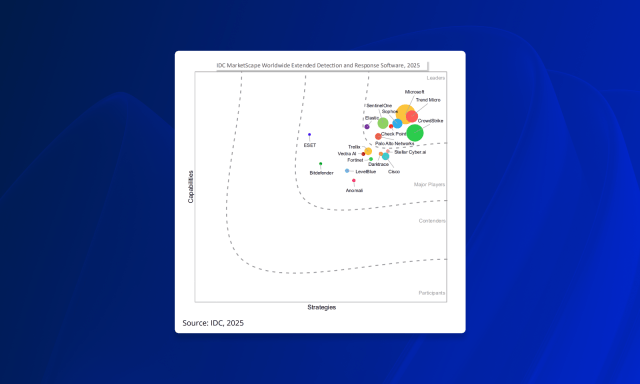
  1. Sophos has been recognized as a Leader in the IDC MarketScape™: Worldwide Extended Detection and Response (XDR) Software 2025, underscoring its commitment to scalable, intelligent security solutions.
  2. The report praises Sophos’ protection capabilities, including standard features like host firewalls, IDS/IPS, device control, and encryption, alongside proactive defense tools such as Adaptive Attack Protection (‘Shields Up’).
  3. Sophos XDR integrates AI-driven threat detection, automated defenses, and extensive ecosystem flexibility, enabling rapid threat investigation, response, and seamless integration across diverse IT environments.
  4. The acquisition of Secureworks enhances Sophos’ platform, providing combined prevention, detection, and response, with plans for full integration into the Sophos Central platform, further strengthening industry trust and future innovation.

What’s the Problem?

In a recent industry report by IDC MarketScape™, Sophos has been recognized as a leader in the field of Extended Detection and Response (XDR) software for 2025, reflecting its strong reputation for innovative and comprehensive cybersecurity solutions. The report praises Sophos for its robust protection features, which include firewalls, intrusion detection, device control, and encryption, all integrated into its platform, alongside advanced proactive defenses like Adaptive Attack Protection, introduced in 2023, that automatically activate in the face of active threats. This recognition is based on Sophos’ ability to deliver scalable and intelligent security measures suitable for organizations of all sizes, enabled further by the recent integration of the Taegis XDR platform, which enhances its capabilities and speeds up the development of new features.

The report highlights that Sophos’ XDR platform effectively combines AI-driven automation, real-time threat insights, and a unified view of an organization’s entire IT environment—covering endpoints, cloud workloads, and identity layers—making it adaptable for both beginners and cybersecurity experts. The recent acquisition and integration of Secureworks, which now allows for combined prevention, detection, and response within a single platform, marks a significant milestone, strengthening protection while reducing costs. This industry validation underscores Sophos’ reputation as a trusted leader, committed to shaping the future of cybersecurity with continuous innovation, particularly as it plans to fully embed Taegis XDR into its broader platform to better serve a diverse global client base.

Potential Risks

Sophos, recognized as a Leader in the IDC MarketScape™ for Extended Detection and Response (XDR) Software 2025, exemplifies a comprehensive approach to cyber security by integrating advanced threat detection, AI-driven investigation, and adaptive defenses across diverse digital environments. Cyber risks, including sophisticated malware, insider threats, and zero-day exploits, pose significant challenges, potentially leading to data breaches, operational disruptions, and costly reputational damage. Sophos addresses these risks through robust protection features like host-based firewalls, IDS/IPS, endpoint encryption, and proactive threat mitigation such as ‘Shields Up’ Adaptive Attack Protection, which activates defenses during active attacks. Its open platform and recent acquisition of Secureworks enable seamless integration with existing IT infrastructures, offering real-time insights, automated responses, and deep visibility into identity and cloud environments. This integrated, scalable approach minimizes attack surfaces, accelerates threat neutralization, and reduces operational complexity, thereby safeguarding organizational assets and maintaining trust amidst an evolving threat landscape.

Possible Remediation Steps

Ensuring prompt and effective remediation is crucial in addressing vulnerabilities within worldwide Extended Detection and Response (XDR) software by 2025, as delays can lead to severe security breaches, data loss, and financial repercussions. Rapid response not only minimizes damage but also reinforces the resilience and trustworthiness of cybersecurity infrastructure in an increasingly interconnected digital landscape.

Mitigation Steps:

  • Immediate patch deployment
  • Software updates installation
  • Security configuration review

Remediation Actions:

  • Incident isolation and containment
  • Malware removal procedures
  • Systems and network scans
  • User access controls tightening
  • Incident documentation and reporting

Stay Ahead in Cybersecurity

Stay informed on the latest Threat Intelligence and Cyberattacks.

Access world-class cyber research and guidance from IEEE.

Disclaimer: The information provided may not always be accurate or up to date. Please do your own research, as the cybersecurity landscape evolves rapidly. Intended for secondary references purposes only.

Cyberattacks-V1

CISO Update Cybersecurity MX1
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleJapan’s Largest Brewer Halts Operations Amid Cyberattack
Next Article Harrods Data Breach Packs a Punch: 430,000 Customers Compromised
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

F5 BIG-IP APM Zero-Day Enables Unauthenticated Remote Exploits

September 23, 2026

ShinyHunters Claims Data on FBI Agents and Job Applicants Stolen

September 23, 2026

Macfinger ClickFix exploits browser vulnerabilities via phishing.

September 23, 2026

Comments are closed.

Latest Posts

Apple Alerts: 110 Countries at Risk of Spyware Attacks

September 22, 2026

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Suspected China-Linked Group Exploits VMware Flaw to Launch Babuk Ransomware

September 16, 2026

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026
Don't Miss

F5 BIG-IP APM Zero-Day Enables Unauthenticated Remote Exploits

By Staff WriterSeptember 23, 2026

Summary Points Attackers can exploit CVE-2026-94127 to perform remote code execution on F5 BIG-IP systems…

ShinyHunters Claims Data on FBI Agents and Job Applicants Stolen

September 23, 2026

Macfinger ClickFix exploits browser vulnerabilities via phishing.

September 23, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • F5 BIG-IP APM Zero-Day Enables Unauthenticated Remote Exploits
  • ShinyHunters Claims Data on FBI Agents and Job Applicants Stolen
  • Macfinger ClickFix exploits browser vulnerabilities via phishing.
  • Is AI the Solution to Your Overburdened Security Team?
  • Apple Alerts: 110 Countries at Risk of Spyware Attacks
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

F5 BIG-IP APM Zero-Day Enables Unauthenticated Remote Exploits

September 23, 2026

ShinyHunters Claims Data on FBI Agents and Job Applicants Stolen

September 23, 2026

Macfinger ClickFix exploits browser vulnerabilities via phishing.

September 23, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026208 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026205 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026203 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.