

Summary Points
-
Security Updates Released: Commvault has addressed four critical vulnerabilities in versions prior to 11.36.60 that could enable remote code execution.
-
Vulnerability Details: Key vulnerabilities include unauthenticated API access (CVE-2025-57788), exploitation of default credentials during installation (CVE-2025-57789), path traversal vulnerabilities (CVE-2025-57790), and input validation issues allowing command-line injection (CVE-2025-57791).
-
Exploitation Risks: These vulnerabilities could be chained together to achieve unauthorized code execution, particularly if default admin passwords remain unchanged post-installation.
- Previous Critical Flaw: This disclosure follows the identification of a severe vulnerability (CVE-2025-34028) by watchTowr Labs, which prompted CISA to include it in their Known Exploited Vulnerabilities catalog.
Commvault Issues Critical Updates to Address Vulnerabilities
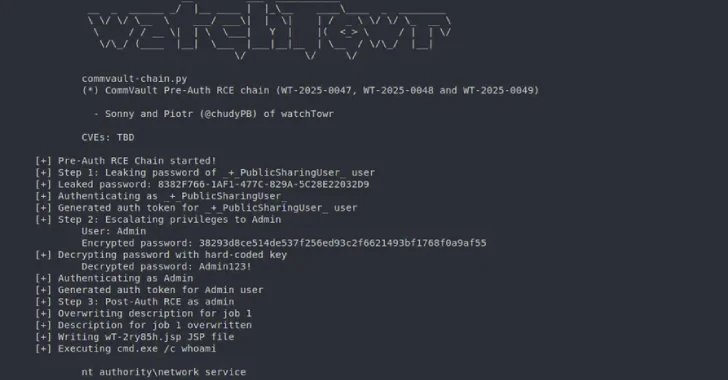
Commvault recently released updates to patch four significant security vulnerabilities. These flaws could allow attackers to execute remote code on vulnerable systems. Notably, these vulnerabilities affect versions prior to 11.36.60. The issues include a problematic login mechanism that enables unauthorized API access (CVE-2025-57788). Additionally, a setup vulnerability allows attackers to exploit default credentials during the initial login phase (CVE-2025-57789). A critical path traversal vulnerability (CVE-2025-57790) permits unauthorized file system access, while another issue enables command-line argument manipulation (CVE-2025-57791). Each of these vulnerabilities has received a Common Vulnerability Scoring System (CVSS) score, indicating their severity.
In April 2025, researchers identified and reported these vulnerabilities, emphasizing their potential risks. Commvault addressed these flaws in versions 11.32.102 and 11.36.60. Importantly, the company’s SaaS solution remains unaffected. The vulnerabilities can be exploited through two pre-authenticated chains, with one reliant on the default admin password remaining unchanged. This news comes after a previous critical flaw (CVE-2025-34028) was flagged, leading to its inclusion in the U.S. Cybersecurity and Infrastructure Security Agency’s Known Exploited Vulnerabilities catalog. With cyber threats evolving continuously, organizations that use Commvault should assess their security posture and implement the latest updates to protect their systems.
Discover More Technology Insights
Dive deeper into the world of Cryptocurrency and its impact on global finance.
Stay inspired by the vast knowledge available on Wikipedia.
DataProtection-V1
