
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

AI fuels rise in multi-stage cyber attack techniques

October 6, 2026

Rise of RMM Tools in Active Cyberattacks

October 6, 2026

Vasileios Mingos to strengthen EU critical infrastructure cyber defenses

October 6, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Jaguar Land Rover Extends Production Halt into October After Cyberattack
Cyber Updates

Jaguar Land Rover Extends Production Halt into October After Cyberattack

Staff WriterBy Staff WriterSeptember 23, 2025Updated:October 25, 2025No Comments3 Mins Read6 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Quick Takeaways

  1. Production Delay Extended: Jaguar Land Rover has extended its production halt until October 1 due to a severe cyberattack, following an initial pause announced on September 2.

  2. Safety Measures in Place: The company is collaborating with cybersecurity experts and law enforcement to ensure a secure and phased restart of operations.

  3. Union Concerns: The Unite union has urged U.K. authorities to implement a furlough plan to support impacted workers, although JLR has not specified the reasons for the further production delay.

  4. Hackers Identified: The threat group Scattered Spider has claimed responsibility for the attack, which has affected other major U.K. retailers, prompting investigations by U.S. and U.K. law enforcement.

Cyberattack Fallout: Jaguar Land Rover’s Extended Production Halt

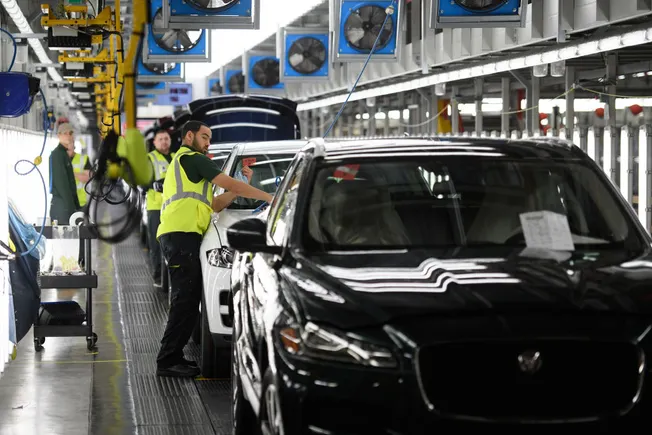
Jaguar Land Rover (JLR) recently announced an extension of its production pause until October 1. This decision follows a cyberattack that forced the luxury automaker to halt operations weeks ago. In a statement, the company aimed to provide clarity during this uncertain time. At present, JLR works tirelessly with cybersecurity professionals and law enforcement to ensure a safe restart of production.

Initially, JLR revealed the cyberattack on September 2, when a threat group infiltrated company data, causing significant disruptions. The initial plan was to resume operations by September 24. However, the need for a longer pause highlights the complexities associated with such security breaches. The Unite union has voiced concerns about job security for the thousands of workers impacted, urging U.K. authorities to assist with a furlough plan.

Wider Implications and Industry Response

The attack on JLR underscores a growing trend in cyber threats affecting major corporations, particularly in the automotive sector. A group named Scattered Spider claimed responsibility for the attack, following a series of similar strikes on prominent retailers. As investigations continue in both the U.K. and the U.S., companies need to take these threats seriously.

Moreover, JLR is not alone in facing cybersecurity challenges. Stellantis reported a separate incident involving the theft of customer data from a third-party service provider. Although the stolen information was limited to contact details, it serves as a reminder for consumers to remain vigilant. For instance, Stellantis advised its customers to avoid suspicious links and only use official communication channels. As the automotive industry grapples with these challenges, fostering a secure digital environment becomes crucial for both companies and consumers alike.

Continue Your Tech Journey

Learn how the Internet of Things (IoT) is transforming everyday life.

Access comprehensive resources on technology by visiting Wikipedia.

Cybersecurity-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleShadowV2 Botnet Uses Misconfigured AWS Docker Containers for DDoS Attacks
Next Article Unseen Threats: Many Cyber Breaches Go Unreported
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Bridging the Critical Confidence Gap in Enterprise AI Security

June 16, 2026

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Comments are closed.

Latest Posts

Malicious Servers Divide Instructions to Force AI Agents to Leak Secrets

October 4, 2026

DeadLock Ransomware Escalates Threats by Exploiting Polygon Smart Contracts

October 1, 2026

Kimwolf v7 Android Botnet: Cloaking DDoS Traffic as Legitimate Browsing

September 28, 2026

Attackers Exploit SharePoint Authentication Bypass Post-PoC Release

September 25, 2026
Don't Miss

Bridging the Critical Confidence Gap in Enterprise AI Security

By Staff WriterJune 16, 2026

Summary Points Current AI security testing methods, like tabletop exercises, fail to reveal how AI…

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • AI fuels rise in multi-stage cyber attack techniques
  • Rise of RMM Tools in Active Cyberattacks
  • Vasileios Mingos to strengthen EU critical infrastructure cyber defenses
  • Denmark: 8.8 Million People’s CPR Data Compromised in Breach
  • Rapid7 unveils threat data platform targeting cyberattack tactics
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

AI fuels rise in multi-stage cyber attack techniques

October 6, 2026

Rise of RMM Tools in Active Cyberattacks

October 6, 2026

Vasileios Mingos to strengthen EU critical infrastructure cyber defenses

October 6, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026255 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026214 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026210 Views

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.