
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Malicious npm Package Exfiltrates Credentials via Twilio Probe

September 22, 2026

Microsoft and Google disrupt RedVDS cybercrime marketplace.

September 22, 2026

CAIRN Detects AI-Driven Malware via Frontier Tracking

September 22, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Europol-coordinated global operation takes down pro-Russian cybercrime network
Uncategorized

Europol-coordinated global operation takes down pro-Russian cybercrime network

Staff WriterBy Staff WriterJuly 17, 2025No Comments3 Mins Read11 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email


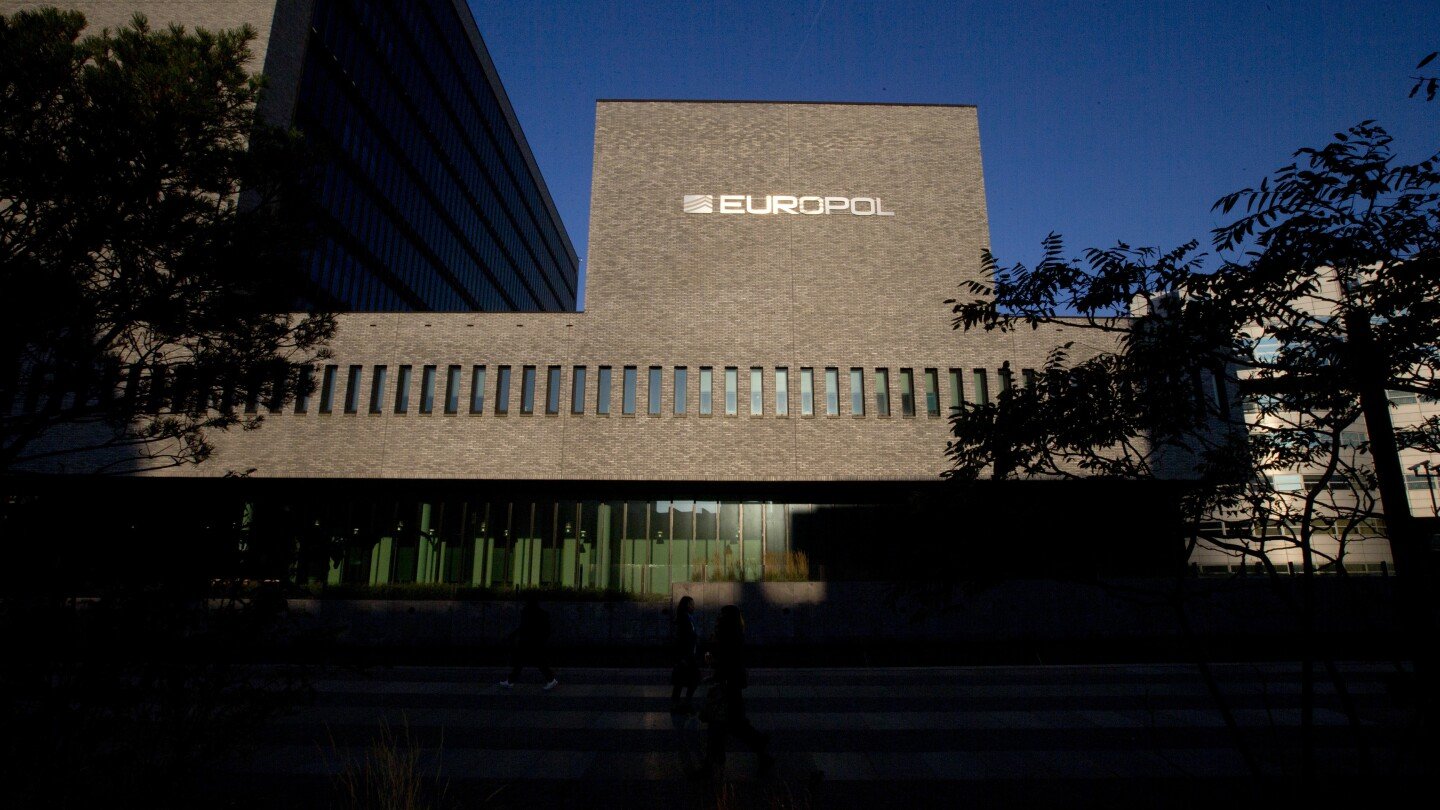
THE HAGUE, Netherlands (AP) — A coordinated international operation has hit the infrastructure of a pro-Russian cybercrime network linked to a string of denial of service attacks targeting Ukraine and its allies, the European Union’s police agency Europol announced Wednesday.

Codenamed Eastwood, the operation targeted the so-called NoName057(16) group, which was identified last month by Dutch authorities as being behind a series of denial-of-service attacks on several municipalities and organizations linked to a NATO summit in the Netherlands.

Europol said that the cybercrime network was also involved in attacks in Sweden, Germany and Switzerland.

The police agency said the international operation “led to the disruption of an attack-infrastructure consisting of over one hundred computer systems worldwide, while a major part of the group’s central server infrastructure was taken offline.”

Law enforcement and judicial authorities from France, Finland, Germany, Italy, Lithuania, Poland, Spain, Sweden, Switzerland, the Czech Republic, the Netherlands and the United States took simultaneous actions against offenders and infrastructure belonging to the pro-Russian cybercrime network, it said.

Western officials have accused Russia and its proxies of staging dozens of attacks, sabotage attempts and other incidents across Europe since the invasion of Ukraine, including cyberattacks. The Associated Press is tracking them in a detailed map that shows the breadth of efforts to sow division in European societies and undermine support for Ukraine.

As part of the latest operation, judicial authorities in Germany issued six arrest warrants for suspects in Russia, two of them accused of being the main leaders of the group, Europol said. Five of them were identified on Europol’s Europe’s Most Wanted website.

One suspect was placed under preliminary arrest in France and another detained in Spain, Europol said. The Paris prosecutor’s office said one person is in custody in France and communications equipment has been seized. No charges have yet been filed. In the United States, the Federal Bureau of Investigation was involved in the operation.

The attorney general’s office in Switzerland, which is not an EU member country, said in a statement Wednesday that joint investigations between Europol and Swiss federal police helped identify three leading members of the group, which is alleged to have targeted more than 200 Swiss websites.

Swiss prosecutors opened a criminal case over the incidents in June 2023, and since then identified several other denial-of-service attacks attributed to the activist group. The attacks included a video address by Ukrainian President Volodymyr Zelenskyy to the Swiss parliament and the popular Eurovision Song Contest, held in in Basel earlier this year.

Europol said members of the cybercrime group initially targeted Ukrainian institutions, “but have shifted their focus to attacking countries that support Ukraine in the ongoing defence against the Russian war of aggression, many of which are members of NATO.”

Law enforcement authorities in countries involved in the operation contacted hundreds of people believed to support the group to inform them of the crackdown and their alleged liability for its actions.

“Individuals acting for NoName057(16) are mainly Russian-speaking sympathisers who use automated tools to carry out distributed denial-of-service (DDoS) attacks. Operating without formal leadership or sophisticated technical skills, they are motivated by ideology and rewards,” Europol said.

It added that people recruited by the group were paid in cryptocurrency and motivated using online-gaming dynamics like leader boards and badges.

“This gamified manipulation, often targeted at younger offenders, was emotionally reinforced by a narrative of defending Russia or avenging political events,” Europol said.

___

Associated Press writers Jamey Keaten in Geneva, Geir Moulson in Berlin and Angela Charlton in Paris contributed.


Source link

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleBrian Krebs, Phil Venables and Alissa Knight Lead Keynote Speaker Lineu
Next Article Cyberhaven Appoints James McCarthy SVP Sales to Drive Growth
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies

September 19, 2026

Gyazo Breach Exposes Over 23 Million User Records and Nearly 500 Million Image Metadata Entries

September 17, 2026

Russian State Hackers Rebuild Malware Using Claude After Detection

September 11, 2026
Leave A Reply Cancel Reply

Latest Posts

Urgent: Exploitation of SAP Commerce Cloud CVE-2026-58231 Sparks Immediate Threat

September 19, 2026

Suspected China-Linked Group Exploits VMware Flaw to Launch Babuk Ransomware

September 16, 2026

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026

TWINLOOT Exploits SharePoint and Teams to Steal Credentials and Lateral Movement

September 10, 2026
Don't Miss

CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies

By Staff WriterSeptember 19, 2026

Essential Insights CrowdSec’s private GitHub repositories were copied by an attacker using an employee’s compromised…

Gyazo Breach Exposes Over 23 Million User Records and Nearly 500 Million Image Metadata Entries

September 17, 2026

Russian State Hackers Rebuild Malware Using Claude After Detection

September 11, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Malicious npm Package Exfiltrates Credentials via Twilio Probe
  • Microsoft and Google disrupt RedVDS cybercrime marketplace.
  • CAIRN Detects AI-Driven Malware via Frontier Tracking
  • SideCopy uses reverse RAT spear-phishing to target Indian academia
  • Hidden meta settings enable AI backdoor exploitation
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Malicious npm Package Exfiltrates Credentials via Twilio Probe

September 22, 2026

Microsoft and Google disrupt RedVDS cybercrime marketplace.

September 22, 2026

CAIRN Detects AI-Driven Malware via Frontier Tracking

September 22, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026205 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026204 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026202 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.