
Close Menu
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

What's Hot

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026

CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies

September 19, 2026
Facebook X (Twitter) Instagram
The CISO Brief
  • Home
  • Cybercrime and Ransomware
  • Emerging Tech
  • Threat Intelligence
  • Expert Insights
  • Careers and Learning
  • Compliance
Home » Nation-State Hackers Breach F5 Systems, Steal Customer Data
Cyber Updates

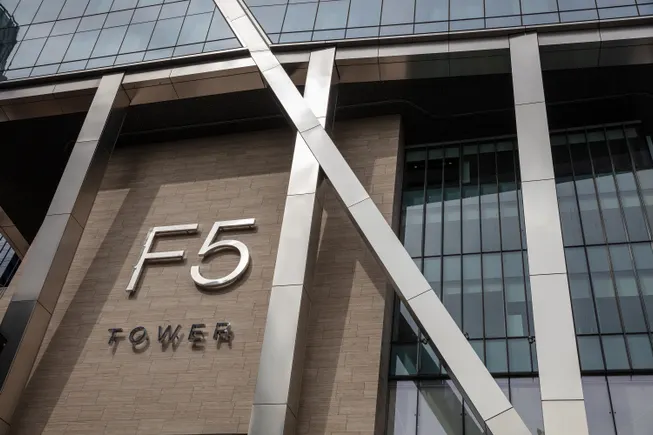
Nation-State Hackers Breach F5 Systems, Steal Customer Data

Staff WriterBy Staff WriterOctober 15, 2025Updated:October 25, 2025No Comments3 Mins Read7 Views
Facebook Twitter Pinterest LinkedIn Tumblr Email
Share
Facebook Twitter LinkedIn Pinterest WhatsApp Email

Summary Points

  1. Breach of Security: Government-backed hackers accessed F5’s production environment, stealing files, including source code and information on vulnerabilities related to their BIG-IP platform.

  2. Long-standing Access: F5 reported that the attackers maintained long-term access to their systems, discovering the breach in August without specifying the attack’s start date.

  3. CISA Response: The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued an emergency directive, mandating federal agencies to identify affected devices and implement security updates by specified deadlines.

  4. Potential Consequences: Concerns escalate over downstream impacts on F5’s government and private-sector customers, highlighting risks similar to the SolarWinds espionage campaign, as hackers could exploit vulnerabilities for broader network access.

Understanding the Breach

Government-backed hackers recently accessed F5 systems, a well-known enterprise technology provider. They infiltrated sensitive environments, specifically targeting F5’s engineering resource portal. This breach allowed hackers to steal critical files, including some source code for F5’s BIG-IP platform. According to F5, these files contained information about undisclosed vulnerabilities, although the company assured that none of these posed critical risks. Still, the stolen data could help malicious actors devise tailored attacks on certain F5 customers.

Moreover, F5 reported that the attackers maintained long-term access to its systems before the breach was discovered in August. The exact timeline remains unclear, raising concerns about the extent of this intrusion. As federal agencies scramble to determine potential impacts on their systems, swift actions are necessary to mitigate risks. Agencies must identify vulnerable devices, remove management interfaces from the public internet, and apply all necessary security updates before deadlines set by CISA.

Wider Implications

This incident draws unsettling parallels to prior high-profile cybersecurity breaches, like Russia’s SolarWinds campaign. Both highlight the vulnerabilities within supply chains and the potential consequences for national security and private industries. Countless F5 products are currently in use across federal agencies, intensifying the need for immediate and coordinated responses.

While F5 claims no alteration occurred to their software supply chain, the anxieties surrounding potential downstream effects remain palpable. Such breaches expose organizations to further risks, including data theft and exploitation of consumer trust. CISA continues to work closely with various sectors to warn about vulnerabilities, stressing the need for heightened vigilance in cybersecurity practices.

As dependency on technology grows, so do the not-so-subtle threats posed by nation-state actors. Understanding these risks is crucial for businesses and government agencies alike as they navigate the complexities of modern cybersecurity.

Stay Ahead with the Latest Tech Trends

Explore the future of technology with our detailed insights on Artificial Intelligence.

Access comprehensive resources on technology by visiting Wikipedia.

Cybersecurity-V1

Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleFake Password Alerts Trigger PC Hijacks via LastPass and Bitwarden Breach Scams
Next Article Capita to Pay £14M Over Data Breach Affecting 6.6 Million People
Avatar photo
Staff Writer
  • Website

John Marcelli is a staff writer for the CISO Brief, with a passion for exploring and writing about the ever-evolving world of technology. From emerging trends to in-depth reviews of the latest gadgets, John stays at the forefront of innovation, delivering engaging content that informs and inspires readers. When he's not writing, he enjoys experimenting with new tech tools and diving into the digital landscape.

Related Posts

Bridging the Critical Confidence Gap in Enterprise AI Security

June 16, 2026

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Comments are closed.

Latest Posts

Suspected China-Linked Group Exploits VMware Flaw to Launch Babuk Ransomware

September 16, 2026

CISA Flags Critical Ray Flaw for Browser-Based RCE Exploits

September 13, 2026

TWINLOOT Exploits SharePoint and Teams to Steal Credentials and Lateral Movement

September 10, 2026

Windchill Web Shell Exposes Credentials and Maps Engineering Data

September 7, 2026
Don't Miss

Bridging the Critical Confidence Gap in Enterprise AI Security

By Staff WriterJune 16, 2026

Summary Points Current AI security testing methods, like tabletop exercises, fail to reveal how AI…

Legal Industry VPNs: Falling to Modern Threats

June 15, 2026

Closing the Gap: The Rising Threat of Third-Party Privileged Access

June 14, 2026

Subscribe to Updates

Subscribe to our newsletter and never miss our latest news

Subscribe my Newsletter for New Posts & tips Let's stay updated!

Recent Posts

  • Mastering Security: The One-Incident Test for Unified Platform Evaluation
  • GISEC 2026: Quantum, AI escalate cyberattack sophistication
  • CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies
  • SolarWinds ARM Hard-Coded Key Enables RCE Exploitation
  • Blockchain malware surge exploits smart contract vulnerabilities
About Us
About Us

Welcome to The CISO Brief, your trusted source for the latest news, expert insights, and developments in the cybersecurity world.

In today’s rapidly evolving digital landscape, staying informed about cyber threats, innovations, and industry trends is critical for professionals and organizations alike. At The CISO Brief, we are committed to providing timely, accurate, and insightful content that helps security leaders navigate the complexities of cybersecurity.

Facebook X (Twitter) Pinterest YouTube WhatsApp
Our Picks

Mastering Security: The One-Incident Test for Unified Platform Evaluation

September 19, 2026

GISEC 2026: Quantum, AI escalate cyberattack sophistication

September 19, 2026

CrowdSec Reveals NPM Attack Resulted in 170 Private GitHub Repo Copies

September 19, 2026
Most Popular

Gefährliche Angriffe: Wie Cyberkriminelle Ihre Identität angreifen

January 29, 2026198 Views

CISA Alerts: Critical Vulnerability in Splunk Enterprise Under Active Attack

June 19, 2026197 Views

Salesforce Disables Klue App After Data Breach from Token Abuse

June 19, 2026195 Views

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025

Categories

  • Compliance
  • Cyber Updates
  • Cybercrime and Ransomware
  • Editor's pick
  • Emerging Tech
  • Events
  • Featured
  • Insights
  • Most Read
  • Threat Intelligence
  • Uncategorized
© 2026 thecisobrief. Designed by thecisobrief.
  • Home
  • About Us
  • Advertise with Us
  • Contact Us
  • DMCA
  • Privacy Policy
  • Terms & Conditions

Type above and press Enter to search. Press Esc to cancel.